providingpermissiondenied
permissiondenied 时间:2021-03-17 阅读:()
CopyrightIBMCorporation2009TrademarksSecureLinuxcontainerscookbookPage1of12SecureLinuxcontainerscookbookStrengthenlightweightcontainerswithSELinuxandSmackSergeE.
HallynFebruary03,2009Lightweightcontainers,otherwiseknownasVirtualPrivateServers(VPS)orJails,areoftenthoughtofasasecuritytoolsdesignedtoconfineuntrustedapplicationsorusers;butaspresentlyconstructed,thesecontainersdonotprovideadequatesecurityguarantees.
BystrengtheningthesecontainersusingSELinuxorSmackpolicy,amuchmoresecurecontainercanbeimplementedinLinux.
ThisarticleshowsyouhowtocreateamoresecureLinux-Security-Modules-protectedcontainer.
BoththeSELinuxandSmackpolicyareconsideredworksinprogress,tobeimproveduponwithhelpfromtheirrespectivecommunities.
Acommonresponsewhensomeonefirsthearsaboutcontainersis"HowdoIcreateasecurecontainer"ThisarticleanswersthatquestionbyshowingyouhowtouseLinuxSecurityModules(LSM)toimprovethesecurityofcontainers.
Inparticular,itshowsyouhowtospecifyasecuritygoalandmeetitwithboththeSmackandSELinuxsecuritymodules.
ForbackgroundreadingonLinuxContainers,see"LXC:Linuxcontainertools"(developerWorks,February2009).
LinuxcontainersarereallyaconceptualartificebuiltatopseveralLinuxtechnologies:Resourcenamespacesallowthemanipulationoflookupsofprocesses,files,SYSVIPCresources,networkinterfaces,andmore,allinsideofcontainers.
Controlgroupsallowresourcelimitstobeplacedoncontainers.
Capabilityboundingsetslimittheprivilegeavailabletocontainers.
Thesetechnologiesmustbecoordinatedinordertoprovidetheillusionofcontainers.
Twoprojectsalreadyprovidethisfunctionality:LibvirtisalargeprojectthatcancreatevirtualmachinesusingtheXenhypervisor,qemuemulator,andkvm,andalsousinglightweightcontainers.
Liblxcisasmallersetoflibrariesanduserspacecommandswritteninparttohelpkerneldevelopersquicklyandeasilytestthecontainersfunctionality.
developerWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage2of12Because"LXC:Linuxcontainertools"waswrittenusingliblxcasitsfoundation,Iwillcontinuewithliblxchere;however,anythingwedoherecanjustaseasilybedoneusinglibvirt'scontainersupport.
Majorplayer1:LSMBeforewestart,ifyouknowlittleabouttheLSM,hereisaquickreview.
AccordingtotheWikipediaentry:LinuxSecurityModules(LSM)isaframeworkthatallowstheLinuxkerneltosupportavarietyofcomputersecuritymodelswhileavoidingfavoritismtowardanysinglesecurityimplementation.
TheframeworkislicensedunderthetermsoftheGNUGeneralPublicLicenseandisstandardpartoftheLinuxkernelsinceLinux2.
6.
.
.
.
LSMwasdesignedtoprovidethespecificneedsofeverythingneededtosuccessfullyimplementamandatoryaccesscontrolmodule,whileimposingthefewestpossiblechangestotheLinuxkernel.
LSMavoidstheapproachofsystemcallinterpositionasusedinSystracebecauseitdoesnotscaletomultiprocessorkernelsandissubjecttoTOCTTOU(race)attacks.
Instead,LSMinserts"hooks"(upcallstothemodule)ateverypointinthekernelwhereauser-levelsystemcallisabouttoresultinaccesstoanimportantinternalkernelobjectsuchasinodesandtaskcontrolblocks.
.
.
.
Theprojectisnarrowlyscopedtosolvetheproblemofaccesscontroltoavoidimposingalargeandcomplexchangepatchonthemainstreamkernel.
Itisnotintendedasageneral"hook"or"upcall"mechanism,nordoesitsupportvirtualization.
.
.
.
LSM'saccesscontrolgoalisverycloselyrelatedtotheproblemofsystemauditing,butissubtlydifferent.
Auditingrequiresthateveryattemptataccessberecorded.
LSMcannotdeliverthat,becauseitwouldrequireagreatmanymorehooks,soastodetectcaseswherethekernel"shortcircuits"failingsystemcallsandreturnsanerrorcodebeforegettingnearsignificantobjects.
Systemsecurityconsistsoftwosomewhatcontradictorygoals.
Thefirstistoachievecompleteandfine-grainedaccesscontrol.
Ateverypointthatinformationcanbeleakedorcorrupted,youmustbeabletoexertcontrol.
Controlsthataretoocoarseisthesameasbeinguncontrolled.
Forinstance,if(attheextreme)allfilesmustbeclassifiedasonetypeandanyonefilemustbeworld-readable,thenallfilesmustbeworld-readable.
Ontheotherhand,configurationmustalsobesimple,otherwiseadministratorswilloftendefaulttogivingtoomuchaccess(andIcan'temphasizethisenough--thisisthesameasbeinguncontrolled).
Forinstance,ifmakingaprogramworkrequiresthousandsofaccessrules,thenchancesareanadminwillgivetheprogramtoomanyaccessrightsratherthantestingwhethereachaccessrulewasreallyneeded.
ThetwoprimarysecuritymodulesinLinuxeachtakeadifferentviewonhowtohandlethisbalance.
SELinuxbeginsbycontrollingeverythingwhileusinganimpressivepolicylanguagetosimplifypolicymanagement.
Smackisprimarilyconcernedwithprovidingasimpleaccesscontrol.
ibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage3of12Majorplayer2:SELinuxSELinuxisbyfarthemostwell-knownMACsystemforLinux(mandatoryaccesscontrol).
Whileitcertainlystillhasitsdetractors,thefactthatthepopularFedoradistributionhasbeendeployedwithSELinuxenforcingforyearsisatremendoustestamenttoitssuccess.
SELinuxisconfiguredusingamodularpolicylanguagewhichallowsaninstalledpolicytobeeasilyupdatedbyusers.
Thelanguagealsoprovidesinterfaces,allowingmorehigh-levelstatementstobeusedtorepresentacollectionoflow-level"allow"statements.
Inthisarticle,wewillbeusinganewinterfacetodefinecontainers.
Whiletheinterfaceitselfwillbequitelargeduetothemanyaccessrightsyoumustgivethecontainer,usingtheinterfacetocreateanewcontainerwillbeverysimple.
Hopefullytheinterfacecanbecomeapartofthecoredistributedpolicy.
Majorplayer3:SmackSmackistheSimplifiedMandatoryAccessControlKernel.
Itbeginsbylabelingallprocesses,files,andnetworktrafficwithsimpletextlabels.
Newlycreatedfilesarecreatedwiththelabelofthecreatingprocess.
Afewdefaulttypesalwaysexistwithclearlydefinedaccessrules.
Aprocesscanalwaysreadandwriteobjectsofthesamelabel.
PrivilegetobypasstheSmackaccessrulesarecontrolledusingPOSIXcapabilities,soataskcarryingCAP_MAC_OVERRIDEcanoverridetherules;ataskcarryingCAP_MAC_ADMINcanchangetherulesandlabels.
"POSIXfilecapabilities:Parcelingthepowerofroot"(Relatedtopics)demonstratestheseprivileges.
OursecuritygoalInsteadofsimplyblindlyapplyingpolicyandhopingtoendupwithsomethinguseful,let'sbeginbydefiningaclearsecuritygoal.
ThesimplicityofSmackactuallylimitsthegoalswecanachieve,butwe'llpursuethefollowinggoal:1.
CreatecontainerswithsegregatedfilesystemsprovidingWebandsshservices.
2.
Containerswillbeprotectedfromeachother.
Acontainerdesignatedvs1cannotreadfilesownedbyanothercontainervs2orkillitstasks.
3.
Thehostcanprotectitskeyfilesfromcontainers.
4.
TheoutsideworldcanreachtheWebserversandsshserversonthecontainers.
ThegeneralsetupInthisarticlewe'lldotwoexperiments--firstwe'llsetupcontainersprotectedbySELinux,thencontainersprotectedbySmack.
Theexperimentswillsharemuchofthepreliminarysetup.
Youcanusearealmachinetodotheseexperiments,butyoumayfinditeasierormorecomfortingtouseavirtualmachine.
Touseqemuorkvm,youcancreateaharddiskusingqemu-imgcreatevm.
img10G.
BootthevirtualmachinefromCDROMusingacommandlikekvm-hdavm.
img-cdromcdrom.
iso-bootd-m512M.
AgoodchoiceforaCDROMimageistogotofedoraproject.
org/get-fedoraanddownloadaninstallationDVDforFedora10fori386.
SubstitutethefilenameyoudownloadfordeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage4of12cdrom.
isointhepreviouscommand.
Youcanmostlyusetheinstallationdefaults,butmakesuretounselectofficeandproductivityandselectsoftwaredevelopment.
You'llalsowanttoinstallthebridge-utils,debootstrap,andncurses-develrpms,probablyusingtheyumpackagemanager.
Nowyouneedtocompileacustomkernel.
Downloadthekernel-sourcesrpm,patchitwithenable-netns.
patch(seetheDownloadsection)toprovidenetworknamespaces(whichwillbeupstreamasof2.
6.
29butnotinFedora10),changetheconfiguration,thencompletethecompilationandinstallation,byfollowingthefollowinginstructionsasroot:yumdownloader--sourcekernelrpm-ikernel*cdrpmbuildrpmbuild-bcSPECS/kernel-*cdBUILD/kernel-2.
6.
27/linux-2.
6*patch-p1Networkingoptionsmenus).
FortheSmackexperiment,alsogointotheSecurityoptionsmenu,deselectSELinux,andselectthenextoption,Smack.
Youmayalsoneedtoswitchthedefaultbootentryin/boot/grub/grub.
confbackto0insteadof1.
Nowwewanttotryoutliblxc.
"LXC:Linuxcontainertools"describesthebasicusageofliblxcindetail,sowe'llglossoverithere.
Simplyusethecontainer_setup.
shscript(seetheDownloadsection)tosetupthebridgeonwhichcontainernetworkdeviceswilltalk.
Itwillalsoclearyourfirewall,whichbydefaultisn'tsetuptohandlethebridge,aswellassetuptheSmackpolicy(whichwe'llcreatelaterinthefile/etc/smackaccesses)ifyouaredoingtheSmackexperiment.
You'llneedtoruncontainer_setup.
shaftereachrebootorifyouknowhow,makeitrunatbootautomatically.
Nowyourmachineisready!
Let'stryoutliblxc.
Youcandownloadthelatestsourceusingcvsfromlxc.
sf.
netandcompileitusingthefollowing:cvs-d:pserver:anonymous@lxc.
cvs.
sourceforge.
net:/cvsroot/lxclogincvs-z3-d:pserver:anonymous@lxc.
cvs.
sourceforge.
net:/cvsroot/lxcco-Plxccdlxc.
/bootstrap&&.
/configure&&make&&makeinstallNowifyoulookattheREADME,you'llseetherearequiteafewoptionsforgettingstarted.
Containerscanbeextremelylightweightbecausetheycansharemanyresourceswithyoursystem--includingthefilesystem.
Butourgoalistoprovidesomesimpleisolationsowewillusethescriptlxc-debiantocreateafulldebianchrootimageforeachcontainer.
Beginbycreatingacontainernamedvsplain:ibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage5of12mkdir/vsplaincd/vsplainlxc-debiancreatecontainername:vsplainhostname:vsplainIP10.
0.
2.
20gateway:10.
0.
2.
2Theconfigurationforthiscontainerisstoredunderthedirectory/usr/local/var/lxc/vsplain.
Ifyoulookatthefilecalledcgroup,you'llseesomelinesbeginningwithdevices.
.
Thesearedirectivestothedeviceswhitelistcgroupwhichwillmediatedevicecreation,read,andwritebythecontainer.
Startthiscontainerusingthecommandlxc-start-nvsplain.
You'llbepresentedwithaloginprompt.
Logintothecontainerusingusernamerootwithnopassword.
Finally,whenyourcontainerisupandrunning,youwillwanttoapt-getinstallopenssh-serverapt-getinstallapacheNowyoucansshfromthekvmhosttothecontainerandlookatitsWebpageusing10.
0.
2.
20forvsplain'sipaddressand10.
0.
2.
15forthehost's.
Youcanshutthecontainerdownatanytimefromarootterminalonthekvmhostusingthecommandlxc-stop-nvsplain.
Atthispoint,youmaywanttosaveyourselfsometimebycloningtwonewvirtualmachinesfromthistemplate.
Shutdownyourvmanddo:cpvm.
imgselinux.
imgcpvm.
imgsmack.
imgSELinux-protectedcontainersTheSELinuxpolicyforcontainerswe'llusewillconsistofapolicymodule;themodulehasbeenpostedtorefpolicy--SELinuxReferencePolicydevelopmentmaillist.
Downloadthepolicyintoadirectory/root/vs,intofilescalledvs.
if,vs.
fc,andvs.
terespectively.
Compileandinstallthenewmoduleasfollows:cp-r/usr/share/selinux/devel/usr/share/selinux/vscp/root/vs.
/usr/share/selinux/vs/cd/usr/share/selinux/vsmake&&semodule-ivs.
ppThencreatecontainers/vs1and/vs2usinglxc-debianandrelabeltheirfilesystemsusingdeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage6of12mkdir/vs1;cd/vs1lxc-debiancreatecontainername:vs1hostname:vs1address:10.
0.
2.
21gateway:10.
0.
2.
2arch:2(i386)mkdir/vs2;cd/vs2lxc-debiancreatecontainername:vs2hostname:vs2address:10.
0.
2.
22gateway:10.
0.
2.
2arch:2(i386)fixfilesrelabel/vs1fixfilesrelabel/vs2Whenyoustartyourcontainers(forinstancebyusinglxc-start-nvs1),you'lllikelygetafewauditmessagesaboutSELinuxaccessdenials.
Don'tworry--thecontainerstartsupfinewithnetworkservicesenabledandthecontainersarenowisolated.
Ifyouhelpcontainervs1cheatusingmount--bind//vs1/rootfs.
vs1/mntbeforestartingthecontainer,you'llfindthateventhoughyouaretherootuser,ls/mnt/rootwillberefused.
Toseehowthisworks,let'slookatthevs.
ifinterfacefile.
Thisdefinesaninterfacecalledcontainerwhichtakesoneargument,thebasenameforthecontainertodefine.
Thevs.
tefilecallsthisfunctiontwicewiththecontainernamesvs1,vs2.
Intheinterface,$1isexpandedtotheargument,so$1_tbecomesvs1_twhenwecallcontainer(vs1).
(Fromhereonlet'sassumewearedefiningvs1).
Themostimportantlinesarethoseinvolvingvs1_exec_t.
Thecontainerrunsintypevs1_t.
Itentersthistypewhenunconfined_texecutesthecontainer's/sbin/initwhichisoftypevs1_exec_t.
Mostoftherestofthepolicymerelyistheretograntthecontainersufficientprivilegetoaccessbitsofthesystem:networkports,devices,consoles,etc.
Theinterfaceisaslongasitisduetothefine-grainednatureoftheexistingSELinuxreferencepolicy.
Aswe'reabouttosee,theSmack-protectedcontainerwillhaveamuchsimplerpolicy;inreturn,itwillpromisemuchlessflexibleprotectionfrommisbehavingsystemservices.
Thereisonemorethingyouneedtodo.
Youmayhavenotedthatwhilethecontainerisnotabletooverwriteits$1_exec_t,thatis/sbin/init.
Butwhatitcandoissomethinglikemv/sbin/sbin.
bakmkdir/sbintouch/sbin/initTheresulting/sbin/initwillbeoftypevs1_file_t.
WhydoyouthinkthecontaineradminwouldwanttodothisBecauseitwouldlaunchthecontainer,includingthesshdaemon,intheunconfined_tdomain,givinghimaprivilegedshellandallowinghimtoescapetheSELinuxconstraintsweweretryingtoenforce.
Topreventthis,youactuallywanttostartthecontainerthroughacustomscriptandrelabelsbin/inittovs1_exec_tbeforestartingthecontainer.
Infact,youcancopyapristinecopyofinitbackintoibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage7of12thecontainerandrelabelthatifthecontaineradministratordidn'tmind.
Butwe'lljustrelabeltheexistinginit:cat>>/vs1/vs1.
sh>/vs1/vs1.
sh/proc/self/attr/currentlxc-start-nvs1/bin/dropmacadmin/sbin/initEOFchmodu+x/vs1/vs1.
shOnemorethingwillletvs1writetothetmpfsfilesystemitisgoingtomount:sed-i's/defaults/defaults,smackfsroot=vs1,smackfsdef=vs1/'\/vs1/rootfs.
vs1/etc/fstabThiswillcausethetmpfsfilesystemmountedat/dev/shmtocarrythevs1labelsothatvs1canwritetoit.
Otherwise,vs1initscriptswon'tbeabletocreatethe/dev/shm/networkdirectoryituseswhilesettingupthenetwork.
Similarly,ifyouwanttousearam-based/tmp,you'llwantthosesameoptions.
Nowagainlet'shelpvs1cheat.
Createvs2thesamewayyoucreatedvs1,substitutingvs2forvs1ateachstep.
Thenbind-mounttherootfilesystemundervs1's/mnt:mount--bind/vs1/vs1mount--make-runbindable/vs1mount--rbind//vs1/rootfs.
vs1/mntibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage9of12Startthecontainerusingvs1.
sh.
NotethatyoucanstillseetheWebpageonvs1andvs2fromthekvmhost.
Notealsothatvs1cannotaccessvs2overthenetwork.
Italsocan'tlookthroughvs2'sfiles:vs1:~#ls/mnt/(directorylisting)vs1:~#ls/mnt/vs2/rootfs.
vs2ls:/mnt/vs2/rootfs.
vs2:Permissiondeniedvs1:~#mkdir/cgroupvs1:~#mount-tcgroupcgroup/cgroupvs1:~#ls/cgroupls:/mnt/vs3:Permissiondeniedvs1:~#mknod/dev/sda1b81mknod:`/dev/sda1':Operationnotpermittedvs1:~#mount/mnt/dev/sda1/tmpmount:permissiondeniedItcanlookthroughthehostfilesystem.
Anythingwewanttoprotectagainst,wecanlabelwiththehostlabel.
That'swhatwedidwiththecgroupfilesystemwhichiswhyls/cgroupfailed.
Finally,thedeviceswhitelistcgroupispreventingusfromcreatingadiskdevice,aswellasmountingitifitexists(asitdoesthrough/mnt).
Ofcourse,thewaywe'vesetthisup,thecontaineradmincanremove/mnt/dev/sda1,aswellmessupthehostinanynumberofways,sootherthanasdemonstrationthisbindmountisobviouslynotdesirable!
NotethatwhileontheSELinuxsystem,thedefault(andeasy)routewastoallowthecontainerstotalktoeachotheroverthenetwork,theinverseistrueinSmack.
Allowingcontainerstotalktoeachotheriscurrentlyveryhardtodo.
AnabilitytosetlabelsonIPaddressesiscomingsoonthoughandshouldallowustosetuppolicytoallowcontainerstocommunicate.
RelatedtohowwesetupSmacknetworking,wehaveanotherproblem.
Thecommandkill-9-1killseverytaskonthesystem.
Whendonebyataskinacontainer,thisshouldonlykilltasksinthesamecontainer.
Thatbehaviorisnowfixedintheupstreamkernel,butnotintheFedora10kernelweareusing.
Soeverytaskwillbesenta-9signal.
IntheSELinux-protectedcontainers,SELinuxstopsthesignalsfrompassingthecontainerboundary,sokill-9-1isactuallysafe.
ButinSmacktasksbydefaultarelabeled_justasthenetworkis,sosinceweallowedthecontainertowrite_toallowwritingtothenetwork,andsincekillingataskisconsideredawriteaccessbySmack,youarealsoallowingthecontaineradmintokillanytasksonthewholesystem.
Anothershortcoming(whichisalsopresentintheSELinuxcontainers)hastodowithUnix98pseudo-terminals.
Opentwographicalterminals.
Inthefirst,startupvs1andlookunder/dev/pts.
Youwillseeatleasttwoentries,0and1,onebelongingtoeachterminal.
Fromthevs1containeryouareabletowriteintotheentrycorrespondingtotheotherterminal.
WiththeFedorakerneltherearetwosolutions.
Youcanusethedevicewhitelistcgrouptodenythecontainertheabilitytoopenthedevices.
However,thiswillhavetobedonebyhandeachtimethedeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage10of12containerisstartedinordertograntitaccesstoitsterminal;oryoucanachievethesameeffectbyapplyingSELinuxandSmacklabels.
Thenewer2.
6.
29kernelsupportsdevptsnamespaces.
Acontainerwillremount/dev/pts,afterwhichitwillbeunabletoaccessthedevptsentriesbelongingtothehostorothercontainers.
ConclusionThisarticleshowcasedthebasictoolsforcreatingLSM-protectedcontainers,butmuchworkremainstobedone:ForSmack,youmustchoosefilestolabelashost.
ForSELinux,youshouldfine-tuneandthenpushacontainerinterfaceintotheupstreamreferencepolicy.
Whilesuchworkisongoing,anduntilmoreexperienceisgainedwithLSM-protectedcontainers,youshouldnotputallyourtrustinthesemechanismstoprotectagainstanuntrustedrootuser.
Althoughtherearenoestablishedbestpracticesforcreatingcontainersyet(thatIknowof),thereareafewideasworthstartingwith.
First,rememberyouareconsolidatingtwosomewhatcontradictorygoals:Youwanttominimizeduplicationamongcontainers(andthehost)whileneedingtoensureisolation.
Onewaytoachievethesegoalscouldbetocreateasinglefullminimalrootfsinwhichnocontainerrunsandlabelingitatypewhichallcontainerscanread.
Thenuseacustomversionofthelxc-sshdscripttocreateeachactualcontainerbasedontheprototype,creatingread-onlymountsformostofthecontainer'sfilesystemwhileprovidingaprivatewritableplaceforthecontainertostorefiles,saylike/scratch.
Sinceeachcontainerhasaprivatemountsnamespace,itcanbind-mountanyfilesordirectorieswhichitneedstobeprivateand/orwriteablefromitsprivateshareddirectory.
Forinstance,ifitwantsaprivate/lib,itcanmount--bind/scratch/rootfs/lib/lib.
Likewise,theadmincanensurethateverycontainerdoesmount--bind/scratch/shadow/etc/shadowatstartup.
OneclearlimitationoftheapproachIdemonstratedherewithbothSELinuxandSmackisthatthecontaineradministratorcannotexploitLSMtocontrolinformationflowwithinhisowncontainer.
Rather,forsimplicity,alltasksinthecontaineraretreatedthesamebyMACpolicy.
Inanotherarticle,IhopetoexplorehowtoallowcontaineradministratorstospecifytheirownLSMpolicieswithoutallowingthemtoescapetheirowncontraints.
ThismaterialisbaseduponworksupportedbytheDefenseAdvancedResearchProjectsAgencyunderitsAgreementNo.
HR0011-07-9-0002.
AcknowledgmentsCaseySchaufler,theauthorofSmack,helpedingettingtheSmack-protectedcontainerofftheground,andDanWalshwaskindenoughtoprovidefeedbackontheSELinuxpolicy.
ibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage11of12DownloadableresourcesDescriptionNameSizeCodeforthisarticlecode.
zip3KBdeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage12of12Relatedtopics"LXC:Linuxcontainertools"(developerWorks,February2009)isastep-by-stepguidetocreatingLinuxcontainers.
Therefpolicy--SELinuxReferencePolicydevelopmentmaillistiswhereyou'llfindthepolicymoduleweusedinthisarticle.
"SELinuxfromscratch"(developerWorks,May2006)isadetailedintroductiontoSELinux.
PlanetSELinuxisanaggregationofblogpostsfrommembersoftheSELinuxdevelopmentcommunity.
"Smackforsimplifiedaccesscontrol"(LWN.
net,August2007)isanearlywriteupontheSmacksubmission.
LinuxResourceContainersprojectonSourceForge.
netisarepositoryofcodeforapplicationcontainerimplementationintheLinuxkernel,astagingareaforcodethatmaybesenttothelinux-kernelmailinglist.
OthercontainertechnologiesincludeSolarisZones(Solaris)BSDjails(FreeBSD)Linux-Vserver(Linux)OpenVZ(Linux)InthedeveloperWorksLinuxzone,findmoreresourcesforLinuxdevelopers(includingdeveloperswhoarenewtoLinux),andscanourmostpopulararticlesandtutorials.
SeeallLinuxtipsandLinuxtutorialsondeveloperWorks.
SELinuxcontainerspolicyCopyrightIBMCorporation2009(www.
ibm.
com/legal/copytrade.
shtml)Trademarks(www.
ibm.
com/developerworks/ibm/trademarks/)
HallynFebruary03,2009Lightweightcontainers,otherwiseknownasVirtualPrivateServers(VPS)orJails,areoftenthoughtofasasecuritytoolsdesignedtoconfineuntrustedapplicationsorusers;butaspresentlyconstructed,thesecontainersdonotprovideadequatesecurityguarantees.
BystrengtheningthesecontainersusingSELinuxorSmackpolicy,amuchmoresecurecontainercanbeimplementedinLinux.
ThisarticleshowsyouhowtocreateamoresecureLinux-Security-Modules-protectedcontainer.
BoththeSELinuxandSmackpolicyareconsideredworksinprogress,tobeimproveduponwithhelpfromtheirrespectivecommunities.
Acommonresponsewhensomeonefirsthearsaboutcontainersis"HowdoIcreateasecurecontainer"ThisarticleanswersthatquestionbyshowingyouhowtouseLinuxSecurityModules(LSM)toimprovethesecurityofcontainers.
Inparticular,itshowsyouhowtospecifyasecuritygoalandmeetitwithboththeSmackandSELinuxsecuritymodules.
ForbackgroundreadingonLinuxContainers,see"LXC:Linuxcontainertools"(developerWorks,February2009).
LinuxcontainersarereallyaconceptualartificebuiltatopseveralLinuxtechnologies:Resourcenamespacesallowthemanipulationoflookupsofprocesses,files,SYSVIPCresources,networkinterfaces,andmore,allinsideofcontainers.
Controlgroupsallowresourcelimitstobeplacedoncontainers.
Capabilityboundingsetslimittheprivilegeavailabletocontainers.
Thesetechnologiesmustbecoordinatedinordertoprovidetheillusionofcontainers.
Twoprojectsalreadyprovidethisfunctionality:LibvirtisalargeprojectthatcancreatevirtualmachinesusingtheXenhypervisor,qemuemulator,andkvm,andalsousinglightweightcontainers.
Liblxcisasmallersetoflibrariesanduserspacecommandswritteninparttohelpkerneldevelopersquicklyandeasilytestthecontainersfunctionality.
developerWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage2of12Because"LXC:Linuxcontainertools"waswrittenusingliblxcasitsfoundation,Iwillcontinuewithliblxchere;however,anythingwedoherecanjustaseasilybedoneusinglibvirt'scontainersupport.
Majorplayer1:LSMBeforewestart,ifyouknowlittleabouttheLSM,hereisaquickreview.
AccordingtotheWikipediaentry:LinuxSecurityModules(LSM)isaframeworkthatallowstheLinuxkerneltosupportavarietyofcomputersecuritymodelswhileavoidingfavoritismtowardanysinglesecurityimplementation.
TheframeworkislicensedunderthetermsoftheGNUGeneralPublicLicenseandisstandardpartoftheLinuxkernelsinceLinux2.
6.
.
.
.
LSMwasdesignedtoprovidethespecificneedsofeverythingneededtosuccessfullyimplementamandatoryaccesscontrolmodule,whileimposingthefewestpossiblechangestotheLinuxkernel.
LSMavoidstheapproachofsystemcallinterpositionasusedinSystracebecauseitdoesnotscaletomultiprocessorkernelsandissubjecttoTOCTTOU(race)attacks.
Instead,LSMinserts"hooks"(upcallstothemodule)ateverypointinthekernelwhereauser-levelsystemcallisabouttoresultinaccesstoanimportantinternalkernelobjectsuchasinodesandtaskcontrolblocks.
.
.
.
Theprojectisnarrowlyscopedtosolvetheproblemofaccesscontroltoavoidimposingalargeandcomplexchangepatchonthemainstreamkernel.
Itisnotintendedasageneral"hook"or"upcall"mechanism,nordoesitsupportvirtualization.
.
.
.
LSM'saccesscontrolgoalisverycloselyrelatedtotheproblemofsystemauditing,butissubtlydifferent.
Auditingrequiresthateveryattemptataccessberecorded.
LSMcannotdeliverthat,becauseitwouldrequireagreatmanymorehooks,soastodetectcaseswherethekernel"shortcircuits"failingsystemcallsandreturnsanerrorcodebeforegettingnearsignificantobjects.
Systemsecurityconsistsoftwosomewhatcontradictorygoals.
Thefirstistoachievecompleteandfine-grainedaccesscontrol.
Ateverypointthatinformationcanbeleakedorcorrupted,youmustbeabletoexertcontrol.
Controlsthataretoocoarseisthesameasbeinguncontrolled.
Forinstance,if(attheextreme)allfilesmustbeclassifiedasonetypeandanyonefilemustbeworld-readable,thenallfilesmustbeworld-readable.
Ontheotherhand,configurationmustalsobesimple,otherwiseadministratorswilloftendefaulttogivingtoomuchaccess(andIcan'temphasizethisenough--thisisthesameasbeinguncontrolled).
Forinstance,ifmakingaprogramworkrequiresthousandsofaccessrules,thenchancesareanadminwillgivetheprogramtoomanyaccessrightsratherthantestingwhethereachaccessrulewasreallyneeded.
ThetwoprimarysecuritymodulesinLinuxeachtakeadifferentviewonhowtohandlethisbalance.
SELinuxbeginsbycontrollingeverythingwhileusinganimpressivepolicylanguagetosimplifypolicymanagement.
Smackisprimarilyconcernedwithprovidingasimpleaccesscontrol.
ibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage3of12Majorplayer2:SELinuxSELinuxisbyfarthemostwell-knownMACsystemforLinux(mandatoryaccesscontrol).
Whileitcertainlystillhasitsdetractors,thefactthatthepopularFedoradistributionhasbeendeployedwithSELinuxenforcingforyearsisatremendoustestamenttoitssuccess.
SELinuxisconfiguredusingamodularpolicylanguagewhichallowsaninstalledpolicytobeeasilyupdatedbyusers.
Thelanguagealsoprovidesinterfaces,allowingmorehigh-levelstatementstobeusedtorepresentacollectionoflow-level"allow"statements.
Inthisarticle,wewillbeusinganewinterfacetodefinecontainers.
Whiletheinterfaceitselfwillbequitelargeduetothemanyaccessrightsyoumustgivethecontainer,usingtheinterfacetocreateanewcontainerwillbeverysimple.
Hopefullytheinterfacecanbecomeapartofthecoredistributedpolicy.
Majorplayer3:SmackSmackistheSimplifiedMandatoryAccessControlKernel.
Itbeginsbylabelingallprocesses,files,andnetworktrafficwithsimpletextlabels.
Newlycreatedfilesarecreatedwiththelabelofthecreatingprocess.
Afewdefaulttypesalwaysexistwithclearlydefinedaccessrules.
Aprocesscanalwaysreadandwriteobjectsofthesamelabel.
PrivilegetobypasstheSmackaccessrulesarecontrolledusingPOSIXcapabilities,soataskcarryingCAP_MAC_OVERRIDEcanoverridetherules;ataskcarryingCAP_MAC_ADMINcanchangetherulesandlabels.
"POSIXfilecapabilities:Parcelingthepowerofroot"(Relatedtopics)demonstratestheseprivileges.
OursecuritygoalInsteadofsimplyblindlyapplyingpolicyandhopingtoendupwithsomethinguseful,let'sbeginbydefiningaclearsecuritygoal.
ThesimplicityofSmackactuallylimitsthegoalswecanachieve,butwe'llpursuethefollowinggoal:1.
CreatecontainerswithsegregatedfilesystemsprovidingWebandsshservices.
2.
Containerswillbeprotectedfromeachother.
Acontainerdesignatedvs1cannotreadfilesownedbyanothercontainervs2orkillitstasks.
3.
Thehostcanprotectitskeyfilesfromcontainers.
4.
TheoutsideworldcanreachtheWebserversandsshserversonthecontainers.
ThegeneralsetupInthisarticlewe'lldotwoexperiments--firstwe'llsetupcontainersprotectedbySELinux,thencontainersprotectedbySmack.
Theexperimentswillsharemuchofthepreliminarysetup.
Youcanusearealmachinetodotheseexperiments,butyoumayfinditeasierormorecomfortingtouseavirtualmachine.
Touseqemuorkvm,youcancreateaharddiskusingqemu-imgcreatevm.
img10G.
BootthevirtualmachinefromCDROMusingacommandlikekvm-hdavm.
img-cdromcdrom.
iso-bootd-m512M.
AgoodchoiceforaCDROMimageistogotofedoraproject.
org/get-fedoraanddownloadaninstallationDVDforFedora10fori386.
SubstitutethefilenameyoudownloadfordeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage4of12cdrom.
isointhepreviouscommand.
Youcanmostlyusetheinstallationdefaults,butmakesuretounselectofficeandproductivityandselectsoftwaredevelopment.
You'llalsowanttoinstallthebridge-utils,debootstrap,andncurses-develrpms,probablyusingtheyumpackagemanager.
Nowyouneedtocompileacustomkernel.
Downloadthekernel-sourcesrpm,patchitwithenable-netns.
patch(seetheDownloadsection)toprovidenetworknamespaces(whichwillbeupstreamasof2.
6.
29butnotinFedora10),changetheconfiguration,thencompletethecompilationandinstallation,byfollowingthefollowinginstructionsasroot:yumdownloader--sourcekernelrpm-ikernel*cdrpmbuildrpmbuild-bcSPECS/kernel-*cdBUILD/kernel-2.
6.
27/linux-2.
6*patch-p1Networkingoptionsmenus).
FortheSmackexperiment,alsogointotheSecurityoptionsmenu,deselectSELinux,andselectthenextoption,Smack.
Youmayalsoneedtoswitchthedefaultbootentryin/boot/grub/grub.
confbackto0insteadof1.
Nowwewanttotryoutliblxc.
"LXC:Linuxcontainertools"describesthebasicusageofliblxcindetail,sowe'llglossoverithere.
Simplyusethecontainer_setup.
shscript(seetheDownloadsection)tosetupthebridgeonwhichcontainernetworkdeviceswilltalk.
Itwillalsoclearyourfirewall,whichbydefaultisn'tsetuptohandlethebridge,aswellassetuptheSmackpolicy(whichwe'llcreatelaterinthefile/etc/smackaccesses)ifyouaredoingtheSmackexperiment.
You'llneedtoruncontainer_setup.
shaftereachrebootorifyouknowhow,makeitrunatbootautomatically.
Nowyourmachineisready!
Let'stryoutliblxc.
Youcandownloadthelatestsourceusingcvsfromlxc.
sf.
netandcompileitusingthefollowing:cvs-d:pserver:anonymous@lxc.
cvs.
sourceforge.
net:/cvsroot/lxclogincvs-z3-d:pserver:anonymous@lxc.
cvs.
sourceforge.
net:/cvsroot/lxcco-Plxccdlxc.
/bootstrap&&.
/configure&&make&&makeinstallNowifyoulookattheREADME,you'llseetherearequiteafewoptionsforgettingstarted.
Containerscanbeextremelylightweightbecausetheycansharemanyresourceswithyoursystem--includingthefilesystem.
Butourgoalistoprovidesomesimpleisolationsowewillusethescriptlxc-debiantocreateafulldebianchrootimageforeachcontainer.
Beginbycreatingacontainernamedvsplain:ibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage5of12mkdir/vsplaincd/vsplainlxc-debiancreatecontainername:vsplainhostname:vsplainIP10.
0.
2.
20gateway:10.
0.
2.
2Theconfigurationforthiscontainerisstoredunderthedirectory/usr/local/var/lxc/vsplain.
Ifyoulookatthefilecalledcgroup,you'llseesomelinesbeginningwithdevices.
.
Thesearedirectivestothedeviceswhitelistcgroupwhichwillmediatedevicecreation,read,andwritebythecontainer.
Startthiscontainerusingthecommandlxc-start-nvsplain.
You'llbepresentedwithaloginprompt.
Logintothecontainerusingusernamerootwithnopassword.
Finally,whenyourcontainerisupandrunning,youwillwanttoapt-getinstallopenssh-serverapt-getinstallapacheNowyoucansshfromthekvmhosttothecontainerandlookatitsWebpageusing10.
0.
2.
20forvsplain'sipaddressand10.
0.
2.
15forthehost's.
Youcanshutthecontainerdownatanytimefromarootterminalonthekvmhostusingthecommandlxc-stop-nvsplain.
Atthispoint,youmaywanttosaveyourselfsometimebycloningtwonewvirtualmachinesfromthistemplate.
Shutdownyourvmanddo:cpvm.
imgselinux.
imgcpvm.
imgsmack.
imgSELinux-protectedcontainersTheSELinuxpolicyforcontainerswe'llusewillconsistofapolicymodule;themodulehasbeenpostedtorefpolicy--SELinuxReferencePolicydevelopmentmaillist.
Downloadthepolicyintoadirectory/root/vs,intofilescalledvs.
if,vs.
fc,andvs.
terespectively.
Compileandinstallthenewmoduleasfollows:cp-r/usr/share/selinux/devel/usr/share/selinux/vscp/root/vs.
/usr/share/selinux/vs/cd/usr/share/selinux/vsmake&&semodule-ivs.
ppThencreatecontainers/vs1and/vs2usinglxc-debianandrelabeltheirfilesystemsusingdeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage6of12mkdir/vs1;cd/vs1lxc-debiancreatecontainername:vs1hostname:vs1address:10.
0.
2.
21gateway:10.
0.
2.
2arch:2(i386)mkdir/vs2;cd/vs2lxc-debiancreatecontainername:vs2hostname:vs2address:10.
0.
2.
22gateway:10.
0.
2.
2arch:2(i386)fixfilesrelabel/vs1fixfilesrelabel/vs2Whenyoustartyourcontainers(forinstancebyusinglxc-start-nvs1),you'lllikelygetafewauditmessagesaboutSELinuxaccessdenials.
Don'tworry--thecontainerstartsupfinewithnetworkservicesenabledandthecontainersarenowisolated.
Ifyouhelpcontainervs1cheatusingmount--bind//vs1/rootfs.
vs1/mntbeforestartingthecontainer,you'llfindthateventhoughyouaretherootuser,ls/mnt/rootwillberefused.
Toseehowthisworks,let'slookatthevs.
ifinterfacefile.
Thisdefinesaninterfacecalledcontainerwhichtakesoneargument,thebasenameforthecontainertodefine.
Thevs.
tefilecallsthisfunctiontwicewiththecontainernamesvs1,vs2.
Intheinterface,$1isexpandedtotheargument,so$1_tbecomesvs1_twhenwecallcontainer(vs1).
(Fromhereonlet'sassumewearedefiningvs1).
Themostimportantlinesarethoseinvolvingvs1_exec_t.
Thecontainerrunsintypevs1_t.
Itentersthistypewhenunconfined_texecutesthecontainer's/sbin/initwhichisoftypevs1_exec_t.
Mostoftherestofthepolicymerelyistheretograntthecontainersufficientprivilegetoaccessbitsofthesystem:networkports,devices,consoles,etc.
Theinterfaceisaslongasitisduetothefine-grainednatureoftheexistingSELinuxreferencepolicy.
Aswe'reabouttosee,theSmack-protectedcontainerwillhaveamuchsimplerpolicy;inreturn,itwillpromisemuchlessflexibleprotectionfrommisbehavingsystemservices.
Thereisonemorethingyouneedtodo.
Youmayhavenotedthatwhilethecontainerisnotabletooverwriteits$1_exec_t,thatis/sbin/init.
Butwhatitcandoissomethinglikemv/sbin/sbin.
bakmkdir/sbintouch/sbin/initTheresulting/sbin/initwillbeoftypevs1_file_t.
WhydoyouthinkthecontaineradminwouldwanttodothisBecauseitwouldlaunchthecontainer,includingthesshdaemon,intheunconfined_tdomain,givinghimaprivilegedshellandallowinghimtoescapetheSELinuxconstraintsweweretryingtoenforce.
Topreventthis,youactuallywanttostartthecontainerthroughacustomscriptandrelabelsbin/inittovs1_exec_tbeforestartingthecontainer.
Infact,youcancopyapristinecopyofinitbackintoibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage7of12thecontainerandrelabelthatifthecontaineradministratordidn'tmind.
Butwe'lljustrelabeltheexistinginit:cat>>/vs1/vs1.
sh>/vs1/vs1.
sh/proc/self/attr/currentlxc-start-nvs1/bin/dropmacadmin/sbin/initEOFchmodu+x/vs1/vs1.
shOnemorethingwillletvs1writetothetmpfsfilesystemitisgoingtomount:sed-i's/defaults/defaults,smackfsroot=vs1,smackfsdef=vs1/'\/vs1/rootfs.
vs1/etc/fstabThiswillcausethetmpfsfilesystemmountedat/dev/shmtocarrythevs1labelsothatvs1canwritetoit.
Otherwise,vs1initscriptswon'tbeabletocreatethe/dev/shm/networkdirectoryituseswhilesettingupthenetwork.
Similarly,ifyouwanttousearam-based/tmp,you'llwantthosesameoptions.
Nowagainlet'shelpvs1cheat.
Createvs2thesamewayyoucreatedvs1,substitutingvs2forvs1ateachstep.
Thenbind-mounttherootfilesystemundervs1's/mnt:mount--bind/vs1/vs1mount--make-runbindable/vs1mount--rbind//vs1/rootfs.
vs1/mntibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage9of12Startthecontainerusingvs1.
sh.
NotethatyoucanstillseetheWebpageonvs1andvs2fromthekvmhost.
Notealsothatvs1cannotaccessvs2overthenetwork.
Italsocan'tlookthroughvs2'sfiles:vs1:~#ls/mnt/(directorylisting)vs1:~#ls/mnt/vs2/rootfs.
vs2ls:/mnt/vs2/rootfs.
vs2:Permissiondeniedvs1:~#mkdir/cgroupvs1:~#mount-tcgroupcgroup/cgroupvs1:~#ls/cgroupls:/mnt/vs3:Permissiondeniedvs1:~#mknod/dev/sda1b81mknod:`/dev/sda1':Operationnotpermittedvs1:~#mount/mnt/dev/sda1/tmpmount:permissiondeniedItcanlookthroughthehostfilesystem.
Anythingwewanttoprotectagainst,wecanlabelwiththehostlabel.
That'swhatwedidwiththecgroupfilesystemwhichiswhyls/cgroupfailed.
Finally,thedeviceswhitelistcgroupispreventingusfromcreatingadiskdevice,aswellasmountingitifitexists(asitdoesthrough/mnt).
Ofcourse,thewaywe'vesetthisup,thecontaineradmincanremove/mnt/dev/sda1,aswellmessupthehostinanynumberofways,sootherthanasdemonstrationthisbindmountisobviouslynotdesirable!
NotethatwhileontheSELinuxsystem,thedefault(andeasy)routewastoallowthecontainerstotalktoeachotheroverthenetwork,theinverseistrueinSmack.
Allowingcontainerstotalktoeachotheriscurrentlyveryhardtodo.
AnabilitytosetlabelsonIPaddressesiscomingsoonthoughandshouldallowustosetuppolicytoallowcontainerstocommunicate.
RelatedtohowwesetupSmacknetworking,wehaveanotherproblem.
Thecommandkill-9-1killseverytaskonthesystem.
Whendonebyataskinacontainer,thisshouldonlykilltasksinthesamecontainer.
Thatbehaviorisnowfixedintheupstreamkernel,butnotintheFedora10kernelweareusing.
Soeverytaskwillbesenta-9signal.
IntheSELinux-protectedcontainers,SELinuxstopsthesignalsfrompassingthecontainerboundary,sokill-9-1isactuallysafe.
ButinSmacktasksbydefaultarelabeled_justasthenetworkis,sosinceweallowedthecontainertowrite_toallowwritingtothenetwork,andsincekillingataskisconsideredawriteaccessbySmack,youarealsoallowingthecontaineradmintokillanytasksonthewholesystem.
Anothershortcoming(whichisalsopresentintheSELinuxcontainers)hastodowithUnix98pseudo-terminals.
Opentwographicalterminals.
Inthefirst,startupvs1andlookunder/dev/pts.
Youwillseeatleasttwoentries,0and1,onebelongingtoeachterminal.
Fromthevs1containeryouareabletowriteintotheentrycorrespondingtotheotherterminal.
WiththeFedorakerneltherearetwosolutions.
Youcanusethedevicewhitelistcgrouptodenythecontainertheabilitytoopenthedevices.
However,thiswillhavetobedonebyhandeachtimethedeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage10of12containerisstartedinordertograntitaccesstoitsterminal;oryoucanachievethesameeffectbyapplyingSELinuxandSmacklabels.
Thenewer2.
6.
29kernelsupportsdevptsnamespaces.
Acontainerwillremount/dev/pts,afterwhichitwillbeunabletoaccessthedevptsentriesbelongingtothehostorothercontainers.
ConclusionThisarticleshowcasedthebasictoolsforcreatingLSM-protectedcontainers,butmuchworkremainstobedone:ForSmack,youmustchoosefilestolabelashost.
ForSELinux,youshouldfine-tuneandthenpushacontainerinterfaceintotheupstreamreferencepolicy.
Whilesuchworkisongoing,anduntilmoreexperienceisgainedwithLSM-protectedcontainers,youshouldnotputallyourtrustinthesemechanismstoprotectagainstanuntrustedrootuser.
Althoughtherearenoestablishedbestpracticesforcreatingcontainersyet(thatIknowof),thereareafewideasworthstartingwith.
First,rememberyouareconsolidatingtwosomewhatcontradictorygoals:Youwanttominimizeduplicationamongcontainers(andthehost)whileneedingtoensureisolation.
Onewaytoachievethesegoalscouldbetocreateasinglefullminimalrootfsinwhichnocontainerrunsandlabelingitatypewhichallcontainerscanread.
Thenuseacustomversionofthelxc-sshdscripttocreateeachactualcontainerbasedontheprototype,creatingread-onlymountsformostofthecontainer'sfilesystemwhileprovidingaprivatewritableplaceforthecontainertostorefiles,saylike/scratch.
Sinceeachcontainerhasaprivatemountsnamespace,itcanbind-mountanyfilesordirectorieswhichitneedstobeprivateand/orwriteablefromitsprivateshareddirectory.
Forinstance,ifitwantsaprivate/lib,itcanmount--bind/scratch/rootfs/lib/lib.
Likewise,theadmincanensurethateverycontainerdoesmount--bind/scratch/shadow/etc/shadowatstartup.
OneclearlimitationoftheapproachIdemonstratedherewithbothSELinuxandSmackisthatthecontaineradministratorcannotexploitLSMtocontrolinformationflowwithinhisowncontainer.
Rather,forsimplicity,alltasksinthecontaineraretreatedthesamebyMACpolicy.
Inanotherarticle,IhopetoexplorehowtoallowcontaineradministratorstospecifytheirownLSMpolicieswithoutallowingthemtoescapetheirowncontraints.
ThismaterialisbaseduponworksupportedbytheDefenseAdvancedResearchProjectsAgencyunderitsAgreementNo.
HR0011-07-9-0002.
AcknowledgmentsCaseySchaufler,theauthorofSmack,helpedingettingtheSmack-protectedcontainerofftheground,andDanWalshwaskindenoughtoprovidefeedbackontheSELinuxpolicy.
ibm.
com/developerWorks/developerWorksSecureLinuxcontainerscookbookPage11of12DownloadableresourcesDescriptionNameSizeCodeforthisarticlecode.
zip3KBdeveloperWorksibm.
com/developerWorks/SecureLinuxcontainerscookbookPage12of12Relatedtopics"LXC:Linuxcontainertools"(developerWorks,February2009)isastep-by-stepguidetocreatingLinuxcontainers.
Therefpolicy--SELinuxReferencePolicydevelopmentmaillistiswhereyou'llfindthepolicymoduleweusedinthisarticle.
"SELinuxfromscratch"(developerWorks,May2006)isadetailedintroductiontoSELinux.
PlanetSELinuxisanaggregationofblogpostsfrommembersoftheSELinuxdevelopmentcommunity.
"Smackforsimplifiedaccesscontrol"(LWN.
net,August2007)isanearlywriteupontheSmacksubmission.
LinuxResourceContainersprojectonSourceForge.
netisarepositoryofcodeforapplicationcontainerimplementationintheLinuxkernel,astagingareaforcodethatmaybesenttothelinux-kernelmailinglist.
OthercontainertechnologiesincludeSolarisZones(Solaris)BSDjails(FreeBSD)Linux-Vserver(Linux)OpenVZ(Linux)InthedeveloperWorksLinuxzone,findmoreresourcesforLinuxdevelopers(includingdeveloperswhoarenewtoLinux),andscanourmostpopulararticlesandtutorials.
SeeallLinuxtipsandLinuxtutorialsondeveloperWorks.
SELinuxcontainerspolicyCopyrightIBMCorporation2009(www.
ibm.
com/legal/copytrade.
shtml)Trademarks(www.
ibm.
com/developerworks/ibm/trademarks/)
- providingpermissiondenied相关文档
- 协商permissiondenied
- 4.permissiondenied
- termpermissiondenied
- Settingpermissiondenied
- 用户permissiondenied
- 5.permissiondenied
棉花云1折起(49元), 国内BGP 美国 香港 日本
棉花云官网棉花云隶属于江西乐网科技有限公司,前身是2014年就运营的2014IDC,专注海外线路已有7年有余,是国内较早从事海外专线的互联网基础服务提供商。公司专注为用户提供低价高性能云计算产品,致力于云计算应用的易用性开发,并引导云计算在国内普及。目前公司研发以及运营云服务基础设施服务平台(IaaS),面向全球客户提供基于云计算的IT解决方案与客户服务(SaaS),拥有丰富的国内BGP、双线高防...
华为云(69元)828促销活动 2G1M云服务器
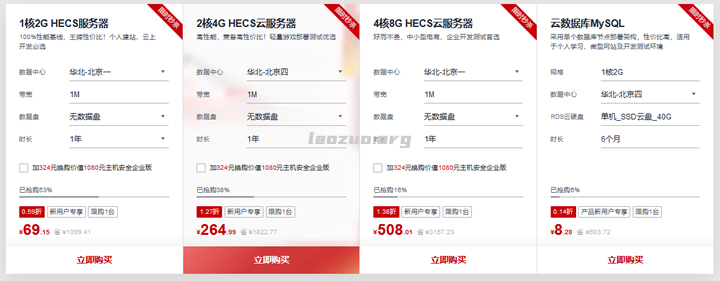
华为云818上云活动活动截止到8月31日。1、秒杀限时区优惠仅限一单!云服务器秒杀价低至0.59折,每日9点开抢秒杀抢购活动仅限早上9点开始,有限量库存的。2G1M云服务器低至首年69元。2、新用户折扣区优惠仅限一单!购云服务器享3折起加购主机安全及数据库。企业和个人的优惠力度和方案是不同的。比如还有.CN域名首年8元。华为云服务器CPU资源正常没有扣量。3、抽奖活动在8.4-8.31日期间注册并...
Hostodo商家提供两年大流量美国VPS主机 可选拉斯维加斯和迈阿密
Hostodo商家算是一个比较小众且运营比较久的服务商,而且还是率先硬盘更换成NVMe阵列的,目前有提供拉斯维加斯和迈阿密两个机房。看到商家这两年的促销套餐方案变化还是比较大的,每个月一般有这么两次的促销方案推送,可见商家也在想着提高一些客户量。毕竟即便再老的服务商,你不走出来让大家知道,迟早会落寞。目前,Hostodo有提供两款大流量的VPS主机促销,机房可选拉斯维加斯和迈阿密两个数据中心,且都...
permissiondenied为你推荐
-
存储备份存储备份软件哪个好?求推荐固态硬盘是什么固态硬盘是什么?与普通硬盘有什么区别?移动硬盘与u盘有什么区别?vc组合金钟大奖VC组合的两个人分别叫什么?硬盘工作原理硬盘是如何工作的杨紫别祝我生日快乐一个人过生日的伤感说说有什么留学生认证留学生为什么要做学历认证?www.kkk.com谁有免费的电影网站,越多越好?百度关键词分析怎样对关键词进行分析和选择777k7.com怎么在这几个网站上下载图片啊www.777mu.com www.gangguan23.com广告法新修订的《广告法》有哪些内容