简评使用http代理服务器的安全性简评(On the safety of HTTP proxy server)
使用http代理服务器的安全性简评On the safety of HTTP proxyserver
Due to various reasons, in the domestic Internet, it isunavoidable to deal with HTTP proxy server. HTTP proxy serveris divided into encrypted proxy server and general proxy server.If we run some software on your computer can access before cannot access the site, then it may be encrypted proxy; if we setthe proxy server in the browser, without running any software,so this type of proxy server is the general agent. In general,encryption agent security is better than ordinary proxy ifthere is no problem with encryption agent software. Here, thisarticle is mainly about the security of ordinary agents.Brief introduction of 1 and HTTP proxy agreement
The communication between the browser and the HTTP proxy serveris through the HTTP proxy protocol. If we do not use theencrypted proxy running on your computer, but directly in thebrowser settings on the internet proxy server address, thensend between the browser and proxy server communication to theInternet will. The common requests of proxy server are GET, POSTand CONNECT, and the following are introduced respectively:
1. 1, GE T
If we access aweb page of a HTTP protocol through a proxy server,then the browser sends the GET request to the HTTP proxy server.For example, when we access http://www.microsoft.com/ througha proxy server, the browser sends data to the HTTP proxy server:
. . . . . .
After the proxy server gets the data, the web page is returnedto the browser:
HTTP/1. 1 200 OK
. . . . . .
<html>
. . . . . .
We did not use and comparison of the proxy server, if not usinga proxy server, then we visit http://www.microsoft.com/, thebrowser will send a request to the server underwww.microsoft.com:
GET / HTTP/1. 1
. . . . . .
Server return:
HTTP/1. 1 200 OK
. . . . . .
<html>
. . . . . .
We see that after using the proxy server, the format of the GETrequest and return is almost unchanged, and there is nodifference in the security of using the proxy server.
1.2, POST
When we submit the form in the use of the HTTP protocol on thesite (such as the website user login form, fill in the user nameand password, and then log in, the form is submitted to theserver) , if the form type is POST (most of the type of form isPOST, but the search engine search form seemed to be GET type) ,then the browser will send a POST request to the proxy server.Comments such as inhttp://www.williamlong. info/archives/2209.html, the datawill be submitted to the http://www.williamlong. info/cmd.asp?Act=cmt&key=a666b083, if we use the HTTP proxy server, therequest will be sent to the proxy server:
POST http://www.williamlong. info/cmd.asp?
Act=cmt&key=a666b083 HTTP/1. 1
. . . . . .
[submission of comment data]
If the proxy server is not used, the following POST requestsare sent directly to the www.williamlong. info server:
POST /cmd.asp? Act=cmt&key=a666b083 HTTP/1. 1
. . . . . .
[submission of comment data]
The results returned using proxy server and without proxyserver are basically the same. So POST requests are basicallyno different in terms of the security of using proxy servers.
1.3, CONNECT
When we visit the HTTPS protocol web site, the browser sendsthe CONNECT request to the proxy server. For example, we visithttps://mail.google.
When com/mail/? Shva=1#inbox, the browser sends the followingrequest to the proxy server:
CONNECT mail.google.com:443 HTTP/1.0
. . . . . .
Then the server returns:
HTTP/1. 1 200 Connection established
. . . . . .
Then the browser starts sending encrypted data to the proxyserver, using the mail.google. com SSL certificate. The proxy
server to encrypt data as mail.google. com returns back to thebrowser.
If you don't use a proxy server, the browser connects directlyto the mail.google. com:443, and then starts sending andreceiving encrypted data.
We see that the use of the HTTP proxy server, HTTPS protocolcontent still end-to-end encryption, HTTPS still maintains thetransmission of any content will not be responsible for datatransmission equipment (including proxy server) to see thecharacteristics. Whether the proxy server is used does notchange the security of the HTTPS protocol.
2. Discuss in depth
Q: we see, after using the proxy server will need to access thedomain name of the website (including HTTPS) sent to the proxyserver, so that if the network being monitored, you will knowwhat sites we visit (but not HTTPS protocol to monitor thecontents of the transmission, only know that we visited thewebsite) , this is reduce security?
A: if our network is monitored, all network data packets arerecorded, so if you don't use a proxy server, the browser willfirst send a query to the corresponding domain name IP DNSrequest, IP will also be sent after the TCP connection requestto the need to visit the site, they can knowwhat sites we visitby network packet monitor.
Q: some proxy server products claim to be able to record the
contents of HTTPS transmission. How do they do that?
A: using the SSL hijacking means. These proxy server products,without exception, need to install the corresponding client,once you install these clients, you can control the clientcomputer, and then install the proxy server' s own certificate,SSL hijacking. Some products do not need to install the client,but the client browser access all the HTTPS web site, but thebrowser SSL certificate validation, the browser will give thecertificate invalid warning.
Q: if we were not able to access a website, use a proxy servercan be put on the website, this website is the HTTP protocol,so that access to this site all actions are logged in themonitored network environment?
A: yes. Because the proxy server does not change the securityof the HTTP protocol, all the contents of the plaintexttransmission can be recorded by the monitoring system. So, weuse a proxy server to submit important information (such as username and password) , you must select the HTTPS protocol, enterthe user name and password in the need to pay attention to thebrowser' s address bar is not to begin with https.
Q: after using aproxy server, theway the network packet passesis not different from that of the proxy server. What' s theimpact on the security?
A: it depends on every node in the road that was used beforeand after the proxy server was used. Even if you do not use aproxy server, the Internet still face a variety of human network
fault, using a proxy server because of the path is different,so there may still need to face these artificial networkfailures, there may be no need to face these people a networkfailure (if the proxy server itself specifically addressesthese failures) .
3, s umm ary
The above, using a remote HTTP proxy server security and do notuse a proxy server basic does not have what difference, thehuman network problems we face in using a proxy server theremay still exist, but also may reduce or even disappear.If someone offers artificial network failure to resolve theproxy server in the country, not to use or inability to useencryption software agents used, combined with the "proxyserver" and how to use AutoProxy, the agent of the era mightcome oh.
- 简评使用http代理服务器的安全性简评(On the safety of HTTP proxy server)相关文档
- 服务器配置Apache Http Server做为WebLogic集群的代理服务器
- 代理服务器在IE等浏览器中使用HTTP代理服务器
- 地址搭建http代理服务器
- 代理服务器python实现http代理服务器
- 江苏省教育网代理服务器-http代理-游戏代理服务器
- 征地http
BuyVM商家4个机房的官方测试IP地址和测速文件
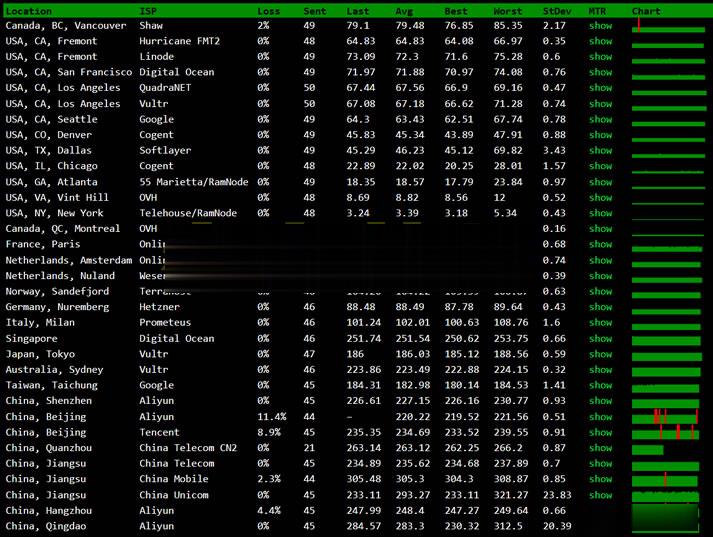
BuyVM 商家算是有一些年头,从早年提供低价便宜VPS主机深受广大网友抢购且也遭到吐槽的是因为审核账户太过于严格。毕竟我们国内的个人注册账户喜欢账户资料乱写,毕竟我们看英文信息有些还是比较难以识别的,于是就注册信息的时候随便打一些字符,这些是不能通过的。前几天,我们可以看到BUYVM商家有新增加迈阿密机房,而且商家有提供大硬盘且不限制流量的VPS主机,深受有一些网友的喜欢。目前,BUYVM商家有...
RAKsmart推出7.59美元/月,云服务器产品Cloud Server,KVM架构1核1G内存40G硬盘1M带宽基础配置
近期RAKsmart上线云服务器Cloud Server产品,KVM架构1核1G内存40G硬盘1M带宽基础配置7.59美元/月!RAKsmart云服务器Cloud Server位于美国硅谷机房,下单可选DIY各项配置,VPC网络/经典网络,大陆优化/精品网线路,1-1000Mbps带宽,支持Linux或者Windows操作系统,提供Snap和Backup。RAKsmart机房是一家成立于2012年...
Virtono:圣何塞VPS七五折月付2.2欧元起,免费双倍内存
Virtono是一家成立于2014年的国外VPS主机商,提供VPS和服务器租用等产品,商家支持PayPal、信用卡、支付宝等国内外付款方式,可选数据中心共7个:罗马尼亚2个,美国3个(圣何塞、达拉斯、迈阿密),英国和德国各1个。目前,商家针对美国圣何塞机房VPS提供75折优惠码,同时,下单后在LET回复订单号还能获得双倍内存的升级。下面以圣何塞为例,分享几款VPS主机配置信息。Cloud VPSC...
-
discuzntdiscuz !nt论坛如何上传超大附件?怎么样免费装扮qq空间要怎么免费装扮QQ空间!ghostxp3ghost xp sp3 和 windows xp3有啥区别硬盘人移动硬盘的优缺点畅想中国20年后中国会变成什么样?--畅想一下未来的中国!!畅想中国用“心系祖国情,畅想中国梦”为题目的800字作文创维云电视功能创维电视怎么用,我买了个创维云电视,现在不知道怎么用手机往电视上传照片,谁能解答以下,网络广告投放网络广告投放有哪些技巧?小米手柄手机用小米手柄能玩什么游戏三星s8什么时候上市三星s8什么时候上市 三星s8上市时间