FIGUREhkcmd.exe
hkcmd.exe 时间:2021-04-14 阅读:()
TrendMicroIncorporatedResearchPaper2013FAKEMRATMalwareDisguisedasWindowsMessengerandYahoo!
MessengerBy:NartVilleneuveJessadelaTorreContentsIntroduction.
1Distribution.
2Installation.
3Backdoor.
3NetworkTrafficEncryption.
5Infrastructure.
7Conclusion.
81|FAKEMRATIntroductionTheperpetratorsoftargetedattacksaimtomaintainpersistentpresenceinatargetnetworkinordertoextractsensitivedatawhenneeded.
Tomaintainpersistentpresence,attackersseektoblendinwithnormalnetworktrafficanduseportsthataretypicallyallowedbyfirewalls.
Asaresult,manyofthemalwareusedintargetedattacksutilizetheHTTPandHTTPSprotocolstoappearlikewebtraffic.
However,whilethesemalwaredogiveattackersfullcontroloveracompromisedsystem,theyareoftensimpleandconfiguredtocarryoutafewcommands.
AttackersoftenuseremoteaccessTrojans(RATs),whichtypicallyhavegraphicaluserinterfaces(GUIs)andremotedesktopfeaturesthatincludedirectorybrowsing,filetransfer,andtheabilitytotakescreenshotsandactivatethemicrophoneandwebcameraofacompromisedcomputer.
AttackersoftenusepubliclyavailableRATslikeGh0st,PoisonIvy,Hupigon,andDRAT,and"closed-released"RATslikeMFCHunterandPlugX.
1However,thenetworktraffictheseRATsproduceiswell-knownandeasilydetectablealthoughattackersstillsuccessfullyusethem.
2Attackersalwayslookforwaystoblendtheirmalicioustrafficwithlegitimatetraffictoavoiddetection.
WefoundafamilyofRATsthatwecall"FAKEM"thatmaketheirnetworktrafficlooklikevariousprotocols.
SomevariantsattempttodisguisenetworktraffictolooklikeWindowsMessengerandYahoo!
Messengertraffic.
AnothervarianttriestomakethecontentofitstrafficlooklikeHTML.
WhilethedisguisestheRATsusearesimpleanddistinguishablefromlegitimatetraffic,theymaybejustgoodenoughtoavoidfurtherscrutiny.
1Gh0st:http://download01.
norman.
no/documents/ThemanyfacesofGh0stRat.
pdfandhttp://www.
mcafee.
com/ca/resources/white-papers/foundstone/wp-know-your-digital-enemy.
pdf;PoisonIvy:https://media.
blackhat.
com/bh-eu-10/presentations/Dereszowski/BlackHat-EU-2010-Dereszowski-Targeted-Attacks-slides.
pdf;Hupigon:http://www.
f-secure.
com/v-descs/backdoor_w32_hupigon.
shtml;DRAT:http://blog.
trendmicro.
com/trendlabs-security-intelligence/watering-holes-and-zero-day-attacks/;MFCHunter:http://blog.
trendmicro.
com/trendlabs-security-intelligence/japan-us-defense-industries-among-targeted-entities-in-latest-attack/;andPlugX:http://about-threats.
trendmicro.
com/us/webattack/112/Pulling+the+Plug+on+PlugX2http://www.
trendmicro.
com/cloud-content/us/pdfs/security-intelligence/white-papers/wp-detecting-apt-activity-with-network-traffic-analysis.
pdf2|FAKEMRATDistributionAllthreeversionsoftheFAKEMRATthatweinvestigatedweredistributedviaspear-phishingemailsusingsocialengineeringtoluretargetsintoexecutingamaliciousattachment.
Whileweobservedtheuseofdifferentthemes,thecontentoftheemailswerealwaysinterestingtopotentialtargets.
FIGURE1:Samplespear-phishingemailswithattachmentsthatdropFAKEMRATThemaliciousattachmentsweremostoftenMicrosoftWorddocumentswithcodethatexploitsthefollowingvulnerabilities:CVE-2010-3333:RTFStackBufferOverflowVulnerabilityaddressedinMicrosoftSecurityBulletinMS10-087.
3CVE-2012-0158:MSCOMCTL.
OCXRCEVulnerabilityaddressedinMicrosoftSecurityBulletinMS12-027.
4WealsofoundaMicrosoftExcelfilethatexploitsCVE-2009-3129,theExcelFeatheaderRecordMemoryCorruptionVulnerabilityaddressedinMicrosoftSecurityBulletinMS09-067.
5Wealsosawsamplesthatweresimplyexecutable(.
EXE)files.
3http://technet.
microsoft.
com/en-us/security/bulletin/MS10-0874http://technet.
microsoft.
com/en-us/security/bulletin/ms12-0275http://technet.
microsoft.
com/en-us/security/bulletin/MS09-0673|FAKEMRATInstallationAfterexploitation,an.
EXEfilepackedwithUPXisdropped.
6Afterinitiallydroppingthemaliciousfilenamedhkcmd.
exetothe%Temp%folder,themalwaretypicallycopiesitselfusingthename,tpframe.
exe,tothe%System%folder.
Itthenaddsthefollowingregistryentrytoenableitsautomaticexecutionateverysystemstartup:HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\policies\Explorer\runtpbar="%System%\tpframe.
exe"BackdoorThenetworktrafficthemalwareproducesisdesignedtolooklikeWindowsMessengertraffic.
MalwareofthistypewerediscussedonTwitter,notedbySonicWALL,andfoundtohavebeenactiveasfarbackasSeptember2009.
7However,itremainsunclearifalltheattacksthatusedthismalwarewereconnected.
ThemalicioustrafficbeginswithheaderssimilartoactualWindowsMessengertraffic:MSG5N130MIME-Version:1.
0However,beyondthis,youwillseethatthetrafficisnotvalidWindowsMessengertrafficbutmaybesufficientlydisguisedassuchtoescapefurtherscrutiny.
6UPXisafreetoolthatcompressesexecutablefiles.
However,itiscommonlyusedtopackmalwarefiles,seehttp://upx.
sourceforge.
net/formoredetails.
7https://twitter.
com/mikko/status/232851667446538241,https://www.
mysonicwall.
com/sonicalert/searchresults.
aspxev=article&id=464,andhttps://twitter.
com/diocyde/statuses/2328730236513361924|FAKEMRATFIGURE4:MalicioustrafficdisguisedasYahoo!
MessengertrafficFIGURE3:LegitimateWindowsMessengertrafficFIGURE2:MalicioustrafficdisguisedaslegitimateWindowsMessengertrafficComparedwithactualWindowsMessengertrafficshowninFigure3,itiseasytodistinguishthemalicioustrafficshowninFigure2.
Duringourinvestigationofthefake"WindowsMessenger"RAT,wefoundanotherversionthatattemptstodisguiseitsnetworktrafficasYahoo!
Messengertraffic.
ThenetworkcommunicationthisversionusesbeginswithYMSG,theYahoo!
Messengertrafficheader.
FIGURE5:LegitimateYahoo!
MessengertrafficHowever,thenetworktrafficshowninFigure4doesnotresemblelegitimateYahoo!
Messengertrafficbeyondtheuseoftheheader,YMSG.
ComparedwiththelegitimateYahoo!
MessengertrafficshowninFigure5,itiseasytodistinguishbetweenthetwo.
AthirdversionoftheFAKEMRATattemptstodisguisethenetworktrafficitproducesasHTML.
Themalicioustrafficbeginswithstringslike1.
.
56or12356.
88ThisvariantwasreferencedduringanincidentdocumentedbyAlienVaultinMarch2012inhttp://labs.
alienvault.
com/labs/index.
php/2012/alienvault-research-used-as-lure-in-targeted-attacks/.
5|FAKEMRATFIGURE6:MalicioustrafficdisguisedasHTMLtrafficThisisafairlyrudimentarydisguiseandoddbecauseyouwouldexpectHTMLtobetheresultofarequesttoawebserverandnotassomethingaclientwouldsendtoawebserver.
NetworkTrafficEncryptionThenetworkcommunicationbetweenthecompromisedcomputerandtheRATcontrollerisencrypted.
Theencryptionisthesameacrossvariantsanddoneatthebitlevel.
EachbyteisXOR-edbyeveryletterinthestring,YHCRA,androtated3bitstotherightaftereveryXORoperation.
Encryptingthecommunicationensuresthatthesuspiciousdatapassedbetweenthecompromisedhostandtheattackerscannotbeeasilyviewedinplaintext.
Thecommunicationcomesin1024-byteblobsofdatathatstartwiththe32-byteheader.
Itappearsthatattackersmayspecifyanykindoffakeheaderswithinthefirst32bytesinordertodisguisethesubsequentnetworktraffic.
Thefollowingbitsofinformationareinitiallysentbythecompromisedhostwhenthecommunicationstarts:UsernameComputernameOEMcodepageidentifierWhatlookslikeacampaigncodebutonlyforsomesamplesThecommandsarenotpreconfiguredasthemalwarereliesonthedatasentbytheserver.
Forinstance,whenaclientreceivesthecommand,0211,thissignifiesthatitshouldexecutetheaccompanyingdatainmemory.
6|FAKEMRATThefollowingarethecommandstheserverissuesandtheirmeanings:0211:Executecode.
0212:Reconnecttoreceivedata.
0213:Sleep,closesocket,andreconnect.
0214:Exit.
TodeterminetheRAT'scapabilities,weallowedtheattackerstoinfiltrateahoneypotcomputerandcapturedallofthenetworktrafficitgenerated.
Wedecryptedthenetworktrafficanddeterminedthecommandstheattackersused,whichinclude:CmdMana:CommandManagerallowsattackerstoexecuteshellcommands.
FileMan:FileManagerallowstheattackerstobrowsedirectories.
HostIn:HostInformationprovidesinformationaboutthecompromisedcomputer.
ProcMan:ProcessManagergivesattackersaccesstorunningprocesses.
RegMana:RegistryManagergivesattackersaccesstotheWindowsregistry.
Scree:Screentakesasnapshotofthedesktop.
ServiceMa:ServiceManagerallowsaccesstoservices.
Passwo:PasswordaccessesstoredpasswordslikethosesavedinInternetExplorer(IE).
UStea:Uploadsfilesfromacompromisedcomputer.
7|FAKEMRATInfrastructureTheWindowsMessengersamplesweanalyzedwereclusteredintofivegroupsthatdidnothaveoverlappinglinkages.
Fouroftheclusterswererelativelysmallandfocusedonfourdifferentdomains:vcvcvcvc.
dyndns.
orgzjhao.
dtdns.
netavira.
suroot.
com*.
googmail.
comThevcvcvcvc.
dyndns.
orgdomainisparticularlyinterestingbecausewealsofounditbeingusedasacommand-and-control(C&C)serverforProtux—awell-knownmalwarefamilythathasbeenusedinmanytargetedattacksovertheyears.
Wealsofoundthattheavira.
suroot.
comdomainusedasaC&Cserverforyetanothermalwarefamilywecall"cxgid.
"The*.
googmail.
comdomainwasslightlylargerandincludednameslikeapple12.
crabdance.
comandapple12.
co.
cc.
However,thelargestclusterrevolvedaroundthe*.
yourturbe.
orgdomainandoverlappedwiththeHTMLvariant.
WealsofoundsmallclustersoftheHTMLvariantthatrevolvedaroundthedomain,endless.
zapto.
org,whichwasdownloadedasasecond-stagemalwarebyProtux.
FIGURE7:FAKEMdomainsassociatedwiththeWindowsMessengerandHTMLvariants8|FAKEMRATMeanwhile,theYahoo!
Messengersamplesweanalyzedallaccessedfreeavg.
sytes.
net—adomainnamethatfrequentlyresolvedtodifferentIPaddresses.
FIGURE8:FAKEMdomainsassociatedwiththeYahoo!
MessengervariantThevarioussampleswecollectedappeartobelongtogroupsthatoverlappedalittle.
Thissuggeststhatratherthanbeingassociatedwithaparticularcampaign,theuseofvariousFAKEMRATscouldbedistributedamongmultiplethreatactors.
ConclusionKnowledgeoftheattacktools,techniques,andinfrastructureofadversariesiscriticalfordevelopingdefensivestrategies.
ThisresearchpaperexaminedthreevariantsofaRAT—FAKEM—thatattempttodisguisethenetworktraffictheyproducetostayundertheradar.
NowthatpopularRATslikeGh0standPoisonIvyhavebecomewell-knownandcaneasilybedetected,attackersarelookingformethodstoblendinwithlegitimatetraffic.
WhileitispossibletodistinguishthenetworktrafficFAKEMRATvariantsproduceforthelegitimateprotocolstheyaimtospoof,doingsointhecontextofalargenetworkmaynotbenoteasy.
TheRAT'sabilitytomaskthetrafficitproducesmaybeenoughtoprovideattackersenoughcovertosurvivelongerinacompromisedenvironment.
Fortunately,solutionslikeTrendMicroDeepDiscoverycanhelpnetworkadministratorsprotecttheirorganizationsfromattacksthatusetheFAKEMRATbydetectingthetrafficitsvariantsproduce.
TRENDMICROINCORPORATEDTrendMicroIncorporated(TYO:4704;TSE:4704),aglobalcloudsecurityleader,createsaworldsafeforexchangingdigitalinformationwithitsInternetcontentsecurityandthreatmanagementsolutionsforbusinessesandconsumers.
Apioneerinserversecuritywithover20years'experience,wedelivertop-rankedclient,serverandcloud-basedsecuritythatfitsourcustomers'andpartners'needs,stopsnewthreatsfaster,andprotectsdatainphysical,virtualizedandcloudenvironments.
Poweredbytheindustry-leadingTrendMicroSmartProtectionNetworkcloudcomputingsecurityinfrastructure,ourproductsandservicesstopthreatswheretheyemerge—fromtheInternet.
Theyaresupportedby1,000+threatintelligenceexpertsaroundtheglobe.
TRENDMICROINCORPORATED10101N.
DeAnzaBlvd.
Cupertino,CA95014U.
S.
tollfree:1+800.
228.
5651Phone:1+408.
257.
1500Fax:1+408.
257.
2003www.
trendmicro.
com2013byTrendMicroIncorporated.
Allrightsreserved.
TrendMicroandtheTrendMicrot-balllogoaretrademarksorregisteredtrademarksofTrendMicroIncorporated.
Allotherproductorcompanynamesmaybetrademarksorregisteredtrademarksoftheirowners.
- FIGUREhkcmd.exe相关文档
- 进程hkcmd.exe进程是什么?
- 进程hkcmd.exe进程是什么-.docx
- 进程hkcmd.exe进程是什么-
- 进程2019年hkcmd.exe进程指什么_
- 进程hkcmd.exe进程是什么
- hkcmd.exesethc.exe的解决办法
快快云:香港沙田CN2/美国Cera大宽带/日本CN2,三网直连CN2 GIA云服务器和独立服务器
快快云怎么样?快快云是一家成立于2021年的主机服务商,致力于为用户提供高性价比稳定快速的主机托管服务,快快云目前提供有香港云服务器、美国云服务器、日本云服务器、香港独立服务器、美国独立服务器,日本独立服务器。快快云专注为个人开发者用户,中小型,大型企业用户提供一站式核心网络云端服务部署,促使用户云端部署化简为零,轻松快捷运用云计算!多年云计算领域服务经验,遍布亚太地区的海量节点为业务推进提供强大...
BGPTO独服折优惠- 日本独服65折 新加坡独服75折
BGPTO是一家成立于2017年的国人主机商,从商家背景上是国内的K总和有其他投资者共同创办的商家,主营是独立服务器业务。数据中心包括美国洛杉矶Cera、新加坡、日本大阪和香港数据中心的服务器。商家对所销售服务器产品拥有自主硬件和IP资源,支持Linux和Windows。这个月,有看到商家BGPTO日本和新加坡机房独服正进行优惠促销,折扣最低65折。第一、商家机房优惠券码这次商家的活动机房是新加坡...
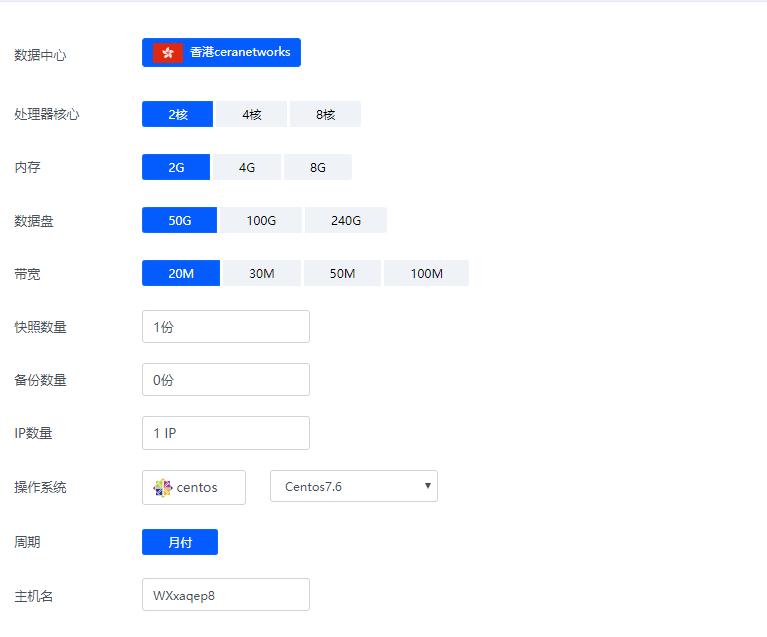
香港ceranetworks(69元/月) 2核2G 50G硬盘 20M 50M 100M 不限流量
香港ceranetworks提速啦是成立于2012年的十分老牌的一个商家这次给大家评测的是 香港ceranetworks 8核16G 100M 这款产品 提速啦老板真的是豪气每次都给高配我测试 不像别的商家每次就给1核1G,废话不多说开始跑脚本。香港ceranetworks 2核2G 50G硬盘20M 69元/月30M 99元/月50M 219元/月100M 519元/月香港ceranetwork...
hkcmd.exe为你推荐
-
360退出北京时间utc+8 13:30-14:00换成北京时间是什么时候360公司迁至天津天津360公司?360开户哪家好?360开户费多少?360推广怎么样?360效果怎么样?360和百度相比哪个更合适?人人视频总部基地落户重庆重庆总部城的项目简介支付宝注册网站在哪里注册支付宝申请支付宝账户如何申请支付宝账户资费标准电信套餐资费介绍表文档下载如何 下载 文库文件文档下载怎样把手机里的文件直接下载或复制到U盘里curl扩展大神帮忙看下centos 7.2 系统 php7.0.12的 curl 扩展怎么开启,谢谢啦35邮箱邮箱地址怎么写