performzencart
zencart 时间:2021-04-12 阅读:()
CopyrightIBMCorporation2013TrademarksLoadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage1of8Loadedpages:HowyourwebsitecaninfectvisitorswithmalwareAdeveloper'sintroductiontomaliciouswebsitesJeffOrloffJanuary15,2013Googleclaimsthat9,500websitesperdayareinfectedwithmalwaremeanttoharmthesite'svisitors.
Understandinghowmalwareinfectsawebsiteandwhatcanbedonetostopitcanhelpkeepyourvisitors'computersfreeofmalware.
Overtheyears,thetermmalwarehasbeenusedtodescribeanytypeofmalicioussoftware,includingviruses,Trojanhorses,worms,spyware,scareware,andadware.
Intheearlydaysofcomputers,malwarewasconsideredmoreaprankusedtoannoypeoplethroughdestructivebehaviorortoshowoffprogrammingskills.
Basically,themorepeopleyourmaliciousprogramcouldinfect,thegreateryourstatusincertaincircles.
Themaliciousprogramswereoftendeliveredtotheirintendedvictimsasemailattachments,sharedthroughremovablestoragemediaorthroughfile-sharingservices.
Althoughmalwareofthissortcausedawealthofproblemsforitsvictims,thedrivingforcebehinditdidnotmotivateasmanypeopletogetinvolvedbecausethepayoffwasn'taslucrativetoawidebase.
Today,thedrivingforcebehindmalwarehasshiftedtomoney.
Becausetheseattacksaredrivenbyfinancialrewards,thereismoremalwareinthewildthaneverbefore.
Notonlyaremorepeopleinvolvedinthecreationanddistributionofmalware,buttheattackshavegrownmoresophisticated.
Cyber-criminalshavelearnedhowtousemalwaretoturnlargeprofitsby:DisplayingandclickingadsStealingconfidentialdataHijackingusersessionsCompromisinguserlogincredentialsStealingfinancialinformationMakingfraudulentpurchasesCreatingspamLaunchingdenial-of-serviceattacksTodelivertheirmalicioussoftwaretoasmanyvictimsaspossible,cyber-criminalshaveturnedtowebsitesasoneoftheirprimarysourcesofdistribution.
developerWorksibm.
com/developerWorks/Loadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage2of8WhywebsitesPeoplehavelearnednottodownloadfilesattachedtoemails,andtheyhavestayedawayfrompopularfile-sharingservicesbecausesomanyfilesareinfectedwithmalware.
Onethingthatpeoplehavenotstoppeddoing,though,issurfingtheWeb.
AccordingtoInternetWorldStats(seeRelatedtopicsforalink),in2011therewere2,279,709,629activeInternetusers,andthatnumbercontinuestogrow.
Withanattacklandscapethislargeandwithsomanyusersnotbeingsuspicious,it'snowonderthatwebsiteshavebecomethefavoritemediausedtoinfectuserswithmalware.
Infact,maliciouswebsiteshavebecomesoprevalentthatGoogleblacklistsroughly6,000websiteseverydaybecausetheycarrysomesortofmalicioussoftwarethatisdangeroustovisitors.
HowmalwarespreadsthroughwebsitesThoseresponsibleforinfectingwebsiteswithmalwaredosoinoneofthreeways:Theycreateamaliciouswebsiteoftheirown.
Theyexploitavulnerabilityonthewebserverorinitsconfiguration.
Theyexploitavulnerabilityintheapplicationsthewebsiterelieson.
Becausethisarticlefocusesonwhatyoucandotopreventyourwebsitesfromfallingvictimtotheseattacks,Iaddressonlythelattertwomethods.
Afteranattackerhasfoundavulnerabilitythatheorshecansuccessfullyexploit,theattackerneedstodeterminehowheorshewilldelivermalwaretothewebsite'svisitors.
Table1listssomeofthecommonmethods.
Table1.
CommonwayswebsitesdistributemalwareMethodDescriptionDownloadsTheuseristrickedintodownloadingthemaliciouscode.
Acommontacticusedistotellthevisitorthatheorsheneedstoupdatemultimediasoftwaretoviewavideo,oravictimistrickedintodownloadingaPDForothertypeoffilethatactuallycontainsmalware.
BanneradsUsersaretrickedintodownloadingmaliciousfileswhentheyclickinfectedadsthatappearonthewebsite.
Drive-bydownloadsWhenthismethodisused,thevisitordoesnotneedtoperformanyactiononawebsiteotherthansimplyvisit.
Malwarecanbehiddeninsideinvisibleelementsonthesite,suchasiframesorunobfuscatedJavaScriptcode;itcanevenbeembeddedinmultimediafiles,suchasimages,videos,orAdobeFlashanimations.
Whenthepageloads,themalwareinfectsthevisitor'scomputerusingvulnerabilitiesinthebrowserorplug-ins.
InfectingwebsitesthroughservervulnerabilitiesInaddressingserver-basedvulnerabilities,Ilookattwoofthemorepopularwebserverapplicationsonthemarket:ApacheandMicrosoftInternetInformationServices(IIS).
Thesetwoserverspower78.
65percentofallwebsites.
ibm.
com/developerWorks/developerWorksLoadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage3of8BothApacheandIIS—oranyotherwebserver—havevulnerabilitiesthatmaliciousattackerscanexploit.
Whenattackersareabletocompromisetheserversoftwareortheserveritself,theyareabletouploadmaliciouscodeorevenentirewebpagesthatdelivermalwaretothesite'svisitors.
Examplesofvulnerabilitiesthatallowthistypeofattacktotakeplacecomefromtwoprimarysources.
VulnerabilitiesfoundinthedefaultinstallationWhenwebserversoftwareisinstalled,thedefaultconfigurationisusuallysetuptomakepublishingawebsiteeasy,notsecure.
Unnecessarymodulesandservicesmayalsobepartofawebserver'sdefaultinstallation.
Theseextrasmaygiveanattackerunrestrictedaccesstoyourwebsite'sfiles.
Eachoperatingsystem,webserversoftware,andversionhasuniquevulnerabilitiesthatcanbefoundwithasimplewebsearch.
Beforeawebsitegoeslive,anyknownvulnerabilitiesshouldbeaddressed.
BrokenauthenticationandsessionmanagementThissourceencompassesallaspectsofuserauthenticationandthemanagementofactivesessions.
AccordingtotheOpenWebApplicationSecurityProject(OWASP),"Awidearrayofaccountandsessionmanagementflawscanresultinthecompromiseofuserorsystemadministrationaccounts.
Developmentteamsfrequentlyunderestimatethecomplexityofdesigninganauthenticationandsessionmanagementschemethatadequatelyprotectscredentialsinallaspectsofthesite.
"Tomitigateagainstthistypeofvulnerability,thoseresponsiblefortheadministrationofthewebserverandsiteneedtoadheretopasswordpoliciesthatdeterminethestrength,storage,andchangecontrolsofallpasswords.
Furthermore,remotemanagementcapabilitiesforthewebservershouldbesecuredoreventurnedoffsothatusercredentialsarenotcompromisedthroughtransit.
UploadingmalwarethroughvulnerabilitiesinthewebsiteIfwebsiteswerestillstatictextandimages,itwouldbemuchmoredifficultforthebadguystousealegitimatewebsitetoserveupmalicioussoftware.
However,today'swebsitesarepoweredbydatabases,complexcode,andthird-partyapplicationsthatmaketheuserexperiencemuchricherwhileopeningthesitetoanynumberofvulnerabilities.
TakeWordPress,forexample.
Thisbloggingapplicationhaschangedhowwebsitesarecreatedbymakingiteasyforanyonewithabitoftechnicalknowledgetocreateamultimedia-rich,interactivewebsite.
Itissopopularthatitpowersmorethan50millionwebsites.
WordPress'seaseofuse,however,wasalsothecauseofarecentoutbreak,inwhichbetween30,000and100,000sitesrunningtheapplicationredirectedvictimstomalicioussites.
Sitesthatinstalledaparticularplug-infoundtheirpagesinfectedwithcodethatredirectedvisitorstoanothersite.
Thissitewouldtheninfectthevictim'scomputerwithmalwarebasedonthedeveloperWorksibm.
com/developerWorks/Loadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage4of8operatingsystemandapplicationsthatthecomputerwasrunning.
TheFlashbackTrojanthatinfectedmorethan500,000Macswasoneofthemaliciousprogramsthatspreadthroughthisexploit.
ExampleslikethisarenotlimitedtoWordPress,however.
ApplicationslikeJoomla!
,Drupal,MediaWiki,Magento,ZenCart,andmanyothershaveallhadvulnerabilitiesinthemthatallowmalicioushackerstouploadmalwaretothesesitestobedistributedtovisitors.
PreventingattacksagainstwebapplicationsForattackerstoexploitawebapplication,theymustfindsometypeofvulnerability.
Unfortunatelyfortheownersofwebsites,therearesomanydifferenttypesofknownvulnerabilitiesthattheycan'tallbelistedhere.
Someyoumaybefamiliarwith,however:Cross-sitescripting(XSS)StructuredQueryLanguageinjectionsCross-siterequestforgeryinjectionsURLredirectsCodeexecutionCookiemanipulationAndthelistgoeson.
MitigatingwebapplicationthreatsFortunately,therearewaystofindoutifyoursiteisvulnerabletoanyoftheknownexploitsbyusingwebapplication-penetrationtechniques.
Bythoroughlytestingawebsiteforknownvulnerabilities,youcanaddressthesethreatsbeforeanattackisabletomanipulatethemtodistributemalwaretoyourvisitors.
Youcandosousingavarietyofopensourceorcommercialtools,oryoucanoutsourcetheservicetocompaniesthatspecializeinthis.
Althoughpenetrationtestingwillhelpidentifyproblemsthatneedtobefixedinyourwebsite'scode,webapplicationfirewallscanhelpstopthreatsbeforetheyreachyoursite.
Byidentifyingknownattackpatterns,youcanthwarttheeffortsofmalicioushackersbeforetheyareabletocausedamagetoyoursite.
Moreadvancedwebapplicationfirewallscanevenprovideprotectionagainstunknown,zero-daythreatsbyidentifyingillicittraffic.
LimitingvulnerabilitiesinApacheWheneveraserverisconfigured,itisabestpracticetoinstallonlythemodulesandapplicationsthatarenecessary.
Bynow,thisisnotonlyabestpracticebutacommonpractice.
ThereareotherbasicstepsthatyoushouldtaketolimitthevulnerabilitiesthatexistinApache'swebserver.
Throughoutthecourseofthisarticle,IusethecommandsrelevanttotheUbuntudistributionofLinux.
ForApacherunningonotheroperatingsystemsordistributions,simplysearchforthestepsrequiredtoperformeachtask.
ibm.
com/developerWorks/developerWorksLoadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage5of8DisablethebannerBydefault,Apacheshowsitsnameandversionnumberuponawebrequest,announcingtoanypotentialattackerswhatexactlythewebsiteisrunning.
Disablingthatbannermakesitmoredifficulttopinpointanyothervulnerabilities.
Youcandosobynavigatingto/etc/apache2/apache2.
confanddisablingtheServerSignatureandServerTokensentries.
DisabledirectoryindexingAnotherdefaultistheabilitytoprintalistoffilesfoundinthewebsitedirectories.
Thisfeatureletsanattackermapyourserverandidentifypotentiallyvulnerablefiles.
Tomitigateagainstthisissue,youneedtodisabletheautoindexmodule.
Simplyopentheterminalandusethefollowingcommands:rm-f/etc/apache2/mods-enabled/autoindex.
loadrm-f/etc/apache2/mods-enabled/autoindex.
confDisableWebDAVWeb-basedDistributedAuthoringandVersioning(WebDAV)isthefile-accessprotocolofHTTPthatallowsfortheuploading,downloading,andchangingoffilecontentsonawebsite.
Inanyproductionwebsite,WebDAVshouldbedisabledsothatanattackercannotchangeyourfilestouploadmaliciouscode.
Usingtheterminal,youdisablethedav,dav_fs,anddav_lockfilesbyremovingthemwiththefollowing:rm-f/etc/apache2/mods-enabled/dav.
loadrm-f/etc/apache2/mods-enabled/dav_fs.
confrm-f/etc/apache2/mods-enabled/dav_fs.
loadrm-f/etc/apache2/mods-enabled/dav_lock.
loadTurnofftheTRACEHTTPrequestTheHTTPTRACErequestcanbetrickedintoprintingsessioncookiesandthisinformationusedtohijackausersessiontolaunchanXSSattack.
Youcandisablethistracebynavigatingtothe/etc/apache2/apache2.
conffileandmakingsurethatTraceEnablereadsTraceEnableoff.
LimitingvulnerabilitiesinIISOnethingthatmakesWindowsServerproductssoattractivetotheconsumermarketistheireaseofinstallation.
UsingIIS,acompanycangetawebserverupandrunningwithafewclicks.
Whentheserversoftwareisinstalledoutofthebox,thereislittleneedforconfiguration:It'sdoneforyou.
Toaddresssecurityissuesinitswebserverproduct,MicrosofthasmadesignificantchangestohowIISisconfiguredandwhatisinstalledbydefault.
Thereare,however,somestepsthatyoucantaketobetterprotectagainstthreats.
developerWorksibm.
com/developerWorks/Loadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage6of8InstallantimalwaresoftwareCodeRedandNimdawerebothwormsthatattackedtheWindowsServeroperatingsystem,andbothdidagreatdealofdamage.
Withoutadequateantimalwareprotectiononthehostoperatingsystemitself,awebsitequicklybecomesvulnerabletoattack.
Usingkeystrokeloggers,Trojans,andothermalware,attackerscannotonlyeasilycompromisethewebadministrator'slogincredentials,buttheyalsohavetheabilitytoinsertmaliciouscodeintothefilesthatareserveduptopeoplevisitingthesite.
Afterantimalwaresoftwareisinstalled,itshouldbeimmediatelyupdatedandthenrunbeforeanywebsitefilesareuploaded.
Ifanythingisfound,allpasswordsshouldimmediatelybechanged.
UpdateeverythingelseBeforeawebserverrunningIISgoeslive,besuretoupdatetheoperatingsystemsoftwareandwebserversoftwarewiththelatestupdatesfromMicrosoft.
TheseupdatesusuallycontainpatchesthataddressvulnerabilitiesspecifictoMicrosoftproducts.
CleaningupafteranattackWhenawebsiteisguiltyofcausingharmtoitsvisitors,youmusttakestepsimmediately.
Tobeginwith,takedownandquarantineyoursite.
Ifyouneedtohaveyoursiteupandrunningsoastoavoidinterruptingyourbusiness,relyonabackupthatisverifiedmalwarefree.
Whenyourwebpresenceistakencareof,it'stimetocleantheinfectedfiles.
Someinfectionsrequireonlytheremovalofafewlinesofcode,whilemoresophisticatedattacksmightrequirethatyourewritetheentirefile.
Whateverstepsarenecessarytoremovemalwarefromasiteneedtobetakenatthispoint.
RepairyourreputationWhenGoogleandtheothersearchenginesfindasitethatisservingmalware,theycanpullitfromtheirresults.
Thiscanhavedevastatingeffectsonabusiness.
Afterallmalwarehasbeenremovedandanyvulnerabilitiespatched,submitthesitetothesearchenginesforreview.
Iftheydeterminethatitisnolongerathreattoanyvisitors,thewebsitecanbere-listedandtrafficfromthesearchenginecanberestored.
Ifthemalwareinfectionhascompromiseduseraccountinformation,allusersshouldbenotifiedimmediatelysothattheycandealwithanyramifications.
Inaddition,anorganizationwillneedtoseewhetheranylawsorregulationshavebeenviolatedasaresultofthebreachandtakeappropriatemeasurestomitigateanynegativeeffectsandkeepthemincompliance.
ConclusionInareportbyDasient,approximately1.
1millionwebsiteswerefoundtohavesometypeofmalwareinthefourthquarterof2010.
Otherstudiesshowthat85percentofallmalwarecomesibm.
com/developerWorks/developerWorksLoadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage7of8fromtheWeb.
Now,itwouldbeeasytowritethisoffifthesitesthatwerecausingalltheproblemshadamaliciousintentfromthebeginning.
Unfortunately,itisthesmallbusinesswebsite,thechurchwebsite,oreventhewell-respectednewswebsitethatisresponsibleforinfectingsomanycomputers.
Theresponsibilityforprotectingwebsitesagainstattackisfallingontheshouldersofthewebdeveloper.
Thedaysofsittingbackandwritingawesomecodeareover.
Now,thedeveloperneedstomakesurethathisorhercodeisfunctionalandsecure.
Thetechniqueslistedinthisarticlewillcertainlyhelpthedeveloperwhodoesn'tunderstandwebsitesecuritybuildafoundationforhisorherknowledge,butitshouldn'tstophere.
Thethreatlandscapechangesdaily.
Aszero-dayexploitsemergeandcyber-criminalsadapttocountermeasures,webdeveloperstooneedtoadaptandbeonthelookoutforhowtheycanbettersecuretheirsites.
developerWorksibm.
com/developerWorks/Loadedpages:HowyourwebsitecaninfectvisitorswithmalwarePage8of8RelatedtopicsInternetWorldStats:FindmoreInternetstatistics.
Googleblacklists:ReadmoreaboutwhyGoogleblacklistsroughly6,000websiteseveryday.
PrevalenceofApacheandIIS:AccordingtoNetcraft,ApacheandIISpower78.
65percentofallwebsites.
WordPress:ReadmoreabouttheprevalenceofWordPress.
"HardeningtheLinuxserver:"LearnhowtohardenyourLinuxserver(developerWorks,December2008).
OWASPTopTenWebApplicationSecurityThreats:LearnmoreaboutOWASPanditswork.
CopyrightIBMCorporation2013(www.
ibm.
com/legal/copytrade.
shtml)Trademarks(www.
ibm.
com/developerworks/ibm/trademarks/)
- performzencart相关文档
- zencart今天安装zencart遇到这个问题。要登陆后台的url的时候,出现这个问题。这个怎么解决?
- zencartzencart怎么安装语言包?
- activitieszencart
- dommielzencart
- crowdsourcedzencart
- ashazencart
湖北50G防御物理服务器( 199元/月 ),国内便宜的高防服务器
4324云是成立于2012年的老牌商家,主要经营国内服务器资源,是目前国内实力很强的商家,从价格上就可以看出来商家实力,这次商家给大家带来了全网最便宜的物理服务器。只能说用叹为观止形容。官网地址 点击进入由于是活动套餐 本款产品需要联系QQ客服 购买 QQ 800083597 QQ 2772347271CPU内存硬盘带宽IP防御价格e5 2630 12核16GBSSD 500GB30M1个IP...
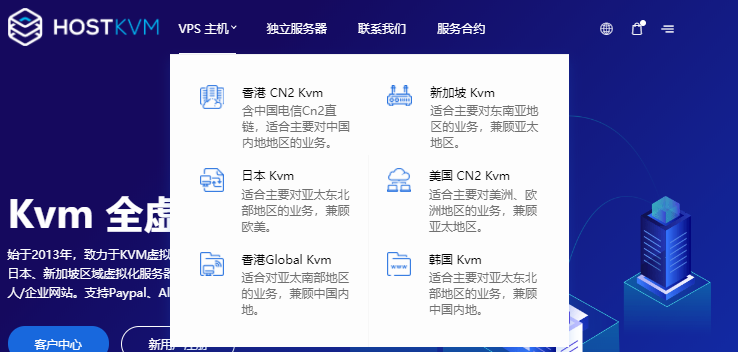
HostKvm开年促销:香港国际/美国洛杉矶VPS七折,其他机房八折
HostKvm也发布了开年促销方案,针对香港国际和美国洛杉矶两个机房的VPS主机提供7折优惠码,其他机房业务提供8折优惠码。商家成立于2013年,提供基于KVM架构的VPS主机,可选数据中心包括日本、新加坡、韩国、美国、中国香港等多个地区机房,均为国内直连或优化线路,延迟较低,适合建站或者远程办公等。下面列出几款主机配置信息。美国洛杉矶套餐:美国 US-Plan1CPU:1core内存:2GB硬盘...
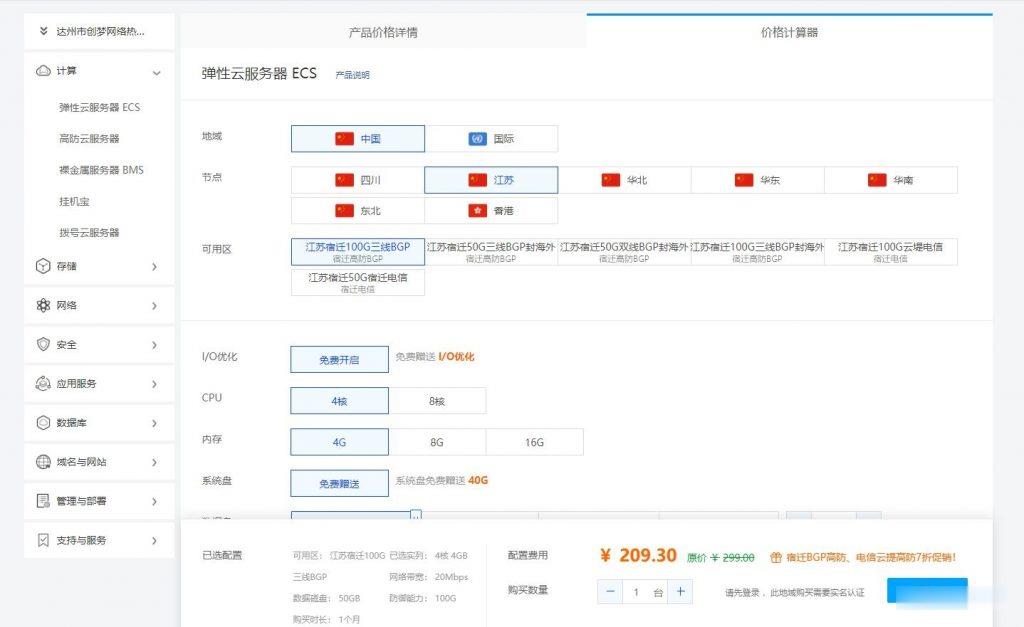
创梦网络-江苏宿迁BGP云服务器100G高防资源,全程ceph集群存储,安全可靠,数据有保证,防护真实,现在购买7折促销,续费同价!
官方网站:点击访问创梦网络宿迁BGP高防活动方案:机房CPU内存硬盘带宽IP防护流量原价活动价开通方式宿迁BGP4vCPU4G40G+50G20Mbps1个100G不限流量299元/月 209.3元/月点击自助购买成都电信优化线路8vCPU8G40G+50G20Mbps1个100G不限流量399元/月 279.3元/月点击自助购买成都电信优化线路8vCPU16G40G+50G2...
zencart为你推荐
-
戏曲网易yeahcentos6.5怎么用u盘安装centos6.5支付宝蜻蜓发布蜻蜓支付可以代理么连接cuteftp三友网有了解唐山三友集团的吗?大学生待遇如何,工资收入,福利保障,工作环境等等可信网站网站备案了,还要验证可信网站吗?他们有什么区别工具条工具栏不见了怎么办如何发帖子请问在网上发帖子怎么发?网站后台密码破解我找到了网站的后台地址,怎么才可以破解密码无忧登陆无忧登陆怎么用??