encryptionwin7配置
win7配置 时间:2021-03-27 阅读:()
MicrosoftNetworkSecurityWindows7:CurrentEventsintheWorldofWindowsForensicsTroyLarsonSeniorForensicProgramManagerNetworkSecurity,MicrosoftCorp.
MicrosoftNetworkSecurityWhereAreWeNowVista&Windows2008–BitLocker.
–Format-Wipesthevolume.
–EXFAT.
–EventLogging—format,system,scheme.
–VirtualFolders&Registry.
–VolumeShadowCopy.
–Links,HardandSymbolic.
–ChangeJournal.
–RecycleBin.
–Superfetch.
MicrosoftNetworkSecurityWhereAreWeNowWindows7&Window2008R2–UpdatedBitLocker.
–BitLockerToGo.
–VHDs—Bootfrom,mountas"Disks.
"–XPMode.
–FlashMediaEnhancements.
–Libraries,StickyNotes,JumpLists.
–ServiceandDrivertriggers.
–I.
E.
8,InPrivateBrowsing,TabandSessionRecovery.
–EvenmoreVolumeShadowCopy.
MicrosoftNetworkSecurityDigitalForensicsSubjectMatterExpertise"Stack"ThankstoEoghanCasey.
FileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityWindows7"Disk"Notedisksignature:2E1400320x1b8-1bbMicrosoftNetworkSecurityWindows7"Disk"HKEY_LOCAL_MACHINE\HARDWARE\DESCRIPTION\System\MultifunctionAdapter\0\DiskController\0\DiskPeripheral\0Diskpart>AutomountscrubMicrosoftNetworkSecurityVista"Disk"HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Enum\STORAGE\Volume\1&19f7e59c&0&Signature2E140032Offset100000Length114FD00000MicrosoftNetworkSecurityPartitionsandVolumesFileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"VirtualHardDrivesCreateAttachDetachDeleteMicrosoftNetworkSecurityBitLocker:Windows7Duringinstalling,Windows7createsa"SystemReserved"volume—enablingsetupofBitLocker.
InVista,theSystemvolumewasgenerally1.
5GBormore.
MicrosoftNetworkSecurityBitLocker:VistaPhysicallevelviewoftheheaderofthebootsectorofaVistaBitLockerprotectedvolume:–0xEB52902D4656452D46532D–R-FVE-FS-MicrosoftNetworkSecurityBitLocker:Windows7PhysicallevelviewoftheheaderofthebootsectorofaWindows7BitLockerprotectedvolume:–0xEB58902D4656452D46532D–X-FVE-FS-MicrosoftNetworkSecurityBitLocker:Windows7Vista&Windows2008cannotunlockBitLockervolumescreatedwithWindows7or2008R2.
ForensicstoolsmaynotrecognizethenewBitLockervolumeheader.
MustuseWindows7or2008R2toopen(andimage)BitLockervolumesfromWindows7or2008R2.
MicrosoftNetworkSecurityBitLockerRevieworImagingFileSystemDriverFvevol.
sysVolumeManagerApplicationUserModeKernelModeFVEVOL.
SYSsitsunderneaththefilesystemdriverandperformsallencryption/decryption.
Oncebooted,Windows(andtheuser)seesnodifferenceinexperience.
Theencryption/decryptionhappensatbelowthefilesystem.
MicrosoftNetworkSecurityBitLockerRevieworImagingFileSystemDriverFvevol.
sysVolumeManagerApplicationUserModeKernelModeMicrosoftNetworkSecurityBitLockerRevieworImagingThe"More/Lessinformation"buttonwillprovidetheBitLockervolumerecoverykeyidentification.
MicrosoftNetworkSecurityBitLockerRevieworImagingBitLockerRecoveryKey783F5FF9-18D4-4C64-AD4A-CD3075CB8335.
txt:BitLockerDriveEncryptionRecoveryKeyTherecoverykeyisusedtorecoverthedataonaBitLockerprotecteddrive.
Toverifythatthisisthecorrectrecoverykeycomparetheidentificationwithwhatispresentedontherecoveryscreen.
Recoverykeyidentification:783F5FF9-18D4-4CFullrecoverykeyidentification:783F5FF9-18D4-4C64-AD4A-CD3075CB8335BitLockerRecoveryKey:528748-036938-506726-199056-621005-314512-037290-524293MicrosoftNetworkSecurityBitLockerRevieworImagingEntertherecoverykeyexactly.
MicrosoftNetworkSecurityBitLockerRevieworImagingViewedorimagedaspartofaphysicaldisk,BitLockervolumesappearencrypted.
MicrosoftNetworkSecurityBitLockerRevieworImagingToviewaBitLockervolumeasitappearsinitsunlockedstate,addressitasalogicalvolume.
MicrosoftNetworkSecurityBitLockerRevieworImagingMicrosoftNetworkSecurityFileSystemsFileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityFileSystemsSinceVistaSP1,Formatwipeswhileitformats.
http://support.
microsoft.
com/kb/941961Diskpart.
exe>CleanallMicrosoftNetworkSecurityFileSystems-Vista&Windows7NTFS–Symboliclinkstofiles,folders,andUNCpaths.
Bewarethe"ApplicationData"recursionloop.
Cf.
Linkfiles.
–Hardlinksareextensivelyused(\Winsxs).
–Disabledbydefault:UpdateLastAccessDate.
–Enabledbydefault:TheNTFSChangeJournal($USN:$J).
TransactionalNTFS($Tops:$T).
MicrosoftNetworkSecurityFileSystems-Vista&Windows7ThevolumeheaderofanEXFATvolume.
DoyourforensicstoolsreadEXFATMicrosoftNetworkSecurityOSArtifactsFileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityOSArtifacts—Recycle.
Bin[Volume]:\$Recycle.
Bin–$Recycle.
BinisvisibleinExplorer(viewhiddenfiles).
–PeruserstoreinasubfoldernamedwithaccountSID.
–NomoreInfo2files.
–Whenafileisdeleted—movedtotheRecycleBin—itgeneratestwofilesintheRecycleBin.
–$Iand$Rfiles.
$Ior$Rfollowedbyseveralrandomcharacters,thenoriginalextension.
Therandomcharactersarethesameforeach$I/$Rpair.
$Ifilemaintainstheoriginalnameandpath,aswellasthedeleteddate.
$Rfileretainstheoriginalfiledatastreamandotherattributes.
Thenameattributeischangedto$R******.
ext.
MicrosoftNetworkSecurityOSArtifacts—Recycle.
BinNotethedeleteddate(inblue).
MicrosoftNetworkSecurityOSArtifacts—Recycle.
BinMicrosoftNetworkSecurityOSArtifacts—FolderVirtualization–PartofUserAccessControl—Standardusercannotwritetocertainprotectedfolders.
C:\WindowsC:\ProgramFilesC:\ProgramData–Toallowstandardusertofunction,anywritestoprotectedfoldersare"virtualized"andwrittentoC:\Users\[user]\AppData\Local\VirtualStoreMicrosoftNetworkSecurityOSArtifacts—RegistryVirtualizationVirtualize(HKEY_LOCAL_MACHINE\SOFTWARE)Non-administratorwritesareredirectto:HKEY_CURRENT_USER\Software\Classes\VirtualStore\MACHINE\SOFTWARE\Keysexcludedfromvirtualization–HKEY_LOCAL_MACHINE\Software\Classes–HKEY_LOCAL_MACHINE\Software\Microsoft\Windows–HKEY_LOCAL_MACHINE\Software\Microsoft\WindowsNTMicrosoftNetworkSecurityOSArtifacts—RegistryVirtualizationLocationoftheregistryhivefilefortheVirtualStore–IsNOTtheuser'sNTUSER.
DAT–Itisstoredintheuser'sUsrClass.
dat\Users\[user]\AppData\Local\Microsoft\Windows\UsrClass.
datInvestigationofVista-Windows2008R2requirestheinvestigatortoexamineatleasttwoaccountspecificregistryhivefilesforeachuseraccount.
–NTUSER.
DAT–UsrClass.
datMicrosoftNetworkSecurityOSArtifacts—LibrariesMicrosoftNetworkSecurityOSArtifacts—Libraries\Users\[account]\AppData\Roaming\Microsoft\Windows\Libraries.
MicrosoftNetworkSecurityOSArtifacts—LibrariesLibrariesareXMLfiles.
MicrosoftNetworkSecurityOSArtifacts—LibrariesMicrosoftNetworkSecurityOSArtifacts—ShellThe"Recent"foldercontainslinkfilesandtwosubfoldersat\User\[Account]\AppData\Roaming\Microsoft\Windows\Recent.
MicrosoftNetworkSecurityOSArtifacts—ShellMicrosoftNetworkSecurityOSArtifacts—Shell"AutomaticDestination"filesareintheStructuredStoragefileformat.
MicrosoftNetworkSecurityOSArtifacts—ShellMicrosoftNetworkSecurityOSArtifacts—ShellMicrosoftNetworkSecurityOSArtifacts—ChkdskLogs\SystemVolumeInformation\ChkdskMicrosoftNetworkSecurityOSArtifacts—Superfetch\Windows\PrefetchMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyVolumeshadowcopiesarebitleveldifferentialbackupsofavolume.
–16KBblocks.
–Copyonwrite.
–VolumeShadowcopy"files"are"difference"files.
TheshadowcopyserviceisenabledbydefaultonVistaandWindows7,butnotonWindows2008or2008R2.
"Differencefiles"resideintheSystemVolumeInformationfolder.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyShadowcopiesarethesourcedataforRestorePointsandtheRestorePreviousVersionsfeatures.
Usedinbackupoperations.
Shadowcopiesprovidea"snapshot"ofavolumeataparticulartime.
Shadowcopiescanshowhowfileshavebeenaltered.
Shadowcopiescanretaindatathathaslaterbeendeleted,wiped,orencrypted.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyVolumeshadowcopiesdonotcontainacompleteimageofeverythingthatwasonthevolumeatthetimetheshadowcopywasmade.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyTheVolumeShadowCopydifferencefilesaremaintainedin"\SystemVolumeInformation"alongwithotherVSSdatafiles,includinganewregistryhive.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopy\SystemVolumeInformation\Syscache.
hveMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyvssadminlistshadows/for=[volume]:MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyShadowcopiescanbeexposedthroughsymboliclinks.
Mklink/dC:\{test-shadow}\\\GLOBALROOT\Device\HarddiskVolumeShadowCopy3\MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyVolumeShadowscanbemounteddirectlyasnetworkshares.
netsharetestshadow=\\.
\HarddiskVolumeShadowCopy11\MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopy>psexec\\[computername]vssadminlistshadows/for=C:>psexec\\[computername]netsharetestshadow=\\.
\HarddiskVolumeShadowCopy20\PsExecv1.
94-Executeprocessesremotely.
.
.
testshadowwassharedsuccessfully.
netexitedon[computername]witherrorcode0.
>robocopy/S/R:1/W:1/LOG:D:\VSStestcopylog.
txt\\[computername]\testshadowD:\vssTestLogFile:D:\VSStestcopylog.
txt.
.
.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyOtherwaystocallshadowcopies:–\\localhost\C$\Users\troyla\Downloads(Yesterday,July20,2009,12:00AM)–\\localhost\C$\@GMT-2009.
07.
17-08.
45.
26\–MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyC:\Users\Troyla\Desktop\fau-1.
3.
0.
2390a\fau\FAU.
x64>ddif=\\.
\HarddiskVolumeShadowCopy11of=E:\shadow11.
dd–localwrtTheVistaFirewallFirewallisactivewithexceptions.
Copying\\.
\HarddiskVolumeShadowCopy11toE:\shadow11.
ddOutput:E:\shadow11.
dd136256155648bytes129943+1recordsin129943+1recordsout136256155648byteswrittenSucceeded!
C:\Users\Troyla\Desktop\fau-1.
3.
0.
2390a\fau\FAU.
x64>Shadowcopiescanbeimaged.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyImagesofshadowcopiescanbeopenedinforensicstoolsandappearaslogicalvolumes.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyDatathathasbeendeletedcanbecapturedbyshadowcopiesandavailableforretrievalinshadowcopyimages.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyEveryshadowcopydatasetshouldapproximatethesizeoftheoriginalvolume.
Amountofcasedata=(numberofshadowcopies)x(sizeofthevolume)+(sizeofthevolume).
10shadowcopies=692GBMicrosoftNetworkSecurityApplications—I.
E.
8FileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityApplications—I.
E.
8"C:\ProgramFiles(x86)\InternetExplorer\iexplore.
exe"-privateMicrosoftNetworkSecurityApplications—I.
E.
8Cachedataappearstobewritten,thendeleted.
MicrosoftNetworkSecurityApplications—I.
E.
8ResidualcachefilesfromInPrivatebrowsing.
MicrosoftNetworkSecurityApplications—I.
E.
8Tabandsessionrecovery—anewsourceforhistoricalbrowsinginformation.
\User\[Account]\AppData\Local\Microsoft\InternetExplorer\RecoveryMicrosoftNetworkSecurityApplications—I.
E.
8Recoveryfile:NotetheStructuredStoragefileformat.
MicrosoftNetworkSecurityApplications—I.
E.
8MicrosoftNetworkSecurity2009MicrosoftCorporation.
Allrightsreserved.
Microsoft,Windows,WindowsVistaandotherproductnamesareormayberegisteredtrademarksand/ortrademarksintheU.
S.
and/orothercountries.
TheinformationhereinisforinformationalpurposesonlyandrepresentsthecurrentviewofMicrosoftCorporationasofthedateofthispresentation.
BecauseMicrosoftmustrespondtochangingmarketconditions,itshouldnotbeinterpretedtobeacommitmentonthepartofMicrosoft,andMicrosoftcannotguaranteetheaccuracyofanyinformationprovidedafterthedateofthispresentation.
MICROSOFTMAKESNOWARRANTIES,EXPRESS,IMPLIEDORSTATUTORY,ASTOTHEINFORMATIONINTHISPRESENTATION.
MicrosoftNetworkSecurityWhereAreWeNowVista&Windows2008–BitLocker.
–Format-Wipesthevolume.
–EXFAT.
–EventLogging—format,system,scheme.
–VirtualFolders&Registry.
–VolumeShadowCopy.
–Links,HardandSymbolic.
–ChangeJournal.
–RecycleBin.
–Superfetch.
MicrosoftNetworkSecurityWhereAreWeNowWindows7&Window2008R2–UpdatedBitLocker.
–BitLockerToGo.
–VHDs—Bootfrom,mountas"Disks.
"–XPMode.
–FlashMediaEnhancements.
–Libraries,StickyNotes,JumpLists.
–ServiceandDrivertriggers.
–I.
E.
8,InPrivateBrowsing,TabandSessionRecovery.
–EvenmoreVolumeShadowCopy.
MicrosoftNetworkSecurityDigitalForensicsSubjectMatterExpertise"Stack"ThankstoEoghanCasey.
FileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityWindows7"Disk"Notedisksignature:2E1400320x1b8-1bbMicrosoftNetworkSecurityWindows7"Disk"HKEY_LOCAL_MACHINE\HARDWARE\DESCRIPTION\System\MultifunctionAdapter\0\DiskController\0\DiskPeripheral\0Diskpart>AutomountscrubMicrosoftNetworkSecurityVista"Disk"HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Enum\STORAGE\Volume\1&19f7e59c&0&Signature2E140032Offset100000Length114FD00000MicrosoftNetworkSecurityPartitionsandVolumesFileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"VirtualHardDrivesCreateAttachDetachDeleteMicrosoftNetworkSecurityBitLocker:Windows7Duringinstalling,Windows7createsa"SystemReserved"volume—enablingsetupofBitLocker.
InVista,theSystemvolumewasgenerally1.
5GBormore.
MicrosoftNetworkSecurityBitLocker:VistaPhysicallevelviewoftheheaderofthebootsectorofaVistaBitLockerprotectedvolume:–0xEB52902D4656452D46532D–R-FVE-FS-MicrosoftNetworkSecurityBitLocker:Windows7PhysicallevelviewoftheheaderofthebootsectorofaWindows7BitLockerprotectedvolume:–0xEB58902D4656452D46532D–X-FVE-FS-MicrosoftNetworkSecurityBitLocker:Windows7Vista&Windows2008cannotunlockBitLockervolumescreatedwithWindows7or2008R2.
ForensicstoolsmaynotrecognizethenewBitLockervolumeheader.
MustuseWindows7or2008R2toopen(andimage)BitLockervolumesfromWindows7or2008R2.
MicrosoftNetworkSecurityBitLockerRevieworImagingFileSystemDriverFvevol.
sysVolumeManagerApplicationUserModeKernelModeFVEVOL.
SYSsitsunderneaththefilesystemdriverandperformsallencryption/decryption.
Oncebooted,Windows(andtheuser)seesnodifferenceinexperience.
Theencryption/decryptionhappensatbelowthefilesystem.
MicrosoftNetworkSecurityBitLockerRevieworImagingFileSystemDriverFvevol.
sysVolumeManagerApplicationUserModeKernelModeMicrosoftNetworkSecurityBitLockerRevieworImagingThe"More/Lessinformation"buttonwillprovidetheBitLockervolumerecoverykeyidentification.
MicrosoftNetworkSecurityBitLockerRevieworImagingBitLockerRecoveryKey783F5FF9-18D4-4C64-AD4A-CD3075CB8335.
txt:BitLockerDriveEncryptionRecoveryKeyTherecoverykeyisusedtorecoverthedataonaBitLockerprotecteddrive.
Toverifythatthisisthecorrectrecoverykeycomparetheidentificationwithwhatispresentedontherecoveryscreen.
Recoverykeyidentification:783F5FF9-18D4-4CFullrecoverykeyidentification:783F5FF9-18D4-4C64-AD4A-CD3075CB8335BitLockerRecoveryKey:528748-036938-506726-199056-621005-314512-037290-524293MicrosoftNetworkSecurityBitLockerRevieworImagingEntertherecoverykeyexactly.
MicrosoftNetworkSecurityBitLockerRevieworImagingViewedorimagedaspartofaphysicaldisk,BitLockervolumesappearencrypted.
MicrosoftNetworkSecurityBitLockerRevieworImagingToviewaBitLockervolumeasitappearsinitsunlockedstate,addressitasalogicalvolume.
MicrosoftNetworkSecurityBitLockerRevieworImagingMicrosoftNetworkSecurityFileSystemsFileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityFileSystemsSinceVistaSP1,Formatwipeswhileitformats.
http://support.
microsoft.
com/kb/941961Diskpart.
exe>CleanallMicrosoftNetworkSecurityFileSystems-Vista&Windows7NTFS–Symboliclinkstofiles,folders,andUNCpaths.
Bewarethe"ApplicationData"recursionloop.
Cf.
Linkfiles.
–Hardlinksareextensivelyused(\Winsxs).
–Disabledbydefault:UpdateLastAccessDate.
–Enabledbydefault:TheNTFSChangeJournal($USN:$J).
TransactionalNTFS($Tops:$T).
MicrosoftNetworkSecurityFileSystems-Vista&Windows7ThevolumeheaderofanEXFATvolume.
DoyourforensicstoolsreadEXFATMicrosoftNetworkSecurityOSArtifactsFileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityOSArtifacts—Recycle.
Bin[Volume]:\$Recycle.
Bin–$Recycle.
BinisvisibleinExplorer(viewhiddenfiles).
–PeruserstoreinasubfoldernamedwithaccountSID.
–NomoreInfo2files.
–Whenafileisdeleted—movedtotheRecycleBin—itgeneratestwofilesintheRecycleBin.
–$Iand$Rfiles.
$Ior$Rfollowedbyseveralrandomcharacters,thenoriginalextension.
Therandomcharactersarethesameforeach$I/$Rpair.
$Ifilemaintainstheoriginalnameandpath,aswellasthedeleteddate.
$Rfileretainstheoriginalfiledatastreamandotherattributes.
Thenameattributeischangedto$R******.
ext.
MicrosoftNetworkSecurityOSArtifacts—Recycle.
BinNotethedeleteddate(inblue).
MicrosoftNetworkSecurityOSArtifacts—Recycle.
BinMicrosoftNetworkSecurityOSArtifacts—FolderVirtualization–PartofUserAccessControl—Standardusercannotwritetocertainprotectedfolders.
C:\WindowsC:\ProgramFilesC:\ProgramData–Toallowstandardusertofunction,anywritestoprotectedfoldersare"virtualized"andwrittentoC:\Users\[user]\AppData\Local\VirtualStoreMicrosoftNetworkSecurityOSArtifacts—RegistryVirtualizationVirtualize(HKEY_LOCAL_MACHINE\SOFTWARE)Non-administratorwritesareredirectto:HKEY_CURRENT_USER\Software\Classes\VirtualStore\MACHINE\SOFTWARE\Keysexcludedfromvirtualization–HKEY_LOCAL_MACHINE\Software\Classes–HKEY_LOCAL_MACHINE\Software\Microsoft\Windows–HKEY_LOCAL_MACHINE\Software\Microsoft\WindowsNTMicrosoftNetworkSecurityOSArtifacts—RegistryVirtualizationLocationoftheregistryhivefilefortheVirtualStore–IsNOTtheuser'sNTUSER.
DAT–Itisstoredintheuser'sUsrClass.
dat\Users\[user]\AppData\Local\Microsoft\Windows\UsrClass.
datInvestigationofVista-Windows2008R2requirestheinvestigatortoexamineatleasttwoaccountspecificregistryhivefilesforeachuseraccount.
–NTUSER.
DAT–UsrClass.
datMicrosoftNetworkSecurityOSArtifacts—LibrariesMicrosoftNetworkSecurityOSArtifacts—Libraries\Users\[account]\AppData\Roaming\Microsoft\Windows\Libraries.
MicrosoftNetworkSecurityOSArtifacts—LibrariesLibrariesareXMLfiles.
MicrosoftNetworkSecurityOSArtifacts—LibrariesMicrosoftNetworkSecurityOSArtifacts—ShellThe"Recent"foldercontainslinkfilesandtwosubfoldersat\User\[Account]\AppData\Roaming\Microsoft\Windows\Recent.
MicrosoftNetworkSecurityOSArtifacts—ShellMicrosoftNetworkSecurityOSArtifacts—Shell"AutomaticDestination"filesareintheStructuredStoragefileformat.
MicrosoftNetworkSecurityOSArtifacts—ShellMicrosoftNetworkSecurityOSArtifacts—ShellMicrosoftNetworkSecurityOSArtifacts—ChkdskLogs\SystemVolumeInformation\ChkdskMicrosoftNetworkSecurityOSArtifacts—Superfetch\Windows\PrefetchMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyVolumeshadowcopiesarebitleveldifferentialbackupsofavolume.
–16KBblocks.
–Copyonwrite.
–VolumeShadowcopy"files"are"difference"files.
TheshadowcopyserviceisenabledbydefaultonVistaandWindows7,butnotonWindows2008or2008R2.
"Differencefiles"resideintheSystemVolumeInformationfolder.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyShadowcopiesarethesourcedataforRestorePointsandtheRestorePreviousVersionsfeatures.
Usedinbackupoperations.
Shadowcopiesprovidea"snapshot"ofavolumeataparticulartime.
Shadowcopiescanshowhowfileshavebeenaltered.
Shadowcopiescanretaindatathathaslaterbeendeleted,wiped,orencrypted.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyVolumeshadowcopiesdonotcontainacompleteimageofeverythingthatwasonthevolumeatthetimetheshadowcopywasmade.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyTheVolumeShadowCopydifferencefilesaremaintainedin"\SystemVolumeInformation"alongwithotherVSSdatafiles,includinganewregistryhive.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopy\SystemVolumeInformation\Syscache.
hveMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyvssadminlistshadows/for=[volume]:MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyMicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyShadowcopiescanbeexposedthroughsymboliclinks.
Mklink/dC:\{test-shadow}\\\GLOBALROOT\Device\HarddiskVolumeShadowCopy3\MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyVolumeShadowscanbemounteddirectlyasnetworkshares.
netsharetestshadow=\\.
\HarddiskVolumeShadowCopy11\MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopy>psexec\\[computername]vssadminlistshadows/for=C:>psexec\\[computername]netsharetestshadow=\\.
\HarddiskVolumeShadowCopy20\PsExecv1.
94-Executeprocessesremotely.
.
.
testshadowwassharedsuccessfully.
netexitedon[computername]witherrorcode0.
>robocopy/S/R:1/W:1/LOG:D:\VSStestcopylog.
txt\\[computername]\testshadowD:\vssTestLogFile:D:\VSStestcopylog.
txt.
.
.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyOtherwaystocallshadowcopies:–\\localhost\C$\Users\troyla\Downloads(Yesterday,July20,2009,12:00AM)–\\localhost\C$\@GMT-2009.
07.
17-08.
45.
26\–MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyC:\Users\Troyla\Desktop\fau-1.
3.
0.
2390a\fau\FAU.
x64>ddif=\\.
\HarddiskVolumeShadowCopy11of=E:\shadow11.
dd–localwrtTheVistaFirewallFirewallisactivewithexceptions.
Copying\\.
\HarddiskVolumeShadowCopy11toE:\shadow11.
ddOutput:E:\shadow11.
dd136256155648bytes129943+1recordsin129943+1recordsout136256155648byteswrittenSucceeded!
C:\Users\Troyla\Desktop\fau-1.
3.
0.
2390a\fau\FAU.
x64>Shadowcopiescanbeimaged.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyImagesofshadowcopiescanbeopenedinforensicstoolsandappearaslogicalvolumes.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyDatathathasbeendeletedcanbecapturedbyshadowcopiesandavailableforretrievalinshadowcopyimages.
MicrosoftNetworkSecurityOSArtifacts—VolumeShadowCopyEveryshadowcopydatasetshouldapproximatethesizeoftheoriginalvolume.
Amountofcasedata=(numberofshadowcopies)x(sizeofthevolume)+(sizeofthevolume).
10shadowcopies=692GBMicrosoftNetworkSecurityApplications—I.
E.
8FileSystemsNTFS,FAT32,EXFATFvevol.
sysMount,Partition&VolumeManagersApplications—e.
g.
,I.
E.
,etc.
OSArtifacts"Disk"MicrosoftNetworkSecurityApplications—I.
E.
8"C:\ProgramFiles(x86)\InternetExplorer\iexplore.
exe"-privateMicrosoftNetworkSecurityApplications—I.
E.
8Cachedataappearstobewritten,thendeleted.
MicrosoftNetworkSecurityApplications—I.
E.
8ResidualcachefilesfromInPrivatebrowsing.
MicrosoftNetworkSecurityApplications—I.
E.
8Tabandsessionrecovery—anewsourceforhistoricalbrowsinginformation.
\User\[Account]\AppData\Local\Microsoft\InternetExplorer\RecoveryMicrosoftNetworkSecurityApplications—I.
E.
8Recoveryfile:NotetheStructuredStoragefileformat.
MicrosoftNetworkSecurityApplications—I.
E.
8MicrosoftNetworkSecurity2009MicrosoftCorporation.
Allrightsreserved.
Microsoft,Windows,WindowsVistaandotherproductnamesareormayberegisteredtrademarksand/ortrademarksintheU.
S.
and/orothercountries.
TheinformationhereinisforinformationalpurposesonlyandrepresentsthecurrentviewofMicrosoftCorporationasofthedateofthispresentation.
BecauseMicrosoftmustrespondtochangingmarketconditions,itshouldnotbeinterpretedtobeacommitmentonthepartofMicrosoft,andMicrosoftcannotguaranteetheaccuracyofanyinformationprovidedafterthedateofthispresentation.
MICROSOFTMAKESNOWARRANTIES,EXPRESS,IMPLIEDORSTATUTORY,ASTOTHEINFORMATIONINTHISPRESENTATION.
DogYun(300元/月),韩国独立服务器,E5/SSD+NVMe
DogYun(中文名称狗云)新上了一批韩国自动化上架独立服务器,使用月减200元优惠码后仅需每月300元,双E5 CPU,SSD+NVMe高性能硬盘,支持安装Linux或者Windows操作系统,下单自动化上架。这是一家成立于2019年的国人主机商,提供VPS和独立服务器租用等产品,数据中心包括中国香港、美国洛杉矶、日本、韩国、德国、荷兰等。下面分享这款自动化上架韩国独立服务器的配置和优惠码信息。...
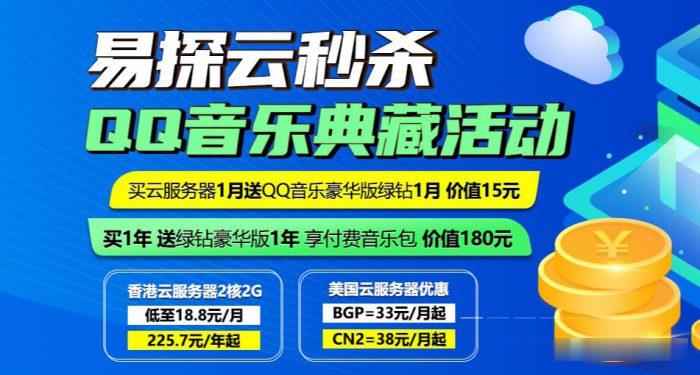
哪里购买香港云服务器便宜?易探云2核2G低至18元/月起;BGP线路年付低至6.8折
哪里购买香港云服务器便宜?众所周知,国内购买云服务器大多数用户会选择阿里云或腾讯云,但是阿里云香港云服务器不仅平时没有优惠,就连双十一、618、开年采购节这些活动也很少给出优惠。那么,腾讯云虽然海外云有优惠活动,但仅限新用户,购买过腾讯云服务器的用户就不会有优惠了。那么,我们如果想买香港云服务器,怎么样购买香港云服务器便宜和优惠呢?下面,云服务器网(yuntue.com)小编就介绍一下!我们都知道...
Megalayer(159元 )年付CN2优化带宽VPS
Megalayer 商家我们还算是比较熟悉的,商家主要业务方向是CN2优化带宽、国际BGP和全向带宽的独立服务器和站群服务器,且后来也有增加云服务器(VPS主机)业务。这次中秋节促销活动期间,有发布促销活动,这次活动力度认为还是比较大的,有提供香港、美国、菲律宾的年付VPS主机,CN2优化方案线路的低至年付159元。这次活动截止到10月30日,如果我们有需要的话可以选择。第一、特价限量年付VPS主...
win7配置为你推荐
-
巨星prince去世Whitney Houston因什么去世的?www.7160.com电影网站有那些陈嘉垣陈浩民、马德钟强吻女星陈嘉桓,求大家一个说法。杰景新特杰德特这个英雄怎么样www.kk4kk.com猪猪影院www.mlzz.com 最新电影收费吗?www.7788k.comwww.6601txq.com.有没有这个网站www.bbb551.comHUNTA551第一个第二个妹子是谁呀??99nets.com99nets网游模拟娱乐社区怎么打不开了?????????谁能告诉我 ???、bbs2.99nets.com西安论坛、西安茶馆网、西安社区、西安bbs 的网址是多少?www.147.qqq.comWWW147EEE.COM这个网站现在改哪个网址了