authenticatedapnic
apnic 时间:2021-01-10 阅读:()
IssueDate:Revision:CryptographyApplications:VPNandIPsec30May20152.
0-draftOverviewIntroductiontoVPNIPsecFundamentalsTunnelandTransportModeIPsecArchitectureandComponentsofIPsecInternetKeyExchangeConfiguringIPsecforIPv4andIPv62VirtualPrivateNetworkCreatesasecuretunneloverapublicnetwork–Clienttofirewall–Routertorouter–FirewalltofirewallUsestheInternetasthepublicbackbonetoaccessasecureprivatenetwork–RemoteemployeescanaccesstheirofficenetworkTwotypes:–Remoteaccess–Site-to-siteVPN3VPNImplementationHardware–UsuallyaVPN-typerouter–Pros:highestnetworkthroughput,plugandplay,dualpurpose–Cons:costandlackofflexibilitySoftware–Idealfortwoend-pointsindifferentorganisations–Pros:flexible,andlowrelativecost–Cons:lackofefficiency,morelabortrainingrequired,lowerproductivity;higherlaborcostsFirewall–Pros:costeffective,tri-purpose,hardenstheoperatingsystem–Cons:stillrelativelycostly4VPNProtocolsPPTP(Point-to-PointtunnelingProtocol)–DevelopedbyMicrosofttosecuredial-upconnections–Operatesinthedata-linklayerL2F(Layer2ForwardingProtocol)–DevelopedbyCisco–SimilarasPPTPL2TP(Layer2TunnelingProtocol)–IETFstandard–CombinesthefunctionalityofPPTPandL2FIPsec(InternetProtocolSecurity)–OpenstandardforVPNimplementation–Operatesonthenetworklayer5OtherModernVPNsMPLSVPN–Usedforlargeandsmallenterprises–Pseudowire,VPLS,VPRNGRETunnel–PacketencapsulationprotocoldevelopedbyCisco–Notencrypted–ImplementedwithIPsecL2TPIPsec–UsesL2TPprotocol–UsuallyimplementedalongwithIPsec–IPsecprovidesthesecurechannel,whileL2TPprovidesthetunnel6AdvantagesofVPNCheaperconnection–UsetheInternetconnectioninsteadofaprivateleaselineScalability–Flexibilityofgrowth–EfficiencywithbroadbandtechnologyAvailability–AvailableeverywherethereisanInternetconnection7DisadvantagesofVPNVPNsrequireanin-depthunderstandingofpublicnetworksecurityissuesandproperdeploymentprecautionsAvailabilityandperformancedependsonfactorslargelyoutsideoftheircontrolVPNsneedtoaccommodateprotocolsotherthanIPandexistinginternalnetworktechnology8IPsecProvidesLayer3security(RFC2401)–Transparenttoapplications(noneedforintegratedIPsecsupport)AsetofprotocolsandalgorithmsusedtosecureIPdataatthenetworklayerCombinesdifferentcomponents:–Securityassociations(SA)–Authenticationheaders(AH)–Encapsulatingsecuritypayload(ESP)–InternetKeyExchange(IKE)AsecuritycontextfortheVPNtunnelisestablishedviatheISAKMP9IPSecInternetWhatisIPSecIETFstandardthatenablesencryptedcommunicationbetweenpeers:–Consistsofopenstandardsforsecuringprivatecommunications–Networklayerencryptionensuringdataconfidentiality,integrity,andauthentication–Scalesfromsmalltoverylargenetworks10IPsecStandardsRFC4301"TheIPSecurityArchitecture"–DefinestheoriginalIPsecarchitectureandelementscommontobothAHandESPRFC4302–Definesauthenticationheaders(AH)RFC4303–DefinestheEncapsulatingSecurityPayload(ESP)RFC2408–ISAKMPRFC5996–IKEv2(Sept2010)RFC4835–CryptographicalgorithmimplementationforESPandAH11BenefitsofIPsecConfidentiality–ByencryptingdataIntegrity–RoutersateachendofatunnelcalculatesthechecksumorhashvalueofthedataAuthentication–Signaturesandcertificates–AllthesewhilestillmaintainingtheabilitytoroutethroughexistingIPnetworks"IPsecisdesignedtoprovideinteroperable,highquality,cryptographically-basedsecurityforIPv4andIPv6"-(RFC2401)12BenefitsofIPsecDataintegrityandsourceauthentication–Data"signed"bysenderand"signature"isverifiedbytherecipient–Modificationofdatacanbedetectedbysignature"verification"–Because"signature"isbasedonasharedsecret,itgivessourceauthenticationAnti-replayprotection–Optional;thesendermustprovideitbuttherecipientmayignoreKeymanagement–IKE–sessionnegotiationandestablishment–Sessionsarerekeyedordeletedautomatically–Secretkeysaresecurelyestablishedandauthenticated–Remotepeerisauthenticatedthroughvaryingoptions13DifferentLayersofEncryptionNetworkLayer-IPsecLinkLayerEncryptionApplicationLayer–SSL,PGP,SSH,HTTPS14IPsecModesTunnelMode–EntireIPpacketisencryptedandbecomesthedatacomponentofanew(andlarger)IPpacket.
–FrequentlyusedinanIPsecsite-to-siteVPNTransportMode–IPsecheaderisinsertedintotheIPpacket–Nonewpacketiscreated–Workswellinnetworkswhereincreasingapacket'ssizecouldcauseanissue–Frequentlyusedforremote-accessVPNs15Tunnelvs.
TransportModeIPsecPayloadTCPHeaderIPHeaderWithoutIPsecTransportModeIPsecTunnelModeIPsecPayloadTCPHeaderIPHeaderIPsecHeaderIPHeaderPayloadTCPHeaderIPHeaderIPsecHeaderNewIPHeader16TransportvsTunnelMode17TransportMode:EndsystemsaretheinitiatorandrecipientofprotectedtrafficTunnelMode:GatewaysactonbehalfofhoststoprotecttrafficRoutingUpdateTFTPFileTransferFileTransferIPsecArchitectureESPAHIKEIPsecSecurityPolicyEncapsulatingSecurityPayloadAuthenticationHeaderTheInternetKeyExchange18SecurityAssociations(SA)AcollectionofparametersrequiredtoestablishasecuresessionUniquelyidentifiedbythreeparametersconsistingof–SecurityParameterIndex(SPI)–IPdestinationaddress–Securityprotocol(AHorESP)identifierAnSAiseitheruni-orbidirectional–IKESAsarebidirectional–IPsecSAsareunidirectionalTwoSAsrequiredforabidirectionalcommunicationAsingleSAcanbeusedforAHorESP,butnotboth–mustcreatetwo(ormore)SAsforeachdirectionifusingbothAHandESP19SecurityParameterIndex(SPI)Aunique32-bitidentificationnumberthatispartoftheSecurityAssociation(SA)ItenablesthereceivingsystemtoselecttheSAunderwhichareceivedpacketwillbeprocessed.
Hasonlylocalsignificance,definedbythecreatoroftheSA.
CarriedintheESPorAHheaderWhenanESP/AHpacketisreceived,theSPIisusedtolookupallofthecryptoparameters20HowtoSetUpSAManually–Sometimesreferredtoas"manualkeying"–Youconfigureoneachnode:Participatingnodes(I.
e.
trafficselectors)AHand/orESP[tunnelortransport]CryptographicalgorithmandkeyAutomatically–UsingIKE(InternetKeyExchange)21ISAKMPInternetSecurityAssociationandKeyManagementProtocolUsedforestablishingSecurityAssociations(SA)andcryptographickeysOnlyprovidestheframeworkforauthenticationandkeyexchange,butkeyexchangeisindependentKeyexchangeprotocols–InternetKeyExchange(IKE)–KerberizedInternetNegotiationofKeys(KINK)22AuthenticationHeader(AH)Providessourceauthenticationanddataintegrity–ProtectionagainstsourcespoofingandreplayattacksAuthenticationisappliedtotheentirepacket,withthemutablefieldsintheIPheaderzeroedoutIfbothAHandESPareappliedtoapacket,AHfollowsESPOperatesontopofIPusingprotocol51InIPv4,AHprotectsthepayloadandallheaderfieldsexceptmutablefieldsandIPoptions(suchasIPsecoption)23AHHeaderFormatNextHeader(8bits):indicateswhichupperlayerprotocolisprotected(UDP,TCP,ESP)PayloadLength(8bits):sizeofAHin32-bitlongwords,minus2Reserved(16bits):forfutureuse;mustbesettoallzeroesfornowSPI(32bits):arbitrary32-bitnumberthatspecifiestothereceivingdevicewhichsecurityassociationisbeingused(securityprotocols,algorithms,keys,times,addresses,etc)SequenceNumber(32bits):startat1andmustneverrepeat.
ItisalwayssetbutreceivermaychoosetoignorethisfieldAuthenticationData:ICVisadigitalsignatureoverthepacketanditvariesinlengthdependingonthealgorithmused(SHA-1,MD5)012345678910111213141516171819202122232425262728293031NextHeaderPayloadLengthReservedSecurityParameterIndex(SPI)SequenceNumberAuthenticationData[IntegrityCheckValue(ICV)]24EncapsulatingSecurityPayload(ESP)UsesIPprotocol50ProvidesallthatisofferedbyAH,plusdataconfidentiality–usessymmetrickeyencryptionMustencryptand/orauthenticateineachpacket–EncryptionoccursbeforeauthenticationAuthenticationisappliedtodataintheIPsecheaderaswellasthedatacontainedaspayload25ESPHeaderFormatSPI:arbitrary32-bitnumberthatspecifiesSAtothereceivingdeviceSeq#:startat1andmustneverrepeat;receivermaychoosetoignoreIV:usedtoinitializeCBCmodeofanencryptionalgorithmPayloadData:encryptedIPheader,TCPorUDPheaderanddataPadding:usedforencryptionalgorithmswhichoperateinCBCmodePaddingLength:numberofbytesaddedtothedatastream(maybe0)NextHeader:thetypeofprotocolfromtheoriginalheaderwhichappearsintheencryptedpartofthepacketAuthenticationHeader:ICVisadigitalsignatureoverthepacketanditvariesinlengthdependingonthealgorithmused(SHA-1,MD5)012345678910111213141516171819202122232425262728293031NextHeaderPaddingLengthPayloadData(Variable)Padding(0-255bytes)InitializationVector(IV)SequenceNumberSecurityParameterIndex(SPI)AuthenticationData(ICV)ENCRYPTED26PacketFormatAlterationforAHTransportModeOriginalIPHeaderTCP/UDPDataOriginalIPHeaderAHHeaderTCP/UDPDataAuthenticationHeaderWithoutAHWithAHAuthenticatedexceptformutablefieldsinIPheader(ToS,TTL,HeaderChecksum,Offset,Flags)27PacketFormatAlterationforESPTransportModeOriginalIPHeaderTCP/UDPDataOriginalIPHeaderESPHeaderEncapsulatingSecurityPayloadBeforeapplyingESP:AfterapplyingESP:EncryptedESPAuthenticationAuthenticatedTCP/UDPDataESPTrailer28PacketFormatAlterationforAHTunnelModeOriginalIPHeaderTCP/UDPDataNewIPHeaderAHHeaderDataAuthenticationHeaderBeforeapplyingAH:AfterapplyingAH:AuthenticatedexceptformutablefieldsinnewIPheaderOriginalIPHeader(ToS,TTL,HeaderChecksum,Offset,Flags)29PacketFormatAlterationforESPTunnelModeOriginalIPHeaderTCP/UDPDataNewIPHeaderESPHeaderEncapsulatingSecurityPayloadBeforeapplyingESP:AfterapplyingESP:EncryptedESPAuthenticationAuthenticatedOriginalIPHeaderTCP/UDPDataESPTrailer30InternetKeyExchange(IKE)"AnIPseccomponentusedforperformingmutualauthenticationandestablishingandmaintainingSecurityAssociations.
"(RFC5996)TypicallyusedforestablishingIPsecsessionsAkeyexchangemechanismFivevariationsofanIKEnegotiation:–Twomodes(aggressiveandmainmodes)–Threeauthenticationmethods(pre-shared,publickeyencryption,andpublickeysignature)UsesUDPport50031IKEModesModeDescriptionMainmodeThreeexchangesofinformationbetweenIPsecpeers.
Initiatorsendsoneormoreproposalstotheotherpeer(responder)ResponderselectsaproposalAggressiveModeAchievessameresultasmainmodeusingonly3packetsFirstpacketsentbyinitiatorcontainingallinfotoestablishSASecondpacketbyresponderwithallsecurityparametersselectedThirdpacketfinalizesauthenticationoftheISAKMPsessionQuickModeNegotiatestheparametersfortheIPsecsession.
EntirenegotiationoccurswithintheprotectionofISAKMPsession32InternetKeyExchange(IKE)PhaseI–Establishasecurechannel(ISAKMPSA)–Usingeithermainmodeoraggressivemode–Authenticatecomputeridentityusingcertificatesorpre-sharedsecretPhaseII–Establishesasecurechannelbetweencomputersintendedforthetransmissionofdata(IPsecSA)–Usingquickmode33OverviewofIKETrafficwhichneedstobeprotectedIPsecPeerIPsecPeerIKEPhase1SecurecommunicationchannelIKEPhase2IPsecTunnelSecuredtrafficexchange123434ISAKMPHeaderFormat012345678910111213141516171819202122232425262728293031InitiatorCookieTotalLengthofMessageFlagsResponderCookieNextPayloadExchangeTypeMessageIDMajorVersionMinorVersion35ISAKMPMessageFormat012345678910111213141516171819202122232425262728293031NextPayload:1byte;identifierfornextpayloadinmessage.
IfitisthelastpayloadItwillbesetto0Reserved:1byte;setto0PayloadLength:2bytes;lengthofpayload(inbytes)includingtheheaderPayload:TheactualpayloaddataNextPayloadReservedPayloadLengthPayloadNextPayloadReservedPayloadLengthPayloadISAKMPHEADER36IKEPhase1(MainMode)MainmodenegotiatesanISAKMPSAwhichwillbeusedtocreateIPsecSAsThreesteps–SAnegotiation(encryptionalgorithm,hashalgorithm,authenticationmethod,whichDFgrouptouse)–DoaDiffie-Hellmanexchange–Provideauthenticationinformation–Authenticatethepeer37IKEPhase1(MainMode)ResponderInitiator12IKEMessage1(SAproposal)IKEMessage2(acceptedSA)IKEMessage3(DHpublicvalue,nonce)IKEMessage4(DHpublicvalue,nonce)IKEMessage5(Authenticationmaterial,ID)IKEMessage6(Authenticationmaterial,ID)43NegotiateIKEPolicyAuthenticatedDHExchangeComputeDHsharedsecretandderivekeyingmaterialProtectIKEPeerIdentityInternet(Encrypted)38IKEPhase1(AggressiveMode)Uses3(vs6)messagestoestablishIKESANodenialofserviceprotectionDoesnothaveidentityprotectionOptionalexchangeandnotwidelyimplemented39IKEPhase2(QuickMode)AlltrafficisencryptedusingtheISAKMPSecurityAssociationEachquickmodenegotiationresultsintwoIPsecSecurityAssociations(oneinbound,oneoutbound)Creates/refresheskeys40IKEPhase2(QuickMode)ResponderInitiator3ComputekeyingmaterialInternetMessage1(authentication/keyingmaterialandSAproposal)Message2(authentication/keyingmaterialandacceptedSA)Message3(hashforproofofintegrity/authentication)125Validatemessage1746Validatemessage3Validatemessage241IKEv2:ReplacementforCurrentIKESpecificationFeaturePreservation–MostfeaturesandcharacteristicsofbaselineIKEv1protocolarebeingpreservedinv2CompilationofFeaturesandExtensions–QuiteafewfeaturesthatwereaddedontopofthebaselineIKEprotocolfunctionalityinv1arebeingreconciledintothemainlinev2frameworkSomeNewFeatures42IKEv2:WhatIsNotChangingFeaturesinv1thathavebeendebatedbutareultimatelybeingpreservedinv2–Mostpayloadsreused–Useofnoncestoensureuniquenessofkeysv1extensionsandenhancementsbeingmergedintomainlinev2specification–Useofa'configurationpayload'similartoMODECFGforaddressassignment–'X-auth'typefunctionalityretainedthroughEAP–UseofNATDiscoveryandNATTraversaltechniques43IKEv2:WhatIsChangingSignificantChangesBeingtotheBaselineFunctionalityofIKE–EAPadoptedasthemethodtoprovidelegacyauthenticationintegrationwithIKE–Publicsignaturekeysandpre-sharedkeys,theonlymethodsofIKEauthentication–Useof'statelesscookie'toavoidcertaintypesofDOSattacksonIKE–Continuousphaseofnegotiation44HowDoesIKEv2WorkIKE_SA_INIT(TwoMessages)IKE_AUTH(TwoMessages)ProtectedDataIKE_SAAuthenticationParametersNegotiatedIKEAuthenticationOccursandOneCHILD_SACreatedCREATE_CHILD_SA(TwoMessages)SecondCHILD_SACreated45ConsiderationsForUsingIPsecSecurityServices–Dataoriginauthentication–Dataintegrity–Replayprotection–ConfidentialitySizeofnetworkHowtrustedareendhosts–canaprioricommunicationpoliciesbecreatedVendorsupportWhatothermechanismscanaccomplishsimilarattackriskmitigation46Non-VendorSpecificDeploymentIssuesHistoricalPerception–Configurationnightmare–NotinteroperablePerformancePerception–Needempiricaldata–WhereistherealperformancehitStandardsNeedCohesion47VendorSpecificDeploymentIssuesLackofinteroperabledefaults–AdefaultdoesNOTmandateaspecificsecuritypolicy–DefaultscanbemodifiedbyendusersConfigurationcomplexity–Toomanyknobs–Vendor-specificterminologyGoodNews:IPv6supportinmostcurrentimplementations48IPsecConcernsAreenoughpeopleawarethatIKEv2isnotbackwardscompatiblewithIKEv1–IKEv1isusedinmostIPsecimplementations–WillIKEv2implementationsfirsttryIKEv2andthenreverttoIKEv1IsIPsecimplementedforIPv6–SomeimplementationsshipIPv6capabledeviceswithoutIPseccapabilityandhostrequirementsischangedfromMUSTtoSHOULDimplementOSPFv3–Allvendors'IF'theyimplementIPsecusedAH–LateststandardtodescribehowtouseIPsecsaysMUSTuseESPw/NullencryptionandMAYuseAH49IPsecConcerns(cont)Whatistransportmodeinteroperabilitystatus–WillenduserauthenticationbeinteroperablePKIIssues–Whichcertificatesdoyoutrust–HowdoesIKEv1and/orIKEv2handleproposalswithcertificates–Shouldcommontrustedrootsbeshippedbydefault–Whoisfollowingandimplementingpki4ipsec-ikecert-profile(rfc4945)Havemobilityscenariosbeentested–MobilitystandardsrelyheavilyonIKEv2ESP–howdetermineifESP-NullvsEncrypted50IPsecBestPracticesUseIPsectoprovideintegrityinadditiontoencryption–UseESPoptionUsestrongencryptionalgorithms–AESinsteadofDESUseagoodhashingalgorithm–SHAinsteadofMD5ReducethelifetimeoftheSecurityAssociation(SA)byenablingPerfectForwardSecrecy(PFS)–Increasesprocessorburdensodothisonlyifdataishighlysensitive51ConfiguringIPsecStep1:ConfiguretheIKEPhase1Policy(ISAKMPPolicy)cryptoisakmppolicy[priority]Step2:SettheISAKMPIdentitycryptoisakmpidentity{ipaddress|hostname}Step3:ConfiguretheIPsectransfersetcryptoipsectransform-settransform-set-namemode[tunnel|transport]cryptoipsecsecurity-associationlifetimesecondsseconds52ConfiguringIPsecStep5:Creatingmapwithnamecryptomapcrypto-map-nameseq-numipsec-isakmpmatchaddressaccess-list-idsetpeer[ipaddress|hostname]settransform-settransform-set-namesetsecurity-associationlifetimesecondssecondssetpfs[group1|group2]Step6:ApplytheIPsecPolicytoanInterfacecryptomapcrypto-map-namelocal-addressinterface-id53IPsecLayoutR1R2EncryptedsessionPublicNetwork54RouterConfigurationcryptoisakmppolicy1authenticationpre-shareencryptionaeshashshagroup5cryptoisakmpkeyTraining123address172.
16.
11.
66!
cryptoipsectransform-setESP-AES-SHAesp-aesesp-sha-hmac!
cryptomapLAB-VPN10ipsec-isakmpmatchaddress101settransform-setESP-AES-SHAsetpeer172.
16.
11.
66Phase1SAEncryptionandauthenticationPhase2SA55RouterConfigurationintfa0/1cryptomapLAB-VPNExit!
access-list101permitip172.
16.
16.
00.
0.
0.
255172.
16.
20.
00.
0.
0.
255ApplytoanoutboundinterfaceDefineinterestingVPNtraffic56IPsecDebugCommandsshcryptoipsecsashcryptoisakmppeersshcryptoisakmpsashcryptomap57Capture:Telnet58Capture:Telnet+IPsec59PrettyGoodIPsecPolicyIKEPhase1(akaISAKMPSAorIKESAorMainMode)–3DES(AES-192ifbothendssupportit)–Lifetime(8hours=480min=28800sec)–SHA-2(256bitkeys)–DHGroup14(akaMODP#14)IKEPhase2(akaIPsecSAorQuickMode)–3DES(AES-192ifbothendssupportit)–Lifetime(1hour=60min=3600sec)–SHA-2(256bitkeys)–PFS2–DHGroup14(akaMODP#14)6061THANKYOUwww.
facebook.
com/APNICwww.
twitter.
com/apnicwww.
youtube.
com/apnicmultimediawww.
flickr.
com/apnicwww.
weibo.
com/APNICrir62
- authenticatedapnic相关文档
- Singleapnic
- "IPv4AddressAllocationsbyCountry"
- Miseapnic
- 中国apnic
- singleapnic
- probeapnic
VoLLcloud6折限量,香港CMI云服务器三网直连-200M带宽
vollcloud LLC首次推出6折促销,本次促销福利主要感恩与回馈广大用户对于我们的信任与支持,我们将继续稳步前行,为广大用户们提供更好的产品和服务,另外,本次促销码共限制使用30个,个人不限购,用完活动结束,同时所有vps产品支持3日内无条件退款和提供免费试用。需要了解更多产品可前往官网查看!vollcloud优惠码:VoLLcloud终生6折促销码:Y5C0V7R0YW商品名称CPU内存S...
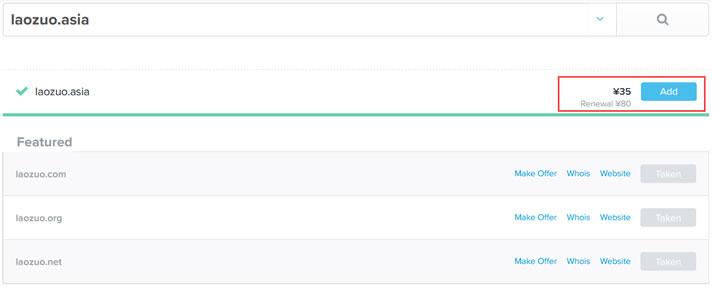
.asia域名是否适合做个人网站及.asia域名注册和续费成本
今天看到群里的老秦同学在布局自己的网站项目,这个同学还是比较奇怪的,他就喜欢用这些奇怪的域名。比如前几天看到有用.in域名,个人网站他用的.me域名不奇怪,这个还是常见的。今天看到他在做的一个范文网站的域名,居然用的是 .asia 后缀。问到其理由,是有不错好记的前缀。这里简单的搜索到.ASIA域名的新注册价格是有促销的,大约35元首年左右,续费大约是80元左右,这个成本算的话,比COM域名还贵。...
PIGYUN:美国联通CUVIPCUVIP限时cuvip、AS9929、GIA/韩国CN2机房限时六折
pigyun怎么样?PIGYunData成立于2019年,2021是PIGYun为用户提供稳定服务的第三年,目前商家提供香港CN2线路、韩国cn2线路、美西CUVIP-9929、GIA等线路优质VPS,基于KVM虚拟架构,商家采用魔方云平台,所有的配置都可以弹性选择,目前商家推出了七月优惠,韩国和美国所有线路都有相应的促销,六折至八折,性价比不错。点击进入:PIGYun官方网站地址PIGYUN优惠...
apnic为你推荐
-
免费美国主机哪里有免费不限流量的国外主机租服务器租服务器是什么意思?asp主机空间Asp空间是什么空间啊?跟有的网站提供的免费空间有什么区别吗?域名服务什么叫主域名服务器?空间域名空间和域名是什么?香港虚拟空间香港虚拟空间 好不、现在还有人买嘛虚拟空间免费试用哪有免费试用的虚拟主机?1g虚拟主机1G虚拟空间大约多少钱?上海虚拟主机谁能告诉我杭州哪个公司的虚拟主机最好,机房最好是上海或浙江的.apache虚拟主机apache里面可以在虚拟主机里边设置虚拟目录吗?急,在线等!