solutionssb
www.nyzsb.com.cn 时间:2021-02-14 阅读:()
Anti-PhishingSecurityStrategyAngeloP.
E.
RosielloAgenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsNatureofPhishing3.
8daysAveragetimeonlineforsiteU.
S.
Countryhostingthemostphishingwebsites149Numberofbrandshijackedbyphishingcampaigns37438Numberofuniquesites23415NumberofuniquereportsFinancialServicescontinuetobethemosttargetedindustrysectorat96.
9%ofallattacksinthemonthofMay-ListofthemainhighlightsreportedforMay2007-StatisticsfromtheAntiPhishingWorkingGroup(AWPG)confirmtheglobalnatureofphishingwhoseprimarytargetarefinancialinstitutionsGrowingEffectivenessandEfficiencyofPhishingOverthelastmonthsphishingattackshavebecomemoreeffectiveandcomplextotrackandchallengeUSChina-Thetop5listofbreaches-InformationWeekResearch&Accenture–InformationSecuritySurvey2007Phishingrepresentsthethirdtypeofsuccessfulattackagainstenterprises(mainlybanks)SymantechasdetectedanumberofphishingsitesthathavebeenhostedongovernmentURLsoverrecentmonths.
InJunealone(2007),fraudulentsiteswereidentifiedonsitesrunbythegovernmentsofThailand,Indonesia,Hungary,Bangladesh,Argentina,SriLanka,theUkraine,China,Brazil,BosniaandHerzegovina,Colombia,andMalaysia.
"HostingaphishingWebpageonagovernmentsitehasanumberofadvantagesforaphisher.
GovernmentWebsitesoftenreceiveahighvolumeoftraffic,sotheirserverscanhandletheextratrafficgeneratedbyaphishingsite"writesSymantecresearcherNickSullivan.
"Thisextratrafficmightnotbenoticedimmediately,givingthephishingsitealongerlifespanbeforeitisdetectedandshutdown.
Perhapsmostimportantly,hostingaphishingsiteonanactualgovernmentURLgivesthephishingsiteasenseofauthenticitythat'shardtobeat.
"-ImprovingPhishingqualityattacks-TaxonomyofPhishingAttacksPhishingattackscanbeclassifiedaccordingtotheirnatureEmail,IMPhishingAttacksE-mailIM,IRC,etc.
-Description-Spoofede-mailaresenttoasetofvictimsaskingthem(usually)toupgradetheirpasswords,dataaccount,etc.
MSN,ICQ,AOLandotherIMchannelsareusedtoreachthevictims.
Socialengineeringtechniquesareusedtogainvictim'ssensitiveinformationCallingthevictimsonthephone,classicsocialengineeringtechniquesareusedbyphishersAnotherkindofattackisbasedontheinternetbrowservulnerabilities.
ThisapproachisusuallyadoptedtoautomaticallyinstalldialersPhone,mail,etc.
Exploitbased-ClassificationoftheAttacks-AProcessofPhishingAttacksInatypicalattack,thephishersendsalargenumberofspoofed(i.
e.
fake)e-mailstorandomInternetusersthatseemtobecomingfromalegitimateandwell-knownbusinessorganization(e.
g.
financialinstitutions,creditcardcompanies,etc)Thee-mailurgesthevictimtoupdatehispersonalinformationasaconditiontoavoidloosingaccessrightstospecificservices(e.
g.
accesstoonlinebankaccount,etc).
Byclickingonthelinkprovided,thevictimisdirectedtoaboguswebsiteimplementedbytheattackerThephishingwebsiteisstructuredasacloneoftheoriginalwebsitesothatthevictimisnotabletodistinguishitfromthatoftheservicehe/shehasaccessto.
Lotsofe-mailsaresenttoasetofrandomvictimsThevictimchangesherdataE-mailurgesthevictimtoupdateherdataviaweb(aspoofedone)Phisher!
!
!
AFRUDNewPhishersSkillsToconfusethevictim,phishersaredevisingnewtricksPhishinge-mailembedhyperlinksfromtheoriginalwebsitesothattheusersmainlysurfontherealwebserverexecutingonlyasmallnumberofconnectionstothefakewebserver.
WebsiteURLareencodedorobfuscatedtonotraisesuspicious.
IDNspoofing,forexample,usesUnicodeURLsthatrenderURLsinbrowsersinawaythattheaddresslooksliketheoriginalwebsiteaddressbutactuallylinktoafakewebsitewithadifferentaddress.
VictimsareredirectedtoaphishingwebsitebyfirstusingmalwarestoinstallamaliciousBrowserHelperObject(BHO).
BHOsareDLLsthatallowsdeveloperstocustomizeandcontrolInternetExplorerbutalsophisherstocompromiseconnections.
Thehostsfileonthevictim'smachineiscorrupted,forexampleusingamalware.
ThehostfilesmaintainslocalmappingsbetweenDNSnamesandIPaddresses.
ByinsertingafakeDNSentryintotheuser'shostsfile,itwillappearthattheirwebbrowserisconnectingtoalegitimatewebsitewheninfactitisconnectingtoaphishingwebsite.
Agenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsStrategicDefenseTechniquesAntiphisingdefensescanbeserverandclientbasedsolutionsServer-basedAnti-PhishingClient-basedBehaviourDetectionBrandMonitoringSecurityEventsE-mailAnalysisBlackListsInformationFlowSimilarityofLayoutsFocusofthispresentation!
Server-basedSolutionsServerbasedtechniquesareimplementedbyserviceproviders(e.
g.
ISP,e-commercestores,financialinstitutions,etc…)Crawlingon-linewebsitestoidentify"clones"(lookingforlegitimatebrands),whichareconsideredphishingpages.
Suspectedwebsitesareaddedtoacentralized"black-list".
Foreachcustomeraprofileisidentified(afteratrainingperiod)whichisusedtodetectanomaliesinthebehaviourofusersSecurityeventanalysisandcorrelationusingregisteredeventsprovidedbyseveralsources(OS,application,networkdevice)toidentifyanomalousactivityorforpostmortemanalysisfollowinganattackorafraudUsingmorethanoneidentificationfactoriscalledstrongauthentication.
Therearethreeuniversallyrecognizedfactorsforauthenticatingindividuals:somethingyouknow(e.
g.
password);somethingyouhave(e.
g.
hwsecuritytoken);somethingyouare(e.
g.
fingerprint)Newtechniquesofauthenticationareunderreasearch,suchasusinganimageduringtheregistrationphasewhichisshownduringeveryloginprocessBrandMonitoringBehaviourDetectionSecurityEventMonitoringStrongAuthenticationNewAuthenticationTechniquesClient-basedSolutionsClient-basedtechniquesareimplementedonusers'endpointthroughbrowserplug-insore-mailclientsE-mail-basedapproachestypicallyusefiltersandcontentanalysis.
IftrainedregularlyBayesianfiltersareactuallyquiteeffectiveininterceptingbothspammingandphishinge-mails.
BlacklistsarecollectionsofURLsidentifiedasmalicious.
Theblacklistisqueriedbythebrowserrun-timewheneverapageisloaded.
IfthecurrentlyvisitedURLisincludedintheblacklist,theuserisadvisedofthedanger,otherwisethepageisconsideredlegitimate.
InformationflowsolutionsarebasedonthepremisethatwhileausermaybeeasilyfooledbyURLobfuscationorafakedomainname,aprogramwillnot.
AntiPhishisanexampleofthistypeofdefensetechniquewhichkeepstrackofthesensitiveinformationthattheuserentersintowebforms,raisinganalertifsomethingisconsideredunsafeMostadvancedtechniquestrytodistinguishaphishingwebpagefromthelegitimateonecomparingtheirvisualsimilarity[[Wenyin,Huang,Xiaoyue,Min,Deng],[Rosiello,Kirda,Kruegel,Ferrandi]E-mailAnalysisBlack-ListsInformationFlowSimilarityofLayoutsTrendsonclient-basedMarketSolutionsInOctober2006,aMicrosoft-commissionedreportonvariousanti-phishingsolutionswasreleased.
ThetestersfoundthatMicrosoftInternetExplorer(IE)7.
0hasbetteranti-phishingtechnologythancompetingsolutions.
TheproductstestedincludedIE7.
0Beta3,EarthLinkScamBlocker,eBayToolbarwithAccountGuard,GeoTrustTrustWatch,GoogleToolbarforFirefoxwithSafeBrowsing,McAfeeSiteAdvisorPlus,NetcraftToolbar,andNetscapeBrowserwithbuilt-inantiphishingtechnologyTheMozillaFoundationcommissioneditsownstudytogaugetheeffectivenessofMozillaFirefox2.
0'santi-phishingtechnologyascomparedwithIE7.
0's.
ThisstudyfoundthatFirefox'santi-phishingtechnologywasbetterthanIE'sbyaconsiderablemarginItseemsevidentthatwecannottrustbothabovestudiesandforthisreasonweconsiderathirdindependentevaluationrealizedbytheSecurityLaboftheTechnicalUniversityofViennaInthelastmonthsthemajorbrowsers(e.
g.
IE7andMozillaFirefox)haveintegratedspecificanti-phishingfunctionalities(black-listsandstaticpageanalysis)AnalysisoftheBlack-ListsOveraperiodofthreeweekstheTechnicalUniversityofVienna(TUWIEN)hascollected10,000URLstobenchmarkMicrosoftandGoogle'sblack-lists.
Basedonthreeindicators,theresearchshowsthatGoogleperformsbetterthanMicrosoftCoverage:percentageofphishingURLsalreadyincludedinthelistQuality:percentageoflegitimateURLsincorrectlyincludedinthelistAverageResponseTime(ART):averagetimerequiredtoinsertnotinitiallyincludedURLs-KPI-2,413(67.
18%)3,241(90.
23%)BLTotal6.
4h9.
3hART2,139(59.
55%)274(7.
63%)3,157(87.
89%)84(2.
34%)BLinitallyBLdelayed3,592(100%)3,595(100%)SitesMicrosoftGoogle-ExperimentalResults-StaticPageAnalysisTUWIENhasdemonstratedthatasetofpagepropertiesactuallyallowstodifferentiatebetweenmalicious(phishing)andlegitimate(benign)onesSelectasetofpagepropertiesCollectwebpagestobeanalyzed18propertiesareconsideredmainlyextractedfromtheHTMLsourcecode(e.
g.
forms,inputfields,links,scripttags,etc.
)ExtracttheclassificationmodelInferaboutphishingAsetoflegitimateandphishingwebpagesarecollectedtoextracttheclassificationmodelTheC4.
2algorithmisexecutedtoidentifytheclassificationmodel(i.
e.
thedecion-tree)AnautomatictoolthatusestheextractedclassificationmodelcandistinguishphishingfromlegitimatewebpagesStaticPageAnalysis:ExperimentalResultsThedecision-treeisextractedusingtheWekapackage(algorithmJ48)onasetof4,829webpages-ReducedDecision-TreeextractedusingtheWekapackage-565115PhishingPages184,131LegitimatePagesClassifiedasPhishingClassifiedasLegitimate-ConfusionMatrix-Thequalifierisquitesuccessfulinidentifyingphishingpages(morethan80%arecorrectlyrecognized),raisingonlyaverysmallnumberoffalsealerts(18outof4,149pagesareincorrectlyclassifiedasphishing)StaticPageAnalysis:DemoStartingfromthetrainingdata-set,arealtimedemonstrationisprovidedInstalltheWekaPackageLoadtheinput".
arf"or".
csv"fileSelecttheJ48algorithmRuntheapplicationChecktheextractedtree-Stepstobeexecuted-InformationFlowSolutions:AntiPhish(1/2)Alimitednumberofinformationflowbasedsolutionswererealized.
TheobjectiveistoprotectusersbycheckingwheretheinformationissenttoAntiPhishisanapplicationthatisintegratedintothebrowserasanexternalplug-inAfterAntiPhishisinstalled,thebrowserpromptsarequestforanewmasterpasswordwhentheuserentersinputintoaformforthefirsttimeThemasterpasswordisusedtoencryptthesensitiveinformationbeforeitisstored(usingDES)Aftertheuserenterssensitiveinformationsuchasapassword,theAntiPhishmenuisusedtoscanthepageandtocaptureandstorethisinformationwiththedomainofthewebsite,too-Howdoesitlooklike--Generaldescription-InformationFlowSolutions:AntiPhish(2/2)TheexecutionflowchartofAntiPhishindicateshowthistoolallowtoprotectpotentialvictimsUserpresseskeyorpastestextintoformfieldCheckiftheinformationenteredisinthe"watch-list"Istheinfointhe"watch-list"DoesthedomaincorrespondThewebsiteistrusted.
ContinuenormallyUntrustedwebsite.
GenerateanalertNOYESNOYESAntiPhishdetectsthatsensitiveinformationhasbeentypedintoaformofanuntrusteddomainandcancelstheoperation.
Everytimeinformationisenteredintoaformelement(e.
g.
,textfield,textarea,etc.
),AntiPhishgoesthroughitslistofcaptured/cachedinformation.
Interactioneventstheusergenerateswithinthebrowser(keypresses,submissions,mouseclicks&focus)areinterceptedbeforeinformationcanflowtountrustedwebsite.
AntiPhishinActionWhenthevictiminsertshisusernameandpasswordtoanuntrustedwebsite,analertisraisedbeforesensitiveinformationaresenttothephisherAgenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsLayout-Similarity-basedSolutions(1/2)Layout-similarity-basedapproachesclassifyawebpageasaphishingpageifits"visual"similarityvalueisaboveapredefinedthreshold-Wenyinetal.
Approach-Thewebpageisdecomposedintosalientblocksaccordingto"visualcues".
Thevisualsimilaritybetweentwowebpagesismeasured.
Awebpageisconsideredaphishingpageifthesimilaritytothelegitimatewebpageishigherthanathreshold.
Layout-Similarity-basedSolutions(2/2)DOMAntiPhish[Rosiello,Kirda,Kruegel,Ferrandi]computesthesimilarityvalueextractingtheDOM-Treeoftheconsideredwebpages-DOMAntiPhishdescription-Whenapasswordassociatedwithacertaindomainisreusedonanotherdomainthesystemcomparesthelayoutofthecurrentpagewiththepagewherethesensitiveinformationwasoriginallyentered.
ForthecomparisontheDOM-Treeoftheoriginalwebpageandthenewonearechecked.
Ifthesystemdeterminesthatthesepageshaveasimilarappearance,aphishingattackisassumed-DOMAntiPhishFlowchart-DOMAntiPhish:DOM-TreeExtractionTheDocumentObjectModel(DOM)-Treeisaninternalrepresentationusedbybrowserstorepresentawebpage-HTMLsourcecode-ShadyGroveAeolianOvertheriverAlbert-DOM-Treerepresentation-DOMAntiPhish:SimilarityComputationDOM-TreesreducetheproblemofcomputingthelayoutsimilarityoftwowebpagestotheproblemofestablishingiftwotreesareisomorphicINPUTS:vertexv,vertexu,firstSubTreeФ,secondSubTreeФWHILEcontinue_whileexistsequivalent_subTrees_branchesDOfirstSubTree=getSubTree(u,firstSubTree);secondSubTree=getSubTree(v,secondSubTree);IFaresimilar(firstSubTree,secondSubTree)THENfloatpenalty=compute_similarity_penalty();storesubTrees(u,v,firstSubTree,secondSubTree,penalty);ENDIFENDWHILE-Templatescomputationalgorithm-Equaltemplatesextractedbythealgorithm.
Tocoverthetrees,thebestsetoftemplatesareselected(minimizingthesimilaritypenalties)-PhishingExample-DOMAntiPhish:ImplementationProcessDOMAntiPhishprototypeisimplementedasaJavascriptplug-inforMozillaFirefox2.
0whichinvokesaJavasoftwaretocomputethelayoutsimilarityDOM-TreeExtractionJavaSoftwareCallTheJavascriptplug-inforMozillaFirefox2.
0extractstheDOM-TreerepresentationofeachstoredwebpageandbrowsingoneTheJavascriptplug-inwritesdowntwotextfilesthatcontaintheextractedDOM-TreesTheJavascriptplug-ininvokestheJavasoftwareSimilarityLayoutCalculationTheJavasoftwarecalculatesthesimilarityoftheanalyzedDOM-TreeschoosingthesetoftemplateswhichminimizethesimilaritypenaltyandmaximizethecoveragePhishingReportTheJavascriptplug-inreadsthesimilarityvaluefromatextfileandreturnsthephishingreporttotheuserDOMAntiPhish:ExperimentalResultsDOMAntiPhishwastestedonasetofover200websitesprovingthatourapproachisfeasibleinpractice-Experimentalresultsdescription-Duringthesimilaritycomputationprocess,fortheisomorphicsubtreesidentificationalgorithm,weaddedapenaltyof0.
3iftwocorrespondingtagshaddifferenttypesorifatagdidnothavechildrenanditsmatchedcounterpartdid.
Iftwoattributesofmatchedtagsweredifferent,apenaltyof0.
1wasadded.
Moreover,iftheattributeshaddifferentvalues,thenapenaltyof0.
05wasadded,too.
Thepenaltyvaluesweredeterminedempiricallybyhavingasobjectivefunctiontheminimizationoffalsepositiveandnegativeresultsforlowandhighthresholdvaluesrespectively.
DOMAntiPhish:LimitationsAseverysecuritysolution,alsoDOMAntiPhishisnotperfectandwecanidentifythefollowingmainlimitations:Itcouldbepossibleforattackerstouseacombinationofimagestocreateaspoofedwebpagethatlooksvisuallysimilartoalegitimatewebpage.
Hence,theDOMofthespoofedwebpagewouldbedifferentanddetectionwouldbeevaded.
Onepossibilityofdealingwiththislimitationcouldbetotakeaconservativeapproachandtotagwebpagesasbeingsuspiciousthatcontainalargenumberofimagesorthatmainlyconsistofimages.
AnotherpossibleproblemcouldbeDOMobfuscationattemptsthatwouldmakethevisuallooksimilartothelegitimatewebpagewhileatthesametimeevadingdetection.
Ourapproachraisesthedifficultybarforcreatingphishingpages.
Furthermore,onecanalwaystakeamoreconservativeapproachbyreducingthephishingalertthreshold.
Also,ifphishersareforcedtoalterthelookandfeeloftheirphishingpages,thesepageswillbecomelessconvincingandmoresuspicioustothevictims.
-Potentialattacks--Defensivesolutions-DOMAntiPhish:DemoBrowsingsomewebpagesweshowhowDOMAntiPhishworksagainstphishingattacksInstallDOMAntiPhishplug-inLogintoatrustedwebsiteTrytologintoaphishingwebsiteCheckthephishingreport-Stepstobeexecuted-Agenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsConclusionsAsforeveryITattack,phishingcanbeprevented,detectedandmitigatedthroughserver-basedandclient-basedapproaches,supportedbyeducationandawarenessPeopleClient-basedtechniquestrytoprotectusersimplementinglocalsolutions,suchasbrowserplug-insore-mailclientsServerbasedtechniquesareappliedonserversorprovidersthatofferservicestocustomersReferencesAngeloP.
E.
Rosiello,EnginKirda,ChristopherKruegel,andFabrizioFerrandi.
"ALayout-Similarity-BasedApproachforDetectingPhishingPages".
IEEEInternationalConferenceonSecurityandPrivacyinCommunicationNetworks(SecureComm),Nice,France,September2007ChristianLudl,SeanMcAllister,EnginKirda,andChristopherKruegel.
"OntheEffectivenessofTechniquestoDetectPhishingSites".
DetectionofIntrusionsandMalwareandVulnerabilityAssessment(DIMVA)2007Conference,Lucerne,Switzerland,July2007EnginKirdaandChristopherKruegel.
"ProtectingUsersagainstPhishingAttacks".
TheComputerJournal,2006.
NeilChou,RobertLedesma,YukaTeraguchi,DanBoneh,andJohnMitchell.
"Client-sidedefenseagainstweb-basedidentitytheft".
In11thAnnualNetworkandDistributedSystemSecuritySymposium(NDSS'04),SanDiego,2005.
Anti-PhishingWorkingGroup(APWG).
APWGHomepage.
http://www.
antiphishing.
org/,2007.
InformationSecuritySurvey2007–InformationWeekResearch&AccentureGoogle.
GoogleWhitelist.
http://sb.
google.
com/safebrowsing/updateversion=goog-white-domain:1:-1,2007.
Mozilla.
Firefox2PhishingProtectionEffectivenessTesting.
http://www.
mozilla.
org/security/phishing-test.
html,2006.
Verisign.
Anti-PhishingSolution.
http://www.
verisign.
com/verisign-business-solutions/anti-phishing-solutions/,2005.
YueZhang,SergeEgelman,LorrieCranor,andJasonHong.
PhindingPhish:EvaluatingAnti-PhishingTools.
InNetworkandITSecurityConference:NDSS2007,SanDiego,California,2007.
Weka.
http://www.
cs.
waikato.
ac.
nz/ml/weka/
E.
RosielloAgenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsNatureofPhishing3.
8daysAveragetimeonlineforsiteU.
S.
Countryhostingthemostphishingwebsites149Numberofbrandshijackedbyphishingcampaigns37438Numberofuniquesites23415NumberofuniquereportsFinancialServicescontinuetobethemosttargetedindustrysectorat96.
9%ofallattacksinthemonthofMay-ListofthemainhighlightsreportedforMay2007-StatisticsfromtheAntiPhishingWorkingGroup(AWPG)confirmtheglobalnatureofphishingwhoseprimarytargetarefinancialinstitutionsGrowingEffectivenessandEfficiencyofPhishingOverthelastmonthsphishingattackshavebecomemoreeffectiveandcomplextotrackandchallengeUSChina-Thetop5listofbreaches-InformationWeekResearch&Accenture–InformationSecuritySurvey2007Phishingrepresentsthethirdtypeofsuccessfulattackagainstenterprises(mainlybanks)SymantechasdetectedanumberofphishingsitesthathavebeenhostedongovernmentURLsoverrecentmonths.
InJunealone(2007),fraudulentsiteswereidentifiedonsitesrunbythegovernmentsofThailand,Indonesia,Hungary,Bangladesh,Argentina,SriLanka,theUkraine,China,Brazil,BosniaandHerzegovina,Colombia,andMalaysia.
"HostingaphishingWebpageonagovernmentsitehasanumberofadvantagesforaphisher.
GovernmentWebsitesoftenreceiveahighvolumeoftraffic,sotheirserverscanhandletheextratrafficgeneratedbyaphishingsite"writesSymantecresearcherNickSullivan.
"Thisextratrafficmightnotbenoticedimmediately,givingthephishingsitealongerlifespanbeforeitisdetectedandshutdown.
Perhapsmostimportantly,hostingaphishingsiteonanactualgovernmentURLgivesthephishingsiteasenseofauthenticitythat'shardtobeat.
"-ImprovingPhishingqualityattacks-TaxonomyofPhishingAttacksPhishingattackscanbeclassifiedaccordingtotheirnatureEmail,IMPhishingAttacksE-mailIM,IRC,etc.
-Description-Spoofede-mailaresenttoasetofvictimsaskingthem(usually)toupgradetheirpasswords,dataaccount,etc.
MSN,ICQ,AOLandotherIMchannelsareusedtoreachthevictims.
Socialengineeringtechniquesareusedtogainvictim'ssensitiveinformationCallingthevictimsonthephone,classicsocialengineeringtechniquesareusedbyphishersAnotherkindofattackisbasedontheinternetbrowservulnerabilities.
ThisapproachisusuallyadoptedtoautomaticallyinstalldialersPhone,mail,etc.
Exploitbased-ClassificationoftheAttacks-AProcessofPhishingAttacksInatypicalattack,thephishersendsalargenumberofspoofed(i.
e.
fake)e-mailstorandomInternetusersthatseemtobecomingfromalegitimateandwell-knownbusinessorganization(e.
g.
financialinstitutions,creditcardcompanies,etc)Thee-mailurgesthevictimtoupdatehispersonalinformationasaconditiontoavoidloosingaccessrightstospecificservices(e.
g.
accesstoonlinebankaccount,etc).
Byclickingonthelinkprovided,thevictimisdirectedtoaboguswebsiteimplementedbytheattackerThephishingwebsiteisstructuredasacloneoftheoriginalwebsitesothatthevictimisnotabletodistinguishitfromthatoftheservicehe/shehasaccessto.
Lotsofe-mailsaresenttoasetofrandomvictimsThevictimchangesherdataE-mailurgesthevictimtoupdateherdataviaweb(aspoofedone)Phisher!
!
!
AFRUDNewPhishersSkillsToconfusethevictim,phishersaredevisingnewtricksPhishinge-mailembedhyperlinksfromtheoriginalwebsitesothattheusersmainlysurfontherealwebserverexecutingonlyasmallnumberofconnectionstothefakewebserver.
WebsiteURLareencodedorobfuscatedtonotraisesuspicious.
IDNspoofing,forexample,usesUnicodeURLsthatrenderURLsinbrowsersinawaythattheaddresslooksliketheoriginalwebsiteaddressbutactuallylinktoafakewebsitewithadifferentaddress.
VictimsareredirectedtoaphishingwebsitebyfirstusingmalwarestoinstallamaliciousBrowserHelperObject(BHO).
BHOsareDLLsthatallowsdeveloperstocustomizeandcontrolInternetExplorerbutalsophisherstocompromiseconnections.
Thehostsfileonthevictim'smachineiscorrupted,forexampleusingamalware.
ThehostfilesmaintainslocalmappingsbetweenDNSnamesandIPaddresses.
ByinsertingafakeDNSentryintotheuser'shostsfile,itwillappearthattheirwebbrowserisconnectingtoalegitimatewebsitewheninfactitisconnectingtoaphishingwebsite.
Agenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsStrategicDefenseTechniquesAntiphisingdefensescanbeserverandclientbasedsolutionsServer-basedAnti-PhishingClient-basedBehaviourDetectionBrandMonitoringSecurityEventsE-mailAnalysisBlackListsInformationFlowSimilarityofLayoutsFocusofthispresentation!
Server-basedSolutionsServerbasedtechniquesareimplementedbyserviceproviders(e.
g.
ISP,e-commercestores,financialinstitutions,etc…)Crawlingon-linewebsitestoidentify"clones"(lookingforlegitimatebrands),whichareconsideredphishingpages.
Suspectedwebsitesareaddedtoacentralized"black-list".
Foreachcustomeraprofileisidentified(afteratrainingperiod)whichisusedtodetectanomaliesinthebehaviourofusersSecurityeventanalysisandcorrelationusingregisteredeventsprovidedbyseveralsources(OS,application,networkdevice)toidentifyanomalousactivityorforpostmortemanalysisfollowinganattackorafraudUsingmorethanoneidentificationfactoriscalledstrongauthentication.
Therearethreeuniversallyrecognizedfactorsforauthenticatingindividuals:somethingyouknow(e.
g.
password);somethingyouhave(e.
g.
hwsecuritytoken);somethingyouare(e.
g.
fingerprint)Newtechniquesofauthenticationareunderreasearch,suchasusinganimageduringtheregistrationphasewhichisshownduringeveryloginprocessBrandMonitoringBehaviourDetectionSecurityEventMonitoringStrongAuthenticationNewAuthenticationTechniquesClient-basedSolutionsClient-basedtechniquesareimplementedonusers'endpointthroughbrowserplug-insore-mailclientsE-mail-basedapproachestypicallyusefiltersandcontentanalysis.
IftrainedregularlyBayesianfiltersareactuallyquiteeffectiveininterceptingbothspammingandphishinge-mails.
BlacklistsarecollectionsofURLsidentifiedasmalicious.
Theblacklistisqueriedbythebrowserrun-timewheneverapageisloaded.
IfthecurrentlyvisitedURLisincludedintheblacklist,theuserisadvisedofthedanger,otherwisethepageisconsideredlegitimate.
InformationflowsolutionsarebasedonthepremisethatwhileausermaybeeasilyfooledbyURLobfuscationorafakedomainname,aprogramwillnot.
AntiPhishisanexampleofthistypeofdefensetechniquewhichkeepstrackofthesensitiveinformationthattheuserentersintowebforms,raisinganalertifsomethingisconsideredunsafeMostadvancedtechniquestrytodistinguishaphishingwebpagefromthelegitimateonecomparingtheirvisualsimilarity[[Wenyin,Huang,Xiaoyue,Min,Deng],[Rosiello,Kirda,Kruegel,Ferrandi]E-mailAnalysisBlack-ListsInformationFlowSimilarityofLayoutsTrendsonclient-basedMarketSolutionsInOctober2006,aMicrosoft-commissionedreportonvariousanti-phishingsolutionswasreleased.
ThetestersfoundthatMicrosoftInternetExplorer(IE)7.
0hasbetteranti-phishingtechnologythancompetingsolutions.
TheproductstestedincludedIE7.
0Beta3,EarthLinkScamBlocker,eBayToolbarwithAccountGuard,GeoTrustTrustWatch,GoogleToolbarforFirefoxwithSafeBrowsing,McAfeeSiteAdvisorPlus,NetcraftToolbar,andNetscapeBrowserwithbuilt-inantiphishingtechnologyTheMozillaFoundationcommissioneditsownstudytogaugetheeffectivenessofMozillaFirefox2.
0'santi-phishingtechnologyascomparedwithIE7.
0's.
ThisstudyfoundthatFirefox'santi-phishingtechnologywasbetterthanIE'sbyaconsiderablemarginItseemsevidentthatwecannottrustbothabovestudiesandforthisreasonweconsiderathirdindependentevaluationrealizedbytheSecurityLaboftheTechnicalUniversityofViennaInthelastmonthsthemajorbrowsers(e.
g.
IE7andMozillaFirefox)haveintegratedspecificanti-phishingfunctionalities(black-listsandstaticpageanalysis)AnalysisoftheBlack-ListsOveraperiodofthreeweekstheTechnicalUniversityofVienna(TUWIEN)hascollected10,000URLstobenchmarkMicrosoftandGoogle'sblack-lists.
Basedonthreeindicators,theresearchshowsthatGoogleperformsbetterthanMicrosoftCoverage:percentageofphishingURLsalreadyincludedinthelistQuality:percentageoflegitimateURLsincorrectlyincludedinthelistAverageResponseTime(ART):averagetimerequiredtoinsertnotinitiallyincludedURLs-KPI-2,413(67.
18%)3,241(90.
23%)BLTotal6.
4h9.
3hART2,139(59.
55%)274(7.
63%)3,157(87.
89%)84(2.
34%)BLinitallyBLdelayed3,592(100%)3,595(100%)SitesMicrosoftGoogle-ExperimentalResults-StaticPageAnalysisTUWIENhasdemonstratedthatasetofpagepropertiesactuallyallowstodifferentiatebetweenmalicious(phishing)andlegitimate(benign)onesSelectasetofpagepropertiesCollectwebpagestobeanalyzed18propertiesareconsideredmainlyextractedfromtheHTMLsourcecode(e.
g.
forms,inputfields,links,scripttags,etc.
)ExtracttheclassificationmodelInferaboutphishingAsetoflegitimateandphishingwebpagesarecollectedtoextracttheclassificationmodelTheC4.
2algorithmisexecutedtoidentifytheclassificationmodel(i.
e.
thedecion-tree)AnautomatictoolthatusestheextractedclassificationmodelcandistinguishphishingfromlegitimatewebpagesStaticPageAnalysis:ExperimentalResultsThedecision-treeisextractedusingtheWekapackage(algorithmJ48)onasetof4,829webpages-ReducedDecision-TreeextractedusingtheWekapackage-565115PhishingPages184,131LegitimatePagesClassifiedasPhishingClassifiedasLegitimate-ConfusionMatrix-Thequalifierisquitesuccessfulinidentifyingphishingpages(morethan80%arecorrectlyrecognized),raisingonlyaverysmallnumberoffalsealerts(18outof4,149pagesareincorrectlyclassifiedasphishing)StaticPageAnalysis:DemoStartingfromthetrainingdata-set,arealtimedemonstrationisprovidedInstalltheWekaPackageLoadtheinput".
arf"or".
csv"fileSelecttheJ48algorithmRuntheapplicationChecktheextractedtree-Stepstobeexecuted-InformationFlowSolutions:AntiPhish(1/2)Alimitednumberofinformationflowbasedsolutionswererealized.
TheobjectiveistoprotectusersbycheckingwheretheinformationissenttoAntiPhishisanapplicationthatisintegratedintothebrowserasanexternalplug-inAfterAntiPhishisinstalled,thebrowserpromptsarequestforanewmasterpasswordwhentheuserentersinputintoaformforthefirsttimeThemasterpasswordisusedtoencryptthesensitiveinformationbeforeitisstored(usingDES)Aftertheuserenterssensitiveinformationsuchasapassword,theAntiPhishmenuisusedtoscanthepageandtocaptureandstorethisinformationwiththedomainofthewebsite,too-Howdoesitlooklike--Generaldescription-InformationFlowSolutions:AntiPhish(2/2)TheexecutionflowchartofAntiPhishindicateshowthistoolallowtoprotectpotentialvictimsUserpresseskeyorpastestextintoformfieldCheckiftheinformationenteredisinthe"watch-list"Istheinfointhe"watch-list"DoesthedomaincorrespondThewebsiteistrusted.
ContinuenormallyUntrustedwebsite.
GenerateanalertNOYESNOYESAntiPhishdetectsthatsensitiveinformationhasbeentypedintoaformofanuntrusteddomainandcancelstheoperation.
Everytimeinformationisenteredintoaformelement(e.
g.
,textfield,textarea,etc.
),AntiPhishgoesthroughitslistofcaptured/cachedinformation.
Interactioneventstheusergenerateswithinthebrowser(keypresses,submissions,mouseclicks&focus)areinterceptedbeforeinformationcanflowtountrustedwebsite.
AntiPhishinActionWhenthevictiminsertshisusernameandpasswordtoanuntrustedwebsite,analertisraisedbeforesensitiveinformationaresenttothephisherAgenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsLayout-Similarity-basedSolutions(1/2)Layout-similarity-basedapproachesclassifyawebpageasaphishingpageifits"visual"similarityvalueisaboveapredefinedthreshold-Wenyinetal.
Approach-Thewebpageisdecomposedintosalientblocksaccordingto"visualcues".
Thevisualsimilaritybetweentwowebpagesismeasured.
Awebpageisconsideredaphishingpageifthesimilaritytothelegitimatewebpageishigherthanathreshold.
Layout-Similarity-basedSolutions(2/2)DOMAntiPhish[Rosiello,Kirda,Kruegel,Ferrandi]computesthesimilarityvalueextractingtheDOM-Treeoftheconsideredwebpages-DOMAntiPhishdescription-Whenapasswordassociatedwithacertaindomainisreusedonanotherdomainthesystemcomparesthelayoutofthecurrentpagewiththepagewherethesensitiveinformationwasoriginallyentered.
ForthecomparisontheDOM-Treeoftheoriginalwebpageandthenewonearechecked.
Ifthesystemdeterminesthatthesepageshaveasimilarappearance,aphishingattackisassumed-DOMAntiPhishFlowchart-DOMAntiPhish:DOM-TreeExtractionTheDocumentObjectModel(DOM)-Treeisaninternalrepresentationusedbybrowserstorepresentawebpage-HTMLsourcecode-ShadyGroveAeolianOvertheriverAlbert-DOM-Treerepresentation-DOMAntiPhish:SimilarityComputationDOM-TreesreducetheproblemofcomputingthelayoutsimilarityoftwowebpagestotheproblemofestablishingiftwotreesareisomorphicINPUTS:vertexv,vertexu,firstSubTreeФ,secondSubTreeФWHILEcontinue_whileexistsequivalent_subTrees_branchesDOfirstSubTree=getSubTree(u,firstSubTree);secondSubTree=getSubTree(v,secondSubTree);IFaresimilar(firstSubTree,secondSubTree)THENfloatpenalty=compute_similarity_penalty();storesubTrees(u,v,firstSubTree,secondSubTree,penalty);ENDIFENDWHILE-Templatescomputationalgorithm-Equaltemplatesextractedbythealgorithm.
Tocoverthetrees,thebestsetoftemplatesareselected(minimizingthesimilaritypenalties)-PhishingExample-DOMAntiPhish:ImplementationProcessDOMAntiPhishprototypeisimplementedasaJavascriptplug-inforMozillaFirefox2.
0whichinvokesaJavasoftwaretocomputethelayoutsimilarityDOM-TreeExtractionJavaSoftwareCallTheJavascriptplug-inforMozillaFirefox2.
0extractstheDOM-TreerepresentationofeachstoredwebpageandbrowsingoneTheJavascriptplug-inwritesdowntwotextfilesthatcontaintheextractedDOM-TreesTheJavascriptplug-ininvokestheJavasoftwareSimilarityLayoutCalculationTheJavasoftwarecalculatesthesimilarityoftheanalyzedDOM-TreeschoosingthesetoftemplateswhichminimizethesimilaritypenaltyandmaximizethecoveragePhishingReportTheJavascriptplug-inreadsthesimilarityvaluefromatextfileandreturnsthephishingreporttotheuserDOMAntiPhish:ExperimentalResultsDOMAntiPhishwastestedonasetofover200websitesprovingthatourapproachisfeasibleinpractice-Experimentalresultsdescription-Duringthesimilaritycomputationprocess,fortheisomorphicsubtreesidentificationalgorithm,weaddedapenaltyof0.
3iftwocorrespondingtagshaddifferenttypesorifatagdidnothavechildrenanditsmatchedcounterpartdid.
Iftwoattributesofmatchedtagsweredifferent,apenaltyof0.
1wasadded.
Moreover,iftheattributeshaddifferentvalues,thenapenaltyof0.
05wasadded,too.
Thepenaltyvaluesweredeterminedempiricallybyhavingasobjectivefunctiontheminimizationoffalsepositiveandnegativeresultsforlowandhighthresholdvaluesrespectively.
DOMAntiPhish:LimitationsAseverysecuritysolution,alsoDOMAntiPhishisnotperfectandwecanidentifythefollowingmainlimitations:Itcouldbepossibleforattackerstouseacombinationofimagestocreateaspoofedwebpagethatlooksvisuallysimilartoalegitimatewebpage.
Hence,theDOMofthespoofedwebpagewouldbedifferentanddetectionwouldbeevaded.
Onepossibilityofdealingwiththislimitationcouldbetotakeaconservativeapproachandtotagwebpagesasbeingsuspiciousthatcontainalargenumberofimagesorthatmainlyconsistofimages.
AnotherpossibleproblemcouldbeDOMobfuscationattemptsthatwouldmakethevisuallooksimilartothelegitimatewebpagewhileatthesametimeevadingdetection.
Ourapproachraisesthedifficultybarforcreatingphishingpages.
Furthermore,onecanalwaystakeamoreconservativeapproachbyreducingthephishingalertthreshold.
Also,ifphishersareforcedtoalterthelookandfeeloftheirphishingpages,thesepageswillbecomelessconvincingandmoresuspicioustothevictims.
-Potentialattacks--Defensivesolutions-DOMAntiPhish:DemoBrowsingsomewebpagesweshowhowDOMAntiPhishworksagainstphishingattacksInstallDOMAntiPhishplug-inLogintoatrustedwebsiteTrytologintoaphishingwebsiteCheckthephishingreport-Stepstobeexecuted-Agenda1.
Briefintroductiontophishing2.
Strategicdefensetechniques3.
Anewclientbasedsolution:DOMAntiPhish4.
ConclusionsConclusionsAsforeveryITattack,phishingcanbeprevented,detectedandmitigatedthroughserver-basedandclient-basedapproaches,supportedbyeducationandawarenessPeopleClient-basedtechniquestrytoprotectusersimplementinglocalsolutions,suchasbrowserplug-insore-mailclientsServerbasedtechniquesareappliedonserversorprovidersthatofferservicestocustomersReferencesAngeloP.
E.
Rosiello,EnginKirda,ChristopherKruegel,andFabrizioFerrandi.
"ALayout-Similarity-BasedApproachforDetectingPhishingPages".
IEEEInternationalConferenceonSecurityandPrivacyinCommunicationNetworks(SecureComm),Nice,France,September2007ChristianLudl,SeanMcAllister,EnginKirda,andChristopherKruegel.
"OntheEffectivenessofTechniquestoDetectPhishingSites".
DetectionofIntrusionsandMalwareandVulnerabilityAssessment(DIMVA)2007Conference,Lucerne,Switzerland,July2007EnginKirdaandChristopherKruegel.
"ProtectingUsersagainstPhishingAttacks".
TheComputerJournal,2006.
NeilChou,RobertLedesma,YukaTeraguchi,DanBoneh,andJohnMitchell.
"Client-sidedefenseagainstweb-basedidentitytheft".
In11thAnnualNetworkandDistributedSystemSecuritySymposium(NDSS'04),SanDiego,2005.
Anti-PhishingWorkingGroup(APWG).
APWGHomepage.
http://www.
antiphishing.
org/,2007.
InformationSecuritySurvey2007–InformationWeekResearch&AccentureGoogle.
GoogleWhitelist.
http://sb.
google.
com/safebrowsing/updateversion=goog-white-domain:1:-1,2007.
Mozilla.
Firefox2PhishingProtectionEffectivenessTesting.
http://www.
mozilla.
org/security/phishing-test.
html,2006.
Verisign.
Anti-PhishingSolution.
http://www.
verisign.
com/verisign-business-solutions/anti-phishing-solutions/,2005.
YueZhang,SergeEgelman,LorrieCranor,andJasonHong.
PhindingPhish:EvaluatingAnti-PhishingTools.
InNetworkandITSecurityConference:NDSS2007,SanDiego,California,2007.
Weka.
http://www.
cs.
waikato.
ac.
nz/ml/weka/
- solutionssb相关文档
- 学习2013河南南阳市中考成绩查询网址:www.nyzsb.com.cn
- 登陆中国知网的主页http://www.cnki.net/,点击页面左侧的个人/机构数字图书馆,可以选择手动创建,也可以选择通过第三方账号登录:
提速啦 韩国服务器 E3 16G 3IP 450元/月 韩国站群服务器 E3 16G 253IP 1100元/月
提速啦(www.tisula.com)是赣州王成璟网络科技有限公司旗下云服务器品牌,目前拥有在籍员工40人左右,社保在籍员工30人+,是正规的国内拥有IDC ICP ISP CDN 云牌照资质商家,2018-2021年连续4年获得CTG机房顶级金牌代理商荣誉 2021年赣州市于都县创业大赛三等奖,2020年于都电子商务示范企业,2021年于都县电子商务融合推广大使。资源优势介绍:Ceranetwo...
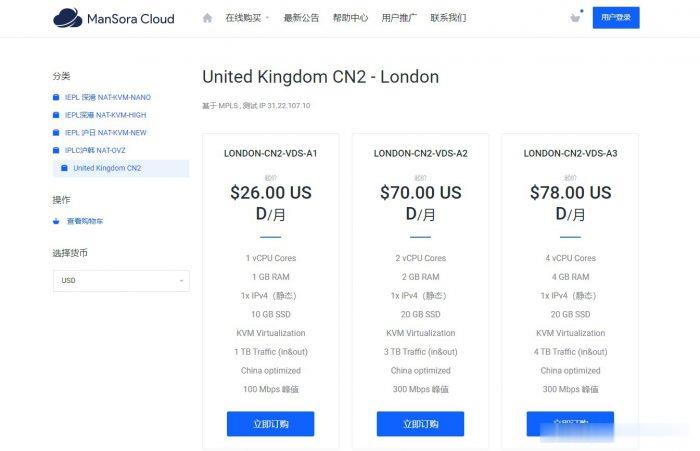
ManSora:英国CN2 VPS,1核/1GB内存/10GB SSD/1TB流量/100Mbps/KVM,$18.2/月
mansora怎么样?mansora是一家国人商家,主要提供沪韩IEPL、沪日IEPL、深港IEPL等专线VPS。现在新推出了英国CN2 KVM VPS,线路为AS4809 AS9929,可解锁 Netflix,并有永久8折优惠。英国CN2 VPS,$18.2/月/1GB内存/10GB SSD空间/1TB流量/100Mbps端口/KVM,有需要的可以关注一下。点击进入:mansora官方网站地址m...
港云网络(¥1/月活动机器),香港CN2 4核4G 1元/月 美国CN2
港云网络官方网站商家简介港云网络成立于2016年,拥有IDC/ISP/云计算资质,是正规的IDC公司,我们采用优质硬件和网络,为客户提供高速、稳定的云计算服务。公司拥有一流的技术团队,提供7*24小时1对1售后服务,让您无后顾之忧。我们目前提供高防空间、云服务器、物理服务器,高防IP等众多产品,为您提供轻松上云、安全防护。点击进入港云网络官方网站港云网络中秋福利1元领【每人限量1台】,售完下架,活...
www.nyzsb.com.cn为你推荐
-
exportingjavatracerouteLinux 下traceroute的工作原理是什么 !tcpip上的netbios禁用tcp/ip上的netbios对网络应用软件的正常运行有没有影响?联通版iphone4s苹果4S移动版和联通版有什么不同google分析google分析打不开了?ipad无法加入网络为什么我的ipad加入网络没法用苹果5.1完美越狱iOS5.1.1完美越狱教程fastreport2.5空调滤芯pm2.5是什么意思?chrome17谷歌浏览器和谷歌浏览器稳定版有什么区别altools.u32keil中字符类型u32什么意思