项目文献原文-SMTP Service Extension for Authentication
外文文献原文
SMTP Service Extension for Authentication
This document specifies an Internet standards track protocol for the Internet community,and requests discussion and suggestions for improvements.Please refer to the current edition ofthe"Internet O fficial Protocol Standards"(STD 1)for the standardization state and status o fthisprotoco l.Distribution o f this memo is unlimited.
Copyright Notice
Copyright(C)The Internet Society(1999).All Rights Reserved.
1. Intro d uc t io n
This document defines an SMTP service extension[ESMTP]whereby an SMTP clientmay indicate an authentication mechanism to the server,perform an authentication protocolexchange, and optionally negotiatea security layer for subsequent protocol interactions.Thisextension is a profile of the Simple Authentication and Security Layer[SASL].
2.Conventions Used in this Document
In examples, "C:"and"S:" indicate lines sentby the client and serverrespectively.The keywords "MUS T", "MUST NOT", "SHOULD", "SHOULD NOT",and"MAY" in this documentare to be interpreted as defined in"Key words for use in RFCs to Indicate Requirement Levels"[KEYWORDS].
3.The Authentication service extension
(1) the name of the SMTP service extension is "Authentication"
(2) the EHLO keyword value associated with this extension is "AUTH"
(3)The AUTH EHLO keyword contains as a parameter a space separated list of the namesof supported SASL mechanisms.
(4)a new SMTP verb"AUTH" is defined
(5) an optional parameter using the keyword "AUTH" is added to the MAIL FROMcommand, and extends the maximum line length of the MAIL FROM command by 500characte rs.
(6) this extension is appropriate for the submission protocol [SUBMIT].
参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
4.The AUTH command AUTH mechanism[initial-response]
Ar gume nts:a string identifying a SASL authentication mechanism. an optional base64-encodedre sp o nse
Restrictions:
After an AUTH command has successfully completed,no more AUTH commands may beissued in the same session.After a successful AUTH command completes, a server MUSTreject any further AUTH commands with a 503 reply.The AUTH command is not permittedduring a mail transaction.
Discussion:
The AUTH command indicates an authentication mechanism to the server. If the serversupports the requested authentication mechanism, it performs an authentication protocolexchange to authenticate and identify the user.Optionally, it also negotiates a security layer forsubsequent protocol interactions. If the requested authentication mechanism is not supported,the server rejects the AUTH command with a 504 reply.
The authentication protocol exchange consists of a series of server challenges and clientanswers that are specific to the authentication mechanism.A server challenge,otherwise knownas a ready response, is a 334 reply with the text part containing a BASE64 encoded string.Theclient answer consists of a line containing a BASE64 encoded string. If the client wishes tocancel an authentication exchange, it issues a line with a single "*". If the server receives suchan answer, it MUST reject the AUTH command by sending a 501 reply.
The optional initial-response argument to the AUTH command is used to save a round tripwhen using authentication mechanisms that are defined to send no data in the initial challenge.
When the initial-response argument is used with such a mechanism, the initial emptychallenge is not sent to the client and the server uses the data in the initial-response argument asif it were sent in response to the empty challenge.Unlike a zero-length client answer to a 334reply,a zero- length initial response is sent as a single equals sign("="). If the client uses aninitial-response argument to the AUTH command with a mechanism that sends data in theinitial challenge, the server rejects the AUTH command with a 535 reply.
参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
If the server cannot BASE64 decode the argument, it rejects the AUTH command with a501 reply. If the server rejects the authentication data, it SHOULD reject the AUTH commandwith a 535 reply unless a more specific error code, such as one listed in section 6, is appropriate.Should the client successfully complete the authentication exchange, the SMTP server issues a235 rep ly.
The service name specified by this protocol's profile of SASL is "smtp".
If a security layer is negotiated through the SASL authentication exchange, it takes effectimmediately following the CRLF that concludes the authentication exchange for the client,andthe CRLF of the success reply for the server.Upon a security layer's taking effect, the SMTPprotocol is reset to the initial state(the state in SMTP after a server issues a 220 service readygreeting).The server MUST discard any knowledge obtained from the client, such as theargument to the EHLO command,which was not obtained from the SASL negotiation itself.The client MUST discard any knowledge obtained from the server, such as the list of SMTPservice extensions,which was not obtained from the SASL negotiation itself (with theexception that a client MAY compare the list ofadvertised SASL mechanisms before and afterauthentication in order to detect an active down-negotiation attack).The client SHOULD sendan EHLO command as the first command after a successful SASL negotiation which results inthe enabling ofa security layer.
The server is not required to support any particular authentication mechanism,nor areauthentication mechanisms required to support any security layers. If an AUTH command fails,the client may try another authentication mechanismby issuing another AUTH command.
If an AUTH command fails, the server MUST behave the same as if the client had notissued the AUTH command.
The BASE64 string may in general be arbitrarily long.Clients and servers MUST be ableto support challenges and responses that are as long as are generated by the authenticationmechanisms they support, independent of any line length limitations the client or server mayhave in other parts of its protocol implementation.
Examples:
参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
S:220 smtp.example.com ESMTP server ready
C:EHLO j gm.example.com
S:250-smtp.example.com
S:250 AUTH CRAM-MD5 DIGEST-MD5
C:AUTH FOOBAR
S:504 Unrecognized authentication type.
C:AUTH CRAM-MD5
S:334
PENCeUxFREJoU0NnbmhN WitOMjNGNndAZWx3b29kLmlubm9 zb2 Z0 LmN vb T4=
C:ZnJlZC A5ZTk 1 YWVlMD ljNDBhZjJiODRhM GMyYjN iYmF lN zg2 ZQ==
S:235 Authentication successful.
5.The AUTH parameter to the MAILFROM command
AUTH=addr-spec
Ar gume nts:
An addr-spec containing the identity which submitted the message to the delivery system,or the two character sequence "<>" indicating such an identity is unknown or insufficientlyauthenticated.To comply with the restrictions imposed on ESMTP parameters, the addr-spec isencoded inside an xtext.The syntax of an xtext is described in section 5 of[ESMTP-DSN].
Discussion:
The optional AUTH parameter to the MAIL FROM command allows cooperating agentsin a trusted environment to communicate the authentication o f individual message s.
Ifthe server trusts the authenticated identity of the client toassert that the message was originally submitted by the supplied addr-spec, then the serverSHOULD supply the same addr-spec in an AUTH parameter when relaying the message to any参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
server which supports the AUTH extension.
A MAIL FROM parameter of AUTH=<> indicates that the original submitter of themessage is not known.The server MUST NOT treat the message as having been originallysubmitted by the c lient.
If the AUTH parameter to the MAIL FROM is not supplied, the client has authenticated,and the server believes the message is an original submission by the client, the server MAYsupply the client's identity in the addr-spec in an AUTH parameter when relaying the messageto any server which supports the AUTH extension.
If the server does not sufficiently trust the authenticated identity of the client, or if theclient is not authenticated, then the server MUST behave as if the AUTH=<>parameter wassupplied.The server MAY,however,write the value of the AUTH parameter to a log file.
If anAUTH=<>parameter was supplied,either explicitly or due to the requirement in theprevious paragraph, then the server MUST supply the AUTH=<>parameter when relaying themessage to any server which it has authenticated to using the AUTH extension.
A server MAY treat expansion of a mailing list as a new submission, setting the AUTHparameter to the mailing list address or mailing list administration address when relaying themessage to list subscribers.
It is conforming for an implementation to be hard-coded to treat all clients as beinginsufficiently trusted. In that case, the implementation does nothing more than parse anddiscard syntactically valid AUTH parameters to the MAIL FROM command and supplyAUTH=<>parameters to any servers to which it authenticates using the AUTH extension.
Examples:
C:MAILFROM:<e=mc2@example.com>AUTH=e+3Dmc2@example.com
S:250 OK
6.Error Codes
The following error codes maybe used to indicate various conditions as described.
432 A password transition is needed
参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
This response to the AUTH command indicates that the user needs to transition to theselected authentication mechanism. This typically done by authenticating once using thePLAIN authentication mechanism.
534 Authentication mechanism is too weak
This response to the AUTH command indicates that the selected authenticationmechanism is weaker than server policy permits for that user.
538 Encryption required for requested authentication mechanism
This response to the AUTH command indicates that the selected authenticationmechanism may only be used when the underlying SMTP connection is encrypted.
454 Temporary authentication failure
This response to the AUTH command indicates that the authentication failed due to atemporary server failure.
530 Authentication required
This response maybe returned by any command other than AUTH,EHLO,HELO,NOOP,RSET,or QUIT. It indicates that server policy requires authentication in order to perform therequested action.
7.Formal S yntax
The following syntax specification uses the augmented Backus-Naur Form(BNF)notation as specified in[ABNF].
Except as noted otherwise,all alphabetic characters are case- insensitive.The use of upperor lower case characters to define token strings is for editorial clarity only. ImplementationsMUST accept these strings in a case-insensitive fashion.
参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
UPALPHA=%x41-5A; ;Uppercase:A-Z
LO ALPHA=%x61-7A;;Low ercase:a-z
ALPHA=UPALPHA/LOALPHA;;case insensitive
DIGIT=%x30-39;;Digits 0-9
HEXDIGIT=%x41-46/DIGIT; ;hexidec imal digit(upp ercase)hexchar="+"HEXDIGIT HEXDIGITxchar=%x21-2A/%x2C-3C/%x3E-7E; ;US-ASCII except for "+", "=",SPACE andCTLxtext=*(xchar/hexchar)
AUTH_CHAR=ALPHA/DIGIT/ "-" / "_"
auth_type=1*20AUTH_CHARauth_command="AUTH"SPAC E auth_type [SPAC E(base64/ "=")]*(CRLF[base64])CRLFauth_param= "AUTH=" xtext;; The decoded form of the xtext MUST be either;; anaddr-spec or the two characters "<>"base64=base64_terminal/( 1*(4b ase64_CHAR) [base64_terminal] )base64_c har=UPALP HA/LOALPHA/DI GIT/ "+"/ "/"; ;C ase-se ns itivebase64_terminal=(2bas e64_char "==")/(3b ase64_char "=")continue_req="334"SPACE[base64]C RLF
CR=%x0C;;ASCII CR,carriage return
CRLF=CR LF
CTL=%x00-1F/%x7F; ;any ASCII control character and DEL
LF=%x0A; ;ASCII LF, line feed
SPACE=%x20; ;ASCII SP, space
8.References
[ABNF]Crocker,D.and P.Overell, "Augmented BNF for Syntax Specifications:ABNF",RFC2234,November 1997.
[CRAM-MD5]Klensin, J., Catoe, R. and P.Krumviede, "IMAP/POP AUTHorize参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
Extension for Simple Challenge/Response",RFC 2195,September 1997.
[ESMTP]Klensin,J.,Freed,N.,Rose,M., Stefferud,E. and D.Crocker, "SMTP ServiceExtensions",RFC1869,November 1995.
[ESMTP-DSN]Moore,K, "SMTP Service Extension for Delivery Status Notifications",RFC 1891,January 1996.
[KEYWORDS]Bradner,S., "Key words for use in RFCs to Indicate Requirement Levels",BCP 14,RFC2119,March 1997
[SASL]Myers, J., "Simple Authentication and Security Layer (SASL)",RFC2222,October 1997.
[SUBMIT]Gellens,R. and J.Klensin, "Message Submission",RFC 2476,December
1998.
[RFC821]Postel,J., "Simple Mail Transfer Protocol",STD 10,RFC 821,August 1982.
[RFC822]Crocker,D., "Standard for the Format of ARPA Internet Text Messages",STD11,RFC822,August 1982.
9.Security Considerations
Security issues are discussed throughout this memo.
If a client uses this extension to get an encrypted tunnel through an insecure network to acooperating server, it needs to be configured to never send mail to that server when theconnection is not mutually authenticated and encrypted.Otherwise,an attacker could steal theclient's mail by hijacking the SMTP connection and either pretending the server does notsupport the Authentication extension or causing all AUTH commands to fail.
Before the SASL negotiation has begun, any protocol interactions are performed in theclear and may be modified by an active attacker.For this reason, clients and servers MUSTdiscard anyknowledge obtained prior to the start ofthe SASL negotiation upon completion of aSASL negotiation which results in a security layer.
This mechanism does not protect the TCP port, so an active attacker may redirect a relayconnection attempt to the submis sion port [SUBMIT].The AUTH=<>parameter prevents suchan attack from causing an relayed message without an envelope authentication to pick up theauthentication ofthe relay client.
参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
A message submission client may require the user to authenticate whenever a suitableSASL mechanism is advertised.Therefore, it may not be desirable for a submission server[SUBMIT] to advertise a SASL mechanism when use of that mechanism grants the client nobenefits over anonymous submis sion.
This extension is not intended to replace or be used instead of end- to-end messagesignature and encryption systems such as S/MIME or PGP.This extension addresses a differentproblem than end-to-end systems; it has the following key differences:
(1) it is generally useful only within a trusted enclave
(2) it protects the entire envelope of a message,not just the message's body.
(3) it authenticates the message submission,not authorship of the message content
(4) it can give the sender some assurance the message was delivered to the next hop in thecase where the sender mutually authenticates with the next hop and negotiates an appropriatesecurity layer.
Additional security considerations are mentioned in the SASL specification[SASL].参考设计材料包含项目源代码屏幕录像指导、项目运行截图、项目设计说明书、任务书、报告书以及文献参考翻译等完整的
设计文件及源代码资料请联系68661508(bshhty)索要
- 项目文献原文-SMTP Service Extension for Authentication相关文档
- 3.extension_dir
- Editextension_dir
- Priceextension_dir
- languagesextension_dir
- 如有Chromium扩展(Extension)的页面(Page)加载过程分析
- 指定ChDir、ChDrive,Dir等的使用说明
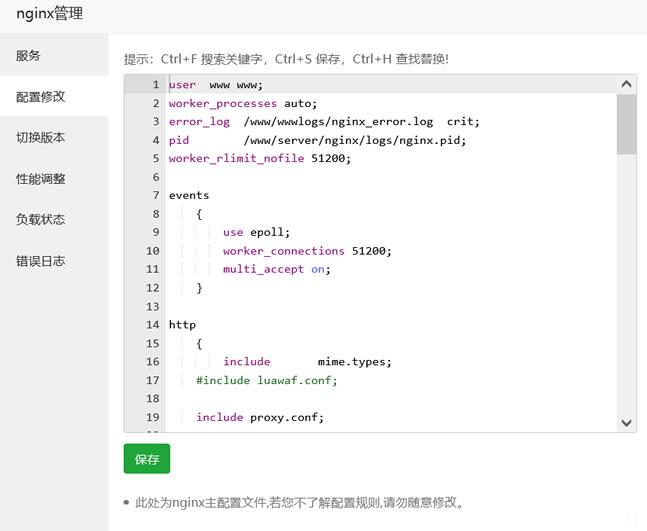
宝塔面板批量设置站点404页面
今天遇到一个网友,他在一个服务器中搭建有十几个网站,但是他之前都是采集站点数据很大,但是现在他删除数据之后希望设置可能有索引的文章给予404跳转页面。虽然他程序有默认的404页面,但是达不到他引流的目的,他希望设置统一的404页面。实际上设置还是很简单的,我们找到他是Nginx还是Apache,直接在引擎配置文件中设置即可。这里有看到他采用的是宝塔面板,直接在他的Nginx中设置。这里我们找到当前...
RackNerd 黑色星期五5款年付套餐
RackNerd 商家从2019年上线以来争议也是比较大的,一直低价促销很多网友都认为坚持时间不长可能会跑路。不过,目前看到RackNerd还是在坚持且这次黑五活动也有发布,且活动促销也是比较多的,不过对于我们用户来说选择这些低价服务商尽量的不要将长远项目放在上面,低价年付套餐服务商一般都是用来临时业务的。RackNerd商家这次发布黑五促销活动,一共有五款年付套餐,涉及到多个机房。最低年付的套餐...
韩国服务器租用优惠点评大全
韩国服务器怎么样?韩国云服务器租用推荐?韩国服务器距离中国近,有天然的地域优势,韩国服务器速度快而且非常稳定!有不少有亚洲市场的外贸公司选择韩国服务器开拓业务,韩国服务器因自身的优势也受到不少用户的青睐。目前的IDC市场上,韩国、香港、美国三个地方的服务器几乎占据了海外服务器的百分之九十以上。韩国服务器相比美国服务器来说速度更快,而相比香港机房来说则带宽更充足,占用市场份额非常大。那么,韩国服务器...
-
openeuler谁知道open opened close closed的区别吗杨紫别祝我生日快乐一个人过生日的伤感说说有什么甲骨文不满赔偿公司倒闭员工不满一年怎么赔偿陈嘉垣电视剧《反黑》里面,雷太太女儿扮演者是谁?同ip域名不同域名解析到同一个IP是否有影响sss17.com一玩棋牌吧(www.17wqp.com)怎么样?www.vtigu.com如图所示的RT三角形ABC中,角B=90°(初三二次根式)30 如图所示的RT三角形ABC中,角B=90°,点p从点B开始沿BA边以1厘米每秒的速度向A移动;同时,点Q也从点B开始沿BC边以2厘米每秒的速度向点C移动。问:几秒后三角形PBQ的面积为35平方厘米?PQ的距离是多少ip查询器怎么样查看自己电脑上的IP地址99nets.com制作网络虚拟证件的网站 那里有呀?www.hyyan.com请问我是HY了吗?在线等