openhiberfil
hiberfil 时间:2021-01-30 阅读:()
ThischeatsheetsupportstheSANSFOR508AdvancedDigitalForensics,IncidentResponse,andThreatHunting&SANSFOR526MemoryForensicsIn-Depthcourses.
ItisnotintendedtobeanexhaustiveresourceforVolatilityorotherhighlightedtools.
VolatilityisatrademarkofVerizon.
TheSANSInstituteisnotsponsored,approvedbyoraffiliatedwithVerizon.
Thetimelinerpluginparsestime-stampedobjectsfoundinmemoryimages.
Outputissortedby:ProcesscreationtimeThreadcreationtimeDrivercompiletimeDLL/EXEcompiletimeNetworksocketcreationtimeMemoryresidentregistrykeylastwritetimeMemoryresidenteventlogentrycreationtimetimeliner--output-fileOptionalfiletowriteoutput--output=bodyBodyfileformat(alsotext,xlsx)--type=RegistryExtractregistrykeylastwritetimes#vol.
py-fmem.
imgtimeliner--output-fileout.
body--output=body--profile=Win10x64MemoryArtifactTimeliningPurposeHowToUseThisDocumentMemoryanalysisisoneofthemostpowerfultoolsavailabletoforensicexaminers.
Thisguidehopestosimplifytheoverwhelmingnumberofavailableoptions.
Analysiscangenerallybeaccomplishedinsixsteps:1.
IdentifyRogueProcesses2.
AnalyzeProcessDLLsandHandles3.
ReviewNetworkArtifacts4.
LookforEvidenceofCodeInjection5.
CheckforSignsofaRootkit6.
ExtractProcesses,Drivers,andObjectsWeoutlinethemostusefulVolatilitypluginssupportingthesesixstepshere.
Furtherinformationisprovidedfor:MemoryAcquisitionAlternateMemoryLocationsConvertingHibernationFilesandCrashDumpsMemoryArtifactTimeliningRegistryAnalysisPluginsRemembertoopencommandpromptasAdministratorwinpmem-oOutputfilelocation-pIncludepagefile-eExtractrawimagefromAFF4file-lLoaddriverforlivememoryanalysisC:\>winpmem_.
exe-oF:\mem.
aff4C:\>winpmem_.
exeF:\mem.
aff4-ePhysicalMemory-omem.
rawDumpIt/fOutputfilelocation/sHashfunctiontouse/tSendtoremotehost(setuplistenerwith/l)C:\>DumpIt.
exe/fF:\mem.
raw/s1MemoryAcquisitionHibernationFileCompressedRAMImage;availableinVolumeShadowCopies%SystemDrive%\hiberfil.
sysPageandSwapFiles%SystemDrive%\pagefile.
sys%SystemDrive%\swapfile.
sys(Win8+\2012+)MemoryDump%WINDIR%\MEMORY.
DMPAlternateMemoryLocationsMemoryForensicsCheatSheetv2.
0POCKETREFERENCEGUIDESANSInstitutebyChadTilburyhttps://digital-forensics.
sans.
orghttp://forensicmethods.
comhivelist-Findandlistavailableregistryhives#vol.
pyhivelisthivedump-Printallkeysandsubkeysinahive-oOffsetofregistryhivetodump(virtualoffset)#vol.
pyhivedump–o0xe1a14b60printkey-Outputaregistrykey,subkeys,andvalues-K"Registrykeypath"#vol.
pyprintkey–K"Microsoft\Windows\CurrentVersion\Run"dumpregistry-Extractallavailableregistryhives-oExtractusingvirtualoffsetofregistryhive--dump-dirDirectorytosaveextractedfiles#vol.
pydumpregistry--dump-dir.
/outputuserassist-Findandparseuserassistkeyvalues#vol.
pyuserassisthashdump-DumpuserNTLMandLanmanhashes#vol.
pyhashdumpautoruns-MapASEPstorunningprocesses-vShoweverything#vol.
pyautoruns-vRegistryAnalysisPluginsConvertingHibernationFilesandCrashDumpsimagecopy-Convertalternatememorysourcestoraw-fNameofsourcefile-OOutputfilename--profileSourceOSfromimageinfo#vol.
pyimagecopy-fhiberfil.
sys-Ohiber.
raw--profile=Win7SP1x64#vol.
pyimagecopy-fMEMORY.
DMP-Ocrashdump.
raw–-profile=Win2016x64_14393ExtractProcesses,Drivers,andObjectspslist-Highlevelviewofrunningprocesses#vol.
pypslistpsscan-ScanmemoryforEPROCESSblocks#vol.
pypsscanpstree-Displayparent-processrelationships#vol.
pypstreeIdentifyRogueProcessespsxview-Findhiddenprocessesusingcross-view#vol.
pypsxviewmodscan-Scanmemoryforloaded,unloaded,andunlinkeddrivers#vol.
pymodscanapihooks-FindAPI/DLLfunctionhooks-pOperateonlyonspecificPIDs-QOnlyscancriticalprocessesandDLLS#vol.
pyapihooksssdt-HooksinSystemServiceDescriptorTable#vol.
pyssdt|egrep–v'(ntoskrnl|win32k)'driverirp-IdentifyI/ORequestPacket(IRP)hooks-rAnalyzedriversmatchingREGEXnamepattern#vol.
pydriverirp–rtcpipidt-DisplayInterruptDescriptorTable#vol.
pyidtCheckforSignsofaRootkitdlldump-ExtractDLLsfromspecificprocesses-pDumpDLLsonlyforspecificPIDs-bDumpDLLusingbaseoffset-rDumpDLLsmatchingREGEXname--dump-dirDirectorytosaveextractedfiles#vol.
pydlldump--dump-dir.
/output–rmetsrvmoddump-Extractkerneldrivers-bDumpdriverusingoffsetaddress(frommodscan)-rDumpdriversmatchingREGEXname--dump-dirDirectorytosaveextractedfiles#vol.
pymoddump--dump-dir.
/output–rgaopdxprocdump-Dumpprocesstoexecutablesample-pDumponlyspecificPIDs-oSpecifyprocessbyphysicalmemoryoffset-nUseREGEXtospecifyprocess--dump-dirDirectorytosaveextractedfiles#vol.
pyprocdump--dump-dir.
/output–p868memdump-Extracteverymemorysectionintoonefile-pDumpmemorysectionsfromthesePIDs-nUseREGEXtospecifyprocess--dump-dirDirectorytosaveextractedfiles#vol.
pymemdump–-dump-dir.
/output–p868filescan-ScanmemoryforFILE_OBJECThandles#vol.
pyfilescandumpfiles-ExtractFILE_OBJECTsfrommemory-QDumpusingphysicaloffsetofFILE_OBJECT-rExtractusingaREGEX(add-iforcaseinsensitive)-nAddoriginalfilenametooutputname--dump-dirDirectorytosaveextractedfiles#vol.
pydumpfiles-n-i-r\\.
exe--dump-dir=.
/svcscan-ScanforWindowsServicerecordstructures-vShowserviceDLLforsvchostinstances#vol.
pysvcscan-vcmdscan-ScanforCOMMAND_HISTORYbuffers#vol.
pycmdscanconsoles-ScanforCONSOLE_INFORMATIONoutput#vol.
pyconsolesnetscan-ScanforTCPconnectionsandsockets#vol.
pynetscanNote:UseconnscanandsockscanforXPsystemsReviewNetworkArtifactsdlllist-Listofloadeddllsbyprocess-pShowinformationonlyforspecificprocesses(PIDs)#vol.
pydlllist–p1022,868getsids-Printprocesssecurityidentifiers-pShowinformationonlyforspecificPIDs#vol.
pygetsids–p868handles-Listofopenhandlesforeachprocess-pShowinformationonlyforspecificPIDs-tDisplayonlyhandlesofacertaintype{Process,Thread,Key,Event,File,Mutant,Token,Port}#vol.
pyhandles–p868–tFile,KeyAnalyzeProcessDLLsandHandlesmalfind-Findinjectedcodeanddumpsections-pShowinformationonlyforspecificPIDs-oProvidephysicaloffsetofsingleprocesstoscan--dump-dirDirectorytosavesuspiciousmemorysections#vol.
pymalfind--dump-dir.
/output_dirldrmodules-DetectunlinkedDLLs-pShowinformationonlyforspecificPIDs-vVerbose:showfullpathsfromthreeDLLlists#vol.
pyldrmodules–p868-vhollowfind-Detectprocesshollowingtechniques-pShowinformationonlyforspecificPIDs-DDirectorytosavesuspiciousmemorysections#vol.
pyhollowfind-D.
/output_dirLookforEvidenceofCodeInjectionGettingHelp#vol.
py–h(showoptionsandsupportedplugins)#vol.
pyplugin–h(showpluginusage)#vol.
pyplugin--info(showavailableOSprofiles)SampleCommandLine#vol.
py-fimage--profile=profilepluginIdentifySystemProfileimageinfo-Displaymemoryimagemetadata#vol.
py–fmem.
imgimageinfoUsingEnvironmentVariablesSetnameofmemoryimage(takesplaceof-f)#exportVOLATILITY_LOCATION=file:///images/mem.
imgSetprofiletype(takesplaceof--profile=)#exportVOLATILITY_PROFILE=Win10x64_14393GettingStartedwithVolatility
Megalayer美国独立服务器新用户首月优惠350元(30M优化不限流量)
Megalayer 商家在开始看到有提供香港服务器、香港站群服务器的时候有介绍过,后来就一直没有怎么关注。但是前几天有看到网友使用到他们家的美国独立服务器问其如何的,但是我没有使用过就不好评论,这不前几天也有介绍到Megalayer美国独立服务器。以及我们也有看到商家有提供美国站群服务器和美国大带宽服务器产品,可选30M不限制流量CN2优化线路,以及100M不限制流量国际带宽线路。新年元旦后,Me...

DogYun香港BGP月付14.4元主机简单测试
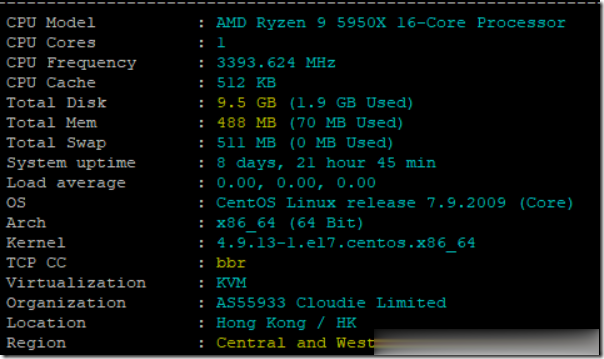
前些天赵容分享过DogYun(狗云)香港BGP线路AMD 5950X经典低价云服务器的信息(点击查看),刚好账户还有点余额够开个最低配,所以手贱尝试下,这些贴上简单测试信息,方便大家参考。官方网站:www.dogyun.com主机配置我搞的是最低款优惠后14.4元/月的,配置单核,512MB内存,10GB硬盘,300GB/50Mbps月流量。基本信息DogYun的VPS主机管理集成在会员中心,包括...
爱用云互联租用服务器租美国、日本、美国、日本、购买2天内不满意可以退换,IP可免费更换!
爱用云互联怎么样?爱用云是一家成立于2018年的老牌商家旗下的服务器销售品牌,是正规持证IDC/ISP/IRCS商家,主要销售国内、中国香港、国外服务器产品,线路有腾讯云国外线路、自营香港CN2线路等,都是中国大陆直连线路,非常适合免备案建站业务需求和各种负载较高的项目,同时国内服务器也有多个BGP以及高防节点。专注为个人开发者用户,中小型,大型企业用户提供一站式核心网络云端服务部署,促使用户云端...
hiberfil为你推荐
-
简体翻译成繁体简体字怎么换成繁体。。?人人时光机寻时光机歌词缓冲区溢出教程溢出攻击原理1433端口1433端口怎么打开硬盘人上海人说“硬盘”是什么梗人人逛街包公免费逛街打一成语商标注册查询官网商标注册查询官方网站?网页打开很慢如何解决网速正常 网页打开很慢问题网页打开很慢为什么打开网页很慢怎么上传音乐怎么上传音乐到网上